同樣地,核心 Siri 限制——包括 允許 Siri (Allow Siri)、強制 Siri 不雅用語過濾器 (Force Siri Profanity Filter) 和 鎖定時允許輔助 (Allow Assistant while Locked)——也已移轉至 DDM。現在為受監督裝置提供了一項新限制:允許 Siri 使用者產生的網頁內容 (Allow Siri User-Generated Web Content)。
Scalefusion 的 macOS 應用程式目錄為 IT 團隊提供了一個集中化的方式來處理第三方應用程式分發,減少了複雜性和行政管理工作量。
macOS 應用程式目錄通過進階功能簡化了應用程式管理,包括應用程式的靜默安裝、提供自助服務目錄讓使用者可按需從超過 400 個經批准的應用程式列表中進行安裝,以及自動後台更新以確保第三方應用程式的安全性和合規性。此外,可自訂的安裝行為使 IT 團隊能夠配置工作流程、應用特定設置,並高效管理應用程式版本。
「一如既往,我們在 Scalefusion 的使命是為 IT 團隊提供減少複雜性並提高效率的工具。隨著 macOS 應用程式目錄的推出,我們讓第三方應用程式管理變得更高效,減少了 IT 團隊的時間消耗。我們的目標是幫助 IT 團隊節省時間,確保 IT 管理員和最終使用者都能擁有順暢的體驗,」Scalefusion 產品與增長副總裁 Spurti Preetham Gurram 表示。
網絡安全多針對外部威脅,但內部威脅同樣危險,甚至更甚。2019 年 Ponemon Institute 的報告(註三)指出,內部攻擊的平均成本每年達 1,145 萬美元。內部威脅源於員工、承包商或受信任合作夥伴濫用存取權限。零信任驗證持續監控使用者行為,標記可疑或異常活動。透過執行嚴格的存取控制與即時異常偵測,零信任降低了內部威脅的風險,並有助於迅速減輕潛在危害。
橫向攻擊:來自外部的無聲移動
內部威脅源於受信任的個人,而橫向攻擊則是由已入侵網絡的外部攻擊者發動。這些攻擊者策略性地移動,利用漏洞或被盜憑證。2020 年 IBM 的報告(註四)顯示,60% 的資料外洩涉及橫向移動。零信任驗證持續監控攻擊者移動,執行嚴格的存取控制並驗證每個請求。這可防止橫向攻擊者存取敏感資料,並隔離受損帳戶,使攻擊者難以升級權限或在網絡中隱匿移動。
當您尋求一個能有效管理 Apple 生態系統 —— 包括 MacBook、iPad 和 iPhone 的工具時,Scalefusion 憑藉其直觀的介面和簡單的設定流程脫穎而出。不需要陡峭學習曲線的解決方案極具價值,而 Scalefusion 正是這樣一個選擇。它不僅限於 Apple 設備,還能管理多種平台的設備,包括 Windows、macOS、Android、iOS、Linux 和 ChromeOS,為使用多樣化設備的企業提供了顯著優勢。
Scalefusion 通過與 Apple Business Manager(ABM)和 Apple School Manager(ASM)的無縫整合,簡化了 Apple 設備管理。ABM 改變了工作場所的設備管理方式,使 Apple 設備的部署和控制更加輕鬆;而對於教育機構,ASM 則提升了行政效率,讓學校能更專注於教育本身。無論是商業還是教育用途,Scalefusion 都能確保 Apple 設備管理的輕鬆與高效。
其全面的功能組合和卓越的客戶支援是 Scalefusion 的突出之處,這在管理多樣化設備時尤為重要。它提供從單一平台管理 Apple 和非 Apple 設備的靈活性,成為一個多功能且實用的選擇,滿足不同規模企業的需求。
Scalefusion的主要功能:
基於 Apple ID 的註冊
FileDock 遙距推送和管理內容
基於角色的存取控制
Apple Business Manager 整合
單應用和多應用 kiosk 模式
配置限制和更新排程
網頁內容過濾
自動化作業系統更新
為什麼選擇Scalefusion?
與 Apple Business Manager 無縫整合:簡化設備管理,讓 Apple 設備的部署和控制更加順暢。
Doesn’t switching systems feel like moving into a new house? Exciting but stressful. It’s a delicate balancing act of packing up, ensuring nothing is lost and setting up the new place just right.
That’s how it feels for IT admins and businesses when migrating from one device management solution to another. To state the obvious, migration isn’t easy. IT teams face hours of troubleshooting, while employees endure workflow disruptions.
Out with JumpCloud In with Scalefusion Migration Done Right
To solve this problem, Scalefusion UEM steps in to transform the migration experience, offering a seamless, secure, and efficient way to manage devices without the usual complexities.
JumpCloud has been a reliable choice for many businesses, but as organizations scale, they often realize they need something more—a solution that’s not just functional but designed to simplify device management without compromising on flexibility, security, or productivity.
Keep reading to explore how Scalefusion makes the migration process easier and more efficient.
Why make the switch from JumpCloud MDM to Scalefusion?
JumpCloud has served many organizations well, but as the demand for more robust features and flexibility grows, Scalefusion takes things up and elevates the experience.
Here’s why switching to Scalefusion makes perfect sense.
Better features and capabilities
Scalefusion brings together Unified Endpoint Management (UEM), Identity and Access Management (IAM), and Endpoint Security under one unified platform. This integration means no more hustling between multiple systems, offering a streamlined solution that covers everything from security to productivity.
Advanced policy management
With Scalefusion, you gain granular control over device configurations. Set up policies tailored to specific user groups, departments, or even individual devices, ensuring the right level of control at every level.
Cost-effectiveness
Scalefusion delivers more than just powerful features—it’s designed to enhance your bottom line. With flexible pricing models and clear ROI, businesses can reduce operational costs while getting more out of their device management solution.
Multi-OS scalability
Scalefusion is built to handle complex multi-OS environments. Scalefusion offers support for Windows, Android, macOS, iOS, ChromeOS and Linux. It ensures seamless integration and scalability across all platforms, allowing your organization to operate smoothly, no matter the mix of devices in use.
Interoperability
Whether you’re integrating with Active Directory, legacy systems, or managing a variety of devices, Scalefusion offers smooth interoperability and a single interface to oversee everything.
Comprehensive Zero-Trust security
For Scalefusion, security is on its priority list. With its zero-trust security framework, Scalefusion ensures that devices, data, and applications remain secure, no matter where employees are working.
A side-by-side look: JumpCloud vs Scalefusion
Key Features
JumpCloud
Scalefusion
Multi-Platform Support
No
Yes
Android Enterprise Recommended
No
Yes
Advanced Platform Security
No
Yes
Advanced Diagnostics
Yes
Yes
Device Trust with Conditional Access (Location, IP Address, Day/Time)
No
Yes
Remote Cast & Control with VoIP Calling
No
Yes
Login with any IdP* on PC & Mac*: GWS/Entra/Okta/PingOne/Microsoft AD
No
Yes
PIM with Just-In-Time Admin for PC & Mac
No
Yes
Automated SSO configuration assignment: For supported providers
No
Yes
Location Tracking & Geofencing
Yes
Yes
Dynamics Groups
No
Yes
Automatic user account provisioning, domain & password sync for PC & Mac
No
Yes
Custom Login screen for PC & Mac
No
Yes
App Management
Yes
Yes
ROM Based Enrollment
No
Yes
In-Built Browser
No
Yes
Learning Curve
9-10 Hours +
4 Hours
Website Control on Edge
No
Yes
Single-app Kiosk Mode
No
Yes
Custom Branding
No
Yes
Conditional Email Access
Yes
Yes
Windows Autopilot Enrollment
No
Yes
Windows Entra/Azure Enrollment
No
Yes
Free Trial
Yes (With limited features)
Yes (With all the features included)
Windows Multi-App and Single App Kiosk mode
No
Yes
Windows Custom Payload option
No
Yes
Execute Shell script
No
Yes
Steps to migrate from JumpCloud to Scalefusion
1. Pre-migration
The first step in any successful migration is preparation. Before migrating from JumpCloud to Scalefusion, take the time to assess your organization’s current setup and define your migration goals.
Assess your devices and users: Make a list of all devices and users across your organization.
Categorize devices: Group devices based on type and operating system.
Define feature requirements: List the features and capabilities you require in your new MDM solution, such as advanced security policies or remote device management.
Review and update policies: Ensure that your current policies are aligned with the organization’s future needs.
Backup data: Back up all critical business data to ensure nothing is lost during the migration.
Prepare a migration plan: Create a comprehensive migration plan and communicate it with stakeholders.
Employee communication: Inform employees about the upcoming migration and guide them through the enrollment process.
Unenroll devices from JumpCloud: Ensure all devices are unenrolled from JumpCloud before starting the migration.
2. Migration
Now it’s time to execute the migration.
Sign up and set up Scalefusion:Register for a Scalefusion account and configure your organization’s profile.
Assign roles: Designate roles for your IT admins and other team members, ensuring that everyone has the correct permissions.
Create and implement policies: Define business policies and push them to all devices remotely.
Choose your enrollment method: Depending on the number of devices and their OS types, select the most appropriate bulk enrollment option for your organization.
Integrate directory services: Use Scalefusion’s directory integration tools to import user data in bulk, syncing directly from your current systems.
3. Post-migration
After completing the migration, it’s crucial to confirm that everything is running smoothly and that your devices are properly managed by Scalefusion.
Verify device enrollment: Ensure all devices are fully migrated from JumpCloud and are now enrolled in Scalefusion.
Check policy implementation: Confirm that the newly implemented policies are functioning correctly across all devices.
Run system checks: IT admins should verify that all JumpCloud services are unsubscribed and that Scalefusion is fully managing the devices.
Gather feedback: Collect feedback from your IT team and employees to ensure the migration went smoothly and identify any potential issues.
Reach out for support: If you encounter any issues or need assistance, Scalefusion’s product specialists are available to provide support and resolve any concerns.
Addressing end-user challenges during migration
1. IT admin overload
Problem: Migration often requires IT teams to manually configure devices, set up user groups, and apply policies, leading to increased workload and potential errors.
Solution: Scalefusion automates these tasks, simplifying workflows and allowing IT admins to focus on higher-priority responsibilities.
2. High costs
Problem: Traditional migrations can be costly, requiring additional resources, consultants, and extended timelines.
Solution: Scalefusion reduces costs by providing an all-in-one platform with clear, affordable pricing and eliminating the need for extra resources during migration.
3. Time-consuming
Problem: Migrations can drag on for weeks, resulting in unnecessary delays and extended disruptions.
Solution: Scalefusion offers an automated, step-by-step process that speeds up migration, ensuring minimal delays and a faster transition.
4. Impact on productivity
Problem: Employees may face downtime or workflow disruptions while devices are being migrated and reconfigured.
Solution: Scalefusion minimizes disruption by allowing employees to continue working during the migration process, with devices configured in the background.
5. Remote worker challenges
Problem: Managing and configuring devices for remote workers can be difficult, especially if they’re scattered across locations.
Solution: Scalefusion supports remote device management, enabling IT to configure and support devices for remote workers without the need for physical access.
6. Risk of failures and delays
Problem: Data transfers and system integrations can fail, leading to delays and incomplete migrations.
Solution: Scalefusion ensures secure and validated data transfer, reducing the risk of errors and preventing delays with continuous migration monitoring.
7. Compatibility and data loss risks
Problem: Migrations often result in compatibility issues or data loss during the transition between platforms.
Solution: Scalefusion guarantees smooth integration with existing systems and ensures that all data is securely transferred without any loss.
Scalefusion’s support and resources
Scalefusion combines expert support with practical tools to make migrations smooth, efficient, and stress-free.
1. Expert assistance – Receive step-by-step guidance through every stage of the migration process, ensuring a smooth transition with minimal disruptions.
2. Comprehensive knowledge base – Access a library of resources, including detailed guides and platform tutorials, to simplify both migration and device management.
3. 24/6 support – Beyond migration, Scalefusion offers continuous assistance via chat, email, and calls, ensuring ongoing device management is effortless and issues are resolved promptly.
Take the next step: Migrate with Scalefusion
Switching from JumpCloud to Scalefusion doesn’t have to be a complicated process. Scalefusion streamlines migrations with automation, robust compatibility, and features tailored for businesses of all sizes. By reducing IT workload, minimizing downtime, and ensuring data integrity, Scalefusion makes device management seamless and efficient.
Scalefusion’s unified platform, advanced policies, and remote-friendly tools make it a seamless, secure, and cost-effective alternative to JumpCloud for scaling businesses.
Ready to make the switch? Contact our support team today to get started and experience the ease of migrating to Scalefusion.
About Scalefusion Scalefusion’s company DNA is built on the foundation of providing world-class customer service and making endpoint management simple and effortless for businesses globally. We prioritize the needs and feedback of our customers, making sure that they are at the forefront of all decision-making processes. We are dedicated to providing comprehensive customer support services, and place emphasis on customer-centric thinking throughout the organization.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
How many Apple devices are in your workplace, school, or home right now?
Do you rely on an iPhone to manage your day, or perhaps a MacBook for work?
Ever wonder how many other people in the world are doing the same?
With 2.2 billion active Apple devices globally, the answer is: a lot.[1]
Apple Endpoint Management
From students browsing away on iPads to businesses running on Macs, Apple’s devices have seamlessly infiltrated our daily lives, becoming indispensable tools for productivity, creativity, and communication. But here’s the catch—as Apple’s influence grows, so does the complexity of managing these devices.
So, who’s in charge of keeping all these devices secure? How do you ensure compliance, prevent data breaches, and keep devices running smoothly—without a team of IT experts working overtime?
The answer lies in Apple Unified Endpoint Management (UEM). It’s the solution that simplifies the complexity of managing Apple devices, ensuring they remain secure, updated, and aligned with organizational policies. Whether it’s a CEO’s iPhone or a classroom full of iPads or you need to manage 10 devices or 10,000, UEM offers the structure needed to oversee a growing ecosystem.
So, how UEM for Apple can transform your device management? Let’s find out.
What is UEM, and why does Apple need it?
Managing a bunch of Apple devices without the right tools is a tricky balancing act. Basic controls aren’t enough. Unified Endpoint Management helps by offering a centralized platform that brings order to the complexity of managing Apple devices (along with other OSs), empowering IT teams to configure, secure, and monitor them all with ease.
Apple mobile device management makes sure every iPhone, iPad, and MacBook operates in sync with organizational needs. From ensuring software is up to date, to secure data, to control what users can and can’t do on their devices, UEM does it all. The better you manage your devices, the smoother your operations will run.
Apple and UEM: A perfect match for every industry
What makes Apple such a great choice across all these industries, and how does UEM play a role in managing them effectively?
Healthcare: Protecting patient data
According to a 2024 KLAS report, 64% of healthcare organizations use Apple devices, making them the most used commercial devices in healthcare.[2] Doctors and nurses rely on iPads and iPhones for accessing patient records, prescribing medications, and communicating within the hospital. UEM ensures that these devices remain HIPAA-compliant and secure, with features like device encryption and secure app management. UEM also allows healthcare organizations to monitor and restrict access to patient data, ensuring that only authorized personnel can view sensitive information.
Education: Managing classrooms of iPads
Schools and universities have embraced Apple devices for education, using iPads, Macs, and even Apple TVs to enhance learning. With Apple UEM, institutions can easily manage a large number of devices, controlling what apps and content are accessible to students. UEM allows schools to roll out software updates, enforce security policies, and ensure that devices are used for educational purposes —preventing distractions like unauthorized browsing or gaming during class.
BFSI: Securing sensitive data
Financial institutions need to ensure that their Apple devices are secure and compliant with industry standards. UEM allows financial firms to manage apps, control data access, and track devices, all while ensuring that they meet compliance requirements like GDPR. By controlling the entire Apple ecosystem, UEM protects sensitive financial data and reduces the risk of costly breaches. Leveraging Apple for BFSI, UEM ensures a secure and compliant environment tailored for the financial sector.
Retail: Seamless operations
In retail, Apple devices are used for everything from managing inventory to running point-of-sale (POS) systems. UEM simplifies the management of these devices, enabling retail businesses to deploy, update, and secure their devices without disrupting operations. With UEM, retailers can ensure that all devices are always up to date with the latest software, providing a seamless experience for both employees and customers.
Key concepts in Apple device management
Before we explore the specific benefits of UEM for Apple devices, it’s important to understand some of the foundational concepts that drive effective device management. These concepts set the stage for why UEM is essential for organizations looking to manage and secure Apple devices at scale.
1. Device supervision: A higher level of control
Device supervision is a critical mode for managing Apple devices in business, education, and institutional settings. When Apple devices are in supervision mode, IT teams gain access to a broader set of controls, features, and configurations, far beyond what is available on unsupervised devices.
For organizations, this level of control means better security, consistent device configurations, and the ability to customize devices according to their specific use cases—whether it’s an employee’s iPhone, a classroom of iPads, or interactive kiosks in retail or hospitality settings. Supervision is achieved through the Device Enrollment Program (DEP) as the primary method, or using tools like Apple Configurator 2 (AC2).
2. Apple Configurator 2: The deployment powerhouse
For large-scale deployments, Apple Configurator 2 is an indispensable tool. This macOS application enables organizations to configure, deploy, and manage multiple Apple devices simultaneously, ensuring that they are ready for use across various environments. Whether you need to supervise a batch of devices or enforce a particular configuration, Apple Configurator 2 is designed for efficiency.
In a UEM context, Apple Configurator 2 enables unsupervised devices to be enrolled into a management system by preparing them for deployment via DEP. It integrates with UEM solutions to configure settings, install profiles, and enforce business-specific requirements, making it ideal for organizations managing high device volumes or frequent turnover.
3. Apple ID vs. Managed Apple ID: Personal vs. organization-wide access
An Apple ID is typically associated with personal use, allowing users to access a variety of Apple services, including iCloud, app purchases, and data synchronization across devices. In an organizational setting, however, an Apple ID can quickly blur the line between personal and work-related use, potentially creating security risks and management complexities.
Managed Apple IDs provide businesses, schools, and government agencies with centralized control and enforced security settings on BYO devices. They maintain data privacy, streamline app distribution, and simplify device management, making them essential for organizations prioritizing secure Apple device usage.
4. APNs: Enabling secure communication between devices and apps
Apple Push Notification Service (APNs) acts as a bridge for delivering push notifications to devices. APNs ensures that any important updates, alerts, or information are securely delivered to iOS, iPadOS, macOS, and watchOS devices in real-time.
For organizations utilizing UEM for Apple, APNs is an essential feature. Not only does it facilitate secure communication between apps and users, but it also allows UEM solutions like Scalefusion to push updates, enforce policies, and notify users about device status, security alerts, or compliance requirements.
In a business context, APNs can be leveraged to ensure that the right messages reach the right devices, whether it’s a security alert, a device configuration change, or a software update.
5. Apple Declarative Device Management: Simplifying and Streamlining Control
Apple Declarative Device Management (DDM) takes device management to the next level by introducing a more proactive and streamlined approach. Apple DDM operates on a declarative model where devices are configured to know their desired state in advance.
This innovative method reduces back-and-forth communication with servers, making updates faster and more efficient. It also ensures devices can proactively adapt to new configurations, even in high-turnover environments.
For organizations using UEM, DDM offers a significant advantage by improving scalability and responsiveness. IT teams can push policies and settings more effectively, ensuring Apple devices remain compliant, secure, and aligned with business objectives.
How UEM simplifies Apple device management
Now that we’ve gone over the basics, let’s see how UEM makes managing Apple devices easier. Apple Business Manager (ABM) helps with setup and provisioning, but it’s UEM that steps in to handle the day-to-day management, secure the devices, and keep everything running smoothly.
With Apple UEM, this job gets a lot easier.
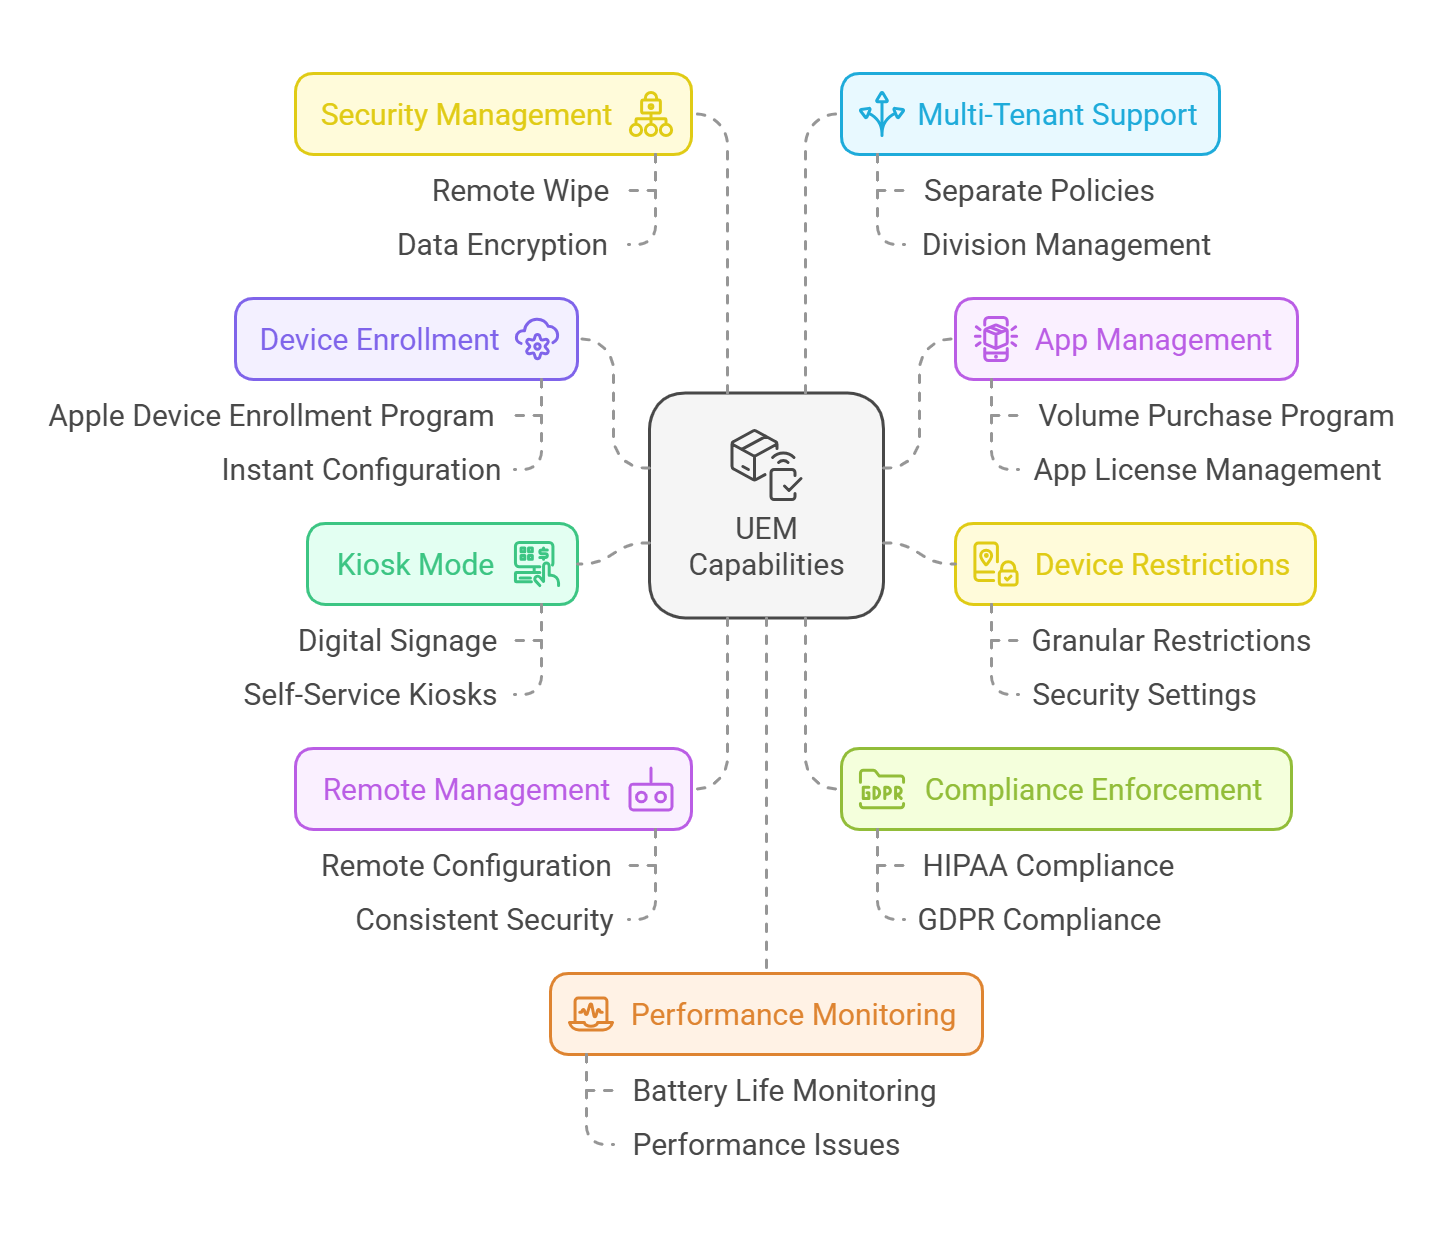
Apple device enrollment program (DEP): Automates the enrollment of devices, allowing IT teams to set up Apple devices straight out of the box. This streamlines large-scale deployments and ensures devices are instantly configured and ready for use without manual intervention.
Volume purchase program (VPP): Enables bulk purchasing and distribution of apps across multiple Apple devices. This feature allows organizations to easily manage app licenses and ensure that every device has the necessary software installed, updated, and maintained.
Granular device restrictions: UEM provides the ability to implement precise device restrictions, such as limiting access to specific apps, disabling certain features (e.g., camera or AirDrop), and enforcing security settings to align with organizational policies. This is crucial in environments like healthcare, retail, or education, where device usage needs to be controlled.
Kiosk mode: UEM allows devices to be locked down into a specific app or set of apps, turning them into dedicated kiosks. This is perfect for situations like digital signage in retail or self-service checkouts, where devices are meant to serve a single purpose and require strict usage control.
Remote configuration, support, and management: IT admins can remotely configure settings, manage devices, and apply updates across all Apple devices, eliminating the need for on-site support and making it easier to maintain consistency in configurations and security policies.
Compliance enforcement: UEM helps ensure compliance with industry standards such as HIPAA, GDPR, and PCI-DSS by enforcing security policies like encryption, password complexity, and data protection. This is essential in sectors like healthcare, finance, and education where regulatory compliance is a priority.
Security management: UEM offers advanced security controls, such as remote wipe capabilities, device tracking, and data encryption, ensuring that if a device is lost or stolen, sensitive data remains protected and inaccessible.
Multi-tenant support: For managed service providers or businesses with different divisions, UEM can provide a multi-tenant architecture, allowing for the management of different Apple device fleets under one system, but with separate policies and configurations for each tenant.
Battery and performance monitoring: UEM offers real-time monitoring of device health, including battery life and overall performance, helping IT teams proactively address issues before they impact productivity.
How UEM improves endpoint security for Apple devices
There’s no end to data breaches, malware attacks, and insider threats but we can definitely prevent them with the help of a UEM solution. Endpoint security is the first line of defense when it comes to securing Apple devices within an organization.
UEM solutions enhance security through several key features:
Device Compliance and Granular Restrictions: UEM solutions enforce security policies such as password rules, encryption, OS updates, and app restrictions. These help ensure compliance with industry regulations (HIPAA, GDPR) while protecting sensitive data from unauthorized access.
Zero Trust Access: UEM platforms enable a zero-trust security framework, where only authenticated users and compliant devices are allowed access to corporate resources, minimizing the risk of unauthorized entry.
Remote Lock and Data Wipe: In the event of a lost or stolen device, UEM solutions allow IT admins to lock or wipe the device remotely, securing sensitive corporate data and preventing unauthorized access.
Secure Network Connectivity with VPN Integration: UEM solutions configure and enforce VPN settings on Apple devices to ensure secure connections, especially for remote workers. This is further strengthened with endpoint security features like split tunneling and traffic filtering.
Proactive Security with Automatic Updates: UEM solutions ensure that devices are always up to date with the latest OS versions and security patches, protecting against vulnerabilities associated with outdated software.
I/O Device Access Control for macOS: UEM platforms allow organizations to manage and restrict the use of external devices like USBs and peripherals, preventing unauthorized data transfers and enhancing security on macOS.
Apple devices, while known for their robust security features, still face potential threats—whether it’s a lost iPhone with sensitive business data or a compromised app on an iPad. UEM solutions like Scalefusion, when paired with endpoint security solutions like Veltar, create an unbreakable defense against these risks.
Why Scalefusion is ideal for Apple device management
Scalefusion goes beyond basic UEM features like supervision, app control, and compliance enforcement. It offers robust tools to simplify and enhance the management of macOS and iOS devices, making it a comprehensive solution for businesses.
Support for all your Apple devices – Scalefusion is compatible with a wide range of Apple devices, from iPhones and iPads to Mac computers. Whether you’re managing mobile devices or desktop setups, you can handle them all from one unified platform, streamlining operations.
Dive deep with DeepDive – From the Scalefusion dashboard, you can get quick, graphical insights into your device inventory. View key metrics like platform-wise enrollment, active/inactive devices, and license usage. This data allows you to make informed decisions and track your device fleet more effectively.
Top-notch security – Keeping your business data secure is non-negotiable, and Scalefusion goes above and beyond to protect it. With features like remote device locking, data wipe, and passcode enforcement, you can ensure Apple devices are always secure and compliant with your company’s policies.
Effortless enrollment – Thanks to integration with Apple’s Device Enrollment Program (DEP), setting up Apple devices is a breeze. Zero-touch enrollment allows you to quickly onboard devices without physical interaction, making the process both fast and hassle-free.
Kiosk Mode and App Control – Scalefusion’s Kiosk Mode lets you restrict Apple devices to just one app or a set of apps, preventing unauthorized access and ensuring the device is dedicated to its intended function.
Granular policy control with Groups and Subgroups – Scalefusion gives you the ability to manage devices at a granular level. By organizing devices into groups and subgroups, you can apply specific policies to different teams or departments, offering greater control and tailoring device settings based on organizational needs.
No-code IT Workflows – Streamline IT tasks by automating and scheduling actions without coding. Create task flows, set execution times, and maintain compliance effortlessly.
Remote Troubleshooting with Remote Cast and Control – With the Remote Cast and Control feature, IT teams can mirror a device’s screen in real-time and take full control of the device to resolve problems. This eliminates the need for physical access, reduces downtime, and ensures your team can quickly address issues.
Seamless integration with Apple’s ecosystem – Scalefusion seamlessly integrates with Apple’s native services, such as iCloud, iTunes, and Apple School Manager. This tight integration ensures smooth syncing of apps, data, and settings across your Apple devices, providing a unified experience for your business.
OS Updates and Patch Management – Scalefusion simplifies OS updates and patch management, automating the process to keep your Apple devices secure and up to date. Scalefusion UEM leverages Apple’s declarative device management (DDM) protocol to further streamline the update process. With DDM, you can schedule updates for macOS devices based on your local time zone, ensuring updates are applied at optimal times. This ensures that devices always install the latest version when multiple updates are available, simplifying the update management process.
Ensure long-term success with Apple UEM
With Apple devices becoming more prevalent across businesses, schools and industries, managing them efficiently is essential. Scalefusion UEM ensures your device management solution evolves alongside your organization, seamlessly adapting to the latest Apple updates.
Scalefusion UEM provides a seamless experience for managing Apple devices, with continuous updates that ensure compatibility with the latest Apple advancements. Its scalability allows organizations to easily manage growing numbers of Apple devices, while its interoperability ensures smooth integration with not just new Apple technologies and updates but also any other OS or device type that your business or employees love and use.
Get in touch with our experts for more details and book a free demo call. Start your 14-day free trial today, with full access to all features, and discover how easy device management can be!
About Scalefusion Scalefusion’s company DNA is built on the foundation of providing world-class customer service and making endpoint management simple and effortless for businesses globally. We prioritize the needs and feedback of our customers, making sure that they are at the forefront of all decision-making processes. We are dedicated to providing comprehensive customer support services, and place emphasis on customer-centric thinking throughout the organization.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
The gap between identifying vulnerabilities and applying patches continues to be a major bottleneck for organizations. In December 2024, the U.S. Treasury Department reported a breach attributed to a Chinese state-sponsored actor, who exploited two known vulnerabilities in BeyondTrust’s remote tech support software to gain unauthorized access[1].
Understanding the meaning of vulnerability and patch management
This incident makes us realize the importance of robust vulnerability and patch management strategies, especially now that we are entering the Year 2025. Both processes play crucial roles in securing IT systems, yet they serve distinct purposes and operate in tandem to safeguard organizational assets.
Let’s explore the fundamentals of vulnerability and patch management, their lifecycles, and how they complement each other to form the backbone of modern cybersecurity strategies. Read On-
Vulnerability vs. patch management: Understanding the basics
The first and most important thing to understand is that patch management is a process that comes within the broader scope of vulnerability management.
Vulnerability management is the process of identifying, assessing, categorizing, prioritizing, mitigating, and finally remediating vulnerabilities from an IT infrastructure. The aim here is to eliminate the security flaws, glitches, or weaknesses found in the system, which an attacker could exploit.
Conversely, patch management is the process of managing the action of patching the vulnerabilities. It identifies, prioritizes, tests, and deploys the patch to an operating system. Patching ensures that the devices run on the latest OS and app versions, addressing any kind of bug or vulnerability.
According to Jason Firch (CEO, PurpleSec), organizations can have vulnerability management without patch management, but they can’t have patch management without vulnerability management. One is dependent on the other[2].
Learning the mechanics of vulnerability and patch management
To understand how vulnerability and patch management work we will need to understand their lifecycles.
Patch management lifecycle
1. Build an inventory of production systems such as IP addresses, OS, and applications.
2. Scan the system for missing patches.
3. Create the patching policies according to your organizational needs.
4. Prioritize patches based on their severity.
5. Stage and test patches in a controlled environment.
6. Deploy patches to required devices, servers, and operating systems.
7. Verify patch deployment to ensure that they are not only installed but also working as intended.
8. Create patch reports under the company’s IT security policies and procedures documentation.
Vulnerability management lifecycle
1. Find and identify vulnerabilities that require patching.
2. Assess vulnerabilities and their levels of risk to the organization.
3. Prioritize vulnerabilities by identifying which ones to patch first for a relevant impact on your organization.
4. Apply a patch to remediate the vulnerability.
5. Review and assess the patched vulnerabilities.
6. Continue monitoring and reporting vulnerabilities for a better patching process.
The interplay between patch and vulnerability management
Patch management and vulnerability management are complementary processes that form the cornerstone of an organization’s cybersecurity strategy.
While vulnerability management sets the stage by highlighting security gaps that need to be addressed, patch management complements vulnerability management by addressing the identified security flaws.
Patch management reduces the attack surface and reinforces the security framework by systematically addressing vulnerabilities. The synergy between vulnerability and patch management lies in their shared objective of minimizing risk.
Feedback loop: Vulnerability assessments inform patch management teams about critical vulnerabilities that require immediate action. Post-patch deployment, vulnerability scans confirm whether the issues have been resolved.
Prioritization alignment: Vulnerability management helps prioritize which patches to apply first based on the risk level, ensuring high-risk vulnerabilities are addressed promptly.
Proactive defense: Continuous monitoring by vulnerability management ensures that emerging threats are detected, while patch management provides the means to neutralize them effectively.
Patch vs vulnerability management: The odds and evens
Effective cybersecurity strategies hinge on patch and vulnerability management, as these processes address critical aspects of IT security. While they share similar goals—reducing risks and maintaining system integrity—they follow distinct methodologies and scopes.
Similarities
a. Focus on reducing risks
Both patch management and vulnerability management aim to minimize security risks by addressing potential threats. Patch management achieves this by applying software updates, while vulnerability management identifies and mitigates weaknesses in the system infrastructure.
b. Lifecycle phases
Both processes share similar lifecycle stages, such as identification, prioritization, remediation, and validation. These stages ensure vulnerabilities and patches are systematically addressed to enhance security.
c. Dependency on accurate assessment
Accurate assessment is critical for both processes. Patch management relies on understanding software versions and available updates, whereas vulnerability management depends on thorough scans to detect potential weaknesses.
Key Differences
Aspect
Patch management
Vulnerability management
Scope
Addresses software and application updates.
Covers weaknesses in networks, hardware, and software.
Approach
Reactive: Fixes known issues.
Proactive: Finds and assesses potential risks.
Tools
Patch deployment tools, and automated update systems.
Scanners, penetration testing, and risk analysis tools.
Outcome
Measured by patches applied and compliance.
Focuses on risk reduction and improved security posture.
Integration
IT asset and change management processes.
Risk management, compliance, and incident response.
a. Scope of management
Patch management: Focuses specifically on deploying updates to software and applications, addressing known vulnerabilities by fixing bugs or enhancing features.
Vulnerability management: Takes a broader approach, identifying, analyzing, and mitigating weaknesses across the entire IT environment, including network configurations, hardware, and software.
b. Proactive vs. reactive
Patch management: Often reactive, as it addresses vulnerabilities already identified and fixed by software vendors.
Vulnerability management: Proactive, involving continuous scanning and monitoring to uncover vulnerabilities that may not yet have a patch available.
c. Tools and techniques
Patch management: Relies on patch deployment tools and update management systems to automate and schedule updates.
Vulnerability management: Uses vulnerability scanners, penetration testing, and risk analysis tools to identify and assess system weaknesses.
d. Outcome and metrics
Patch Management: Success is measured by the number of systems patched and compliance with update schedules.
Vulnerability Management: Metrics focus on risk reduction, such as the number of vulnerabilities mitigated and the overall security posture improvement.
e. Integration with other processes
Patch management: Primarily integrates with IT asset management and change management processes.
Vulnerability management: Aligns more broadly with risk management, compliance, and incident response plans.
Best practices for implementing patch and vulnerability management
Effective patch and vulnerability management is essential to maintaining a strong security posture and protecting against emerging cyber threats. By adhering to best practices, organizations can reduce the risk of security breaches, improve system performance, and ensure compliance with regulatory standards. Following are some key best practices for implementing a patch and vulnerability management program:
1. Establish a comprehensive inventory
Begin by creating and maintaining an up-to-date inventory of all hardware and software assets. This includes operating systems, applications, and network devices. Knowing what needs to be patched or updated is the first step in managing vulnerabilities effectively. Regularly audit and update the inventory to ensure you aren’t missing any critical systems.
2. Prioritize patches based on risk
Not all vulnerabilities are created equal. Some may pose a more immediate threat to your organization than others. Prioritize patches based on risk levels, considering factors such as the severity of the vulnerability, the criticality of the system, and any known exploits. A risk-based approach ensures that you address the most critical threats first, minimizing potential damage.
3. Automate patch deployment
Manual patching can be time-consuming and error-prone. Automated patching allows for faster, more consistent updates across your environment. With automated solutions, patches can be tested, approved, and deployed to all systems efficiently, reducing the likelihood of human error and ensuring timely updates.
4. Test patches before deployment
While automation helps streamline the process, it’s crucial to test patches in a controlled environment before deploying them across your production systems. Testing patches ensure they don’t disrupt business operations or introduce new issues. A test environment will help identify any compatibility or performance issues, so you can address them before widespread implementation.
5. Maintain a patch management schedule
Consistency is key when managing patches. Implement a regular patch management schedule that includes daily, weekly, or monthly checks for new patches. Having a routine process in place ensures that patches are applied promptly and helps organizations stay on top of new security vulnerabilities as they emerge.
6. Monitor and report vulnerabilities
Regularly monitor for new vulnerabilities and threats affecting your systems. Implement vulnerability scanning tools to identify potential weaknesses and gaps in your security posture. Once a vulnerability is discovered, generate detailed reports to help track remediation efforts and assess the effectiveness of your patching strategy.
7. Establish incident response protocols
Even with a solid patch management strategy, incidents can still occur. Ensure that you have clear and well-documented incident response protocols in place. This should include steps to take if a vulnerability is exploited, such as isolating affected systems, analyzing the breach, and applying emergency patches if necessary.
Ensure consistent protection with Scalefusion’s automated patch management
If you want to upgrade to an advanced patch management solution for your Windows devices and third-party applications, look no further. With Scalefusion UEM’s automated patch management, you can schedule, delay, automate, and deploy patches on your device, keeping them updated and protected from vulnerabilities at all times.
About Scalefusion Scalefusion’s company DNA is built on the foundation of providing world-class customer service and making endpoint management simple and effortless for businesses globally. We prioritize the needs and feedback of our customers, making sure that they are at the forefront of all decision-making processes. We are dedicated to providing comprehensive customer support services, and place emphasis on customer-centric thinking throughout the organization.
About Version 2 Digital
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.