Skip to content

【重要訊息公告】您的產品已過期

以下通知主要為ESET與Microsoft Windows有兼容性或是安全性更新之必要 以及由於ESET Management Agent的憑證將於今年年底過期,所以需升級到最新版本以避免產品品過期,須請您將ESET軟體利用手動或由ESMC更新成 v7.3或以上之新版本,排除以下狀況。

近期您的 ESET 軟體會顯示下列通知:

  • 若要在 Windows 7 上繼續使用我們的產品,請安裝導入 SHA2 代碼簽署支援的 Windows 更新 (請參考 Microsoft 的說明),然後在 2020 年 12 月前升級到 ESET 產品的最新版本。 查看您的選項: https://support-eol.eset.com/en/trending_vista_7.html
  • 您目前的產品版本即將不受 Microsoft Windows 10 支援。請於 2020 年 12 月前升級到版本 7.3 或更新版本,以繼續接受完整防護和特色功能。使用具有效性的授權,無須額外費用即可升級。 查看您的選項: https://support-eol.eset.com/en/trending_win_10.html
  • 您目前的ESET Management Agent已過期,不再完全相容您的安全性產品,請升級到版本7.2或更新版本,並確保您的ESET Security Managemente Center版本為7.2或更新版本,查看您的選項: https://support.eset.com/kb7465

➢ 手動更新:

ESET Endpoint Antivirus ESET Endpoint Security
新版載點 新版載點

※ Windows 7若無法安裝最新版本,請更新Windows KB4474419、KB4490628(說明)

➢ ESMC更新

  • 若您的電腦出現ESET Management Agent已過期,請依據下列步驟進行執行,由於agent程式建議需與主控台版本一致,所以主控台也需更新。
  • ERA版本升級到ESMC7.3版本的說明文件,詳細說明文件可點此 之後須注意由於ESMC的系統需求與ERA不相同,可先參考此表格
  • 若windows server 小於2012,則需新建立一個環境搭載新OS的伺服器來作安裝,後續再將設定遷移到新伺服器上(遷移工具說明)
  • 此外若ERA版本非6.5,建議您可先透過ERA的元件升級將版本升級到6.5後再作下列操作。 可參考(ERA6.x升級到6.5)
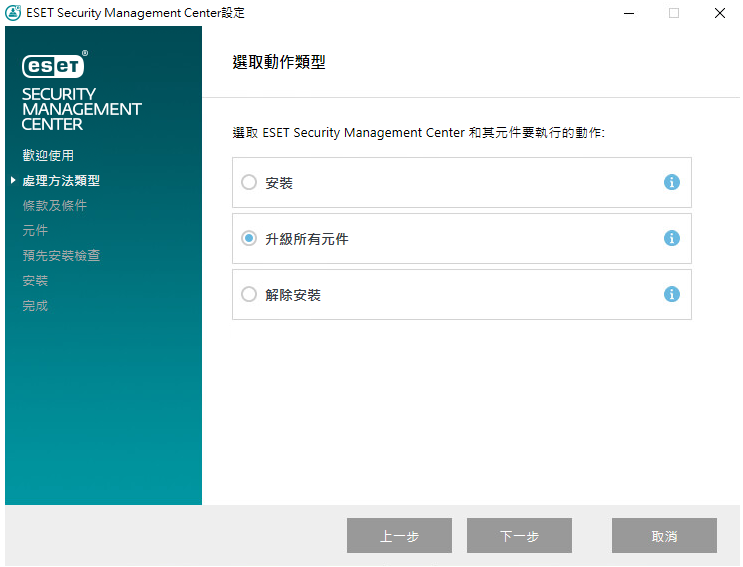
  • 到官網下載新版ESMC安裝包,執行後選擇升級ESMC All in one安裝包【安裝】→【升級所有元件】
  • ESMC升級注意事項可參考此篇文章說明
  • 須注意主控台升級時需將憑證匯出備份避免後續若發生錯誤時可以重新回復。
  • 資料庫備份之說明可參考資料庫伺服器備份/更新與 ESMC 資料庫遷移

➢ Agent更新:

Agent升級部分可參考元件升級部分,

圖1:【工作】→【新增】→【用戶端工作】→【工作:Security Management Center 元件升級】

圖2:之後進入觸發動作選擇目標電腦

即可進行agent更新。

➢ 用戶端防毒軟體更新:

圖1:【工作】→【新增】→【用戶端工作】→【工作:軟體安裝】

圖2:

圖3:點擊【建立觸發程序】

圖4:選擇要更新軟體之client端 【目標】→【新增電腦/群組】

用上述2種方式,將ESET軟體更新。若有其他問題將相關截圖傳送至:support@version-2.tw

ESET CEO理查德·馬科(Richard Marko)幫助網絡安全技術協議和聯合國辦事處帶來創新的數字解決方案,作為Apps 4 Digital Peace競賽小組的評委

Bratislava – Richard Marko, CEO of ESET, a global leader in cybersecurity, has been invited to judge the first-of-its-kind Apps 4 Digital Peace Competition organized by the Cybersecurity Tech Accord, the United Nations Office for Disarmament Affairs (UNODA), and the https://www.un.org/youthenvoy/.

The competition was created in response to the dramatic increase in the malicious use of information and technology by state and non-state actors. Given the possible threat to international peace and security, these organizations felt a need to encourage the brightest young minds to help develop technology solutions to limit the use of the internet as a domain of conflict, and to increase the security and stability of our online environment.

Through ESET’s involvement as a signatory of the Cybersecurity Tech Accord, Mr. Marko will join a panel of distinguished judges to help stimulate new and ethical thinking from young innovators across the world. The other members of the panel are Alex Stamos, director, Stanford Internet Observatory and former Facebook CISO; Damir “Gaus” Rajnovic, cybersecurity manager of Panasonic; Kim Zetter, award-winning journalist covering cybersecurity and national security issues; Liis Vihul, CEO, Cyber Law International; and Jayathma Wickramanayake, the UN Secretary General’s Envoy on Youth.

Five finalists are in the running to receive both cash prizes and networking opportunities that will help get their ideas off the ground. The winners will be invited to attend the Cybersecurity Tech Accord’s annual meeting to present their Apps 4 Digital Peace submission to some of the world’s leading technology companies committed to improving security online for users everywhere.

“It is a privilege to serve on the judging panel for the first-ever Apps 4 Digital Peace Competition,” said Mr. Marko. “At ESET we are passionate about making technology safer for everyone, and we are proud to empower the leaders of tomorrow in creating and developing innovative solutions that promote digital peace.”

“I’m excited to see what these bright, young minds create to tackle the many challenges that the cyber world brings,” said Tony Anscombe, Chief Security Evangelist at ESET. “Our youth innovators are the future of cybersecurity. Their contributions will help form cyber hygiene practices, protect infrastructure and promote responsible online behavior, creating a positive impact in our online world.”   

The Apps 4 Digital Peace Competition Virtual Award Ceremony will take place on September 21 from 10:00 am to 12:00 pm EDT. Click here to register to watch the ceremony.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

ESET的新總部和校園將由丹麥領先的建築工作室BIG(Bjarke Ingels Group)設計

BRATISLAVA – ESET has named its partner in transforming the premises of the former Military Hospital at Patrónka into the Center for Innovation and Creativity – ESET Campus – the world-renowned architectural studio Bjarke Ingels Group (BIG). Architects from one of today’s most sought-after studios have won the international architectural competition that was announced by ESET last September. As ESET Campus is an exceptional project in terms of scope but especially the combination and interconnectedness of functions, the most important selection criteria were previous experience with a focus on master planning, campuses and innovation centers, but also sufficient studio size and capacity.

“We also see ESET Campus as an extremely complex project for our company, which is why we paid a lot of attention and time to the choice of the conceptual architect. The international competition and workshops with the addressed studios, as well as discussions with Slovak experts who helped us with the selection, significantly moved us not only in thinking about the future design of the project, but also on current topics such as sustainability, ecology and flexibility of the working environment. In addition, we are preparing this exceptional project at a time that posed completely new challenges for us, so I am very happy that we will develop it with exceptional architects from the BIG studio,” said Pavel Luka, ESET’s chief operating officer, about the results of the competition.

“We are honoured to work with ESET, which has set out an extraordinary level of ambition for their new headquarters. With the global events of 2020 and the rise of remote working in mind, this has become an opportunity to explore the future of both physical and virtual work space, and to rethink the campus as an integrated part of the city. The vision is to demonstrate a true carbon neutral approach to construction, and to create a campus blended closely with the natural environment at the foot of the Small Carpathians,” said Andreas Klok Pedersen, partner, BIG London.

As the intention of the competition was the presentation of conceptual proposals and the selection of a long-term partner for cooperation, the result of the selection is not yet the final design of the project. It should be created in the coming months in cooperation with the BIG studio, ESET and also with the involvement of a local architectural studio, the selection of which is currently being prepared.

Based on the cooperation of ESET with the Faculty of Architecture and Design of the Slovak Technical University (FAD STU) in Bratislava, the architects from the BIG studio also became the guarantors of the newly opened 25th vertical studio at FAD STU. In the next school year, under their leadership, students will solve assignments related to the topic of innovation centers, science parks, and sustainability, but also design solutions in the post-COVID-19 era.

ABOUT THE ESET CAMPUS PROJECT
ESET acquired the plot of land at the Bratislava Patrónka site in 2017. It plans to create an ESET Campus on the site of the former Military Hospital — a living place that will turn this part of the city into an epicenter of innovation and creativity in Bratislava. In addition to the new headquarters and global research center of ESET, the campus will create a unique and stimulating environment for IT and technology companies and startups, and connect them with technically oriented universities.

In addition to a high-quality environment for innovation and research, the campus will provide a wide range of other useful services and facilities, unique public spaces and, in part, a residential function intended mainly for company employees. The campus is also envisioned to create modern forms of accommodation for students, which can deepen the integration of universities within this innovative ecosystem. An important part of the campus will be its sports infrastructure and auditorium; many of these spaces will also be available to the general public.

The campus will be built on the principles of functionality, sustainability and ecology. It is intended to support the use of public transport and maximum comfort for pedestrians as much as possible. In addition to public transport stops, there is also a railway station in the immediate vicinity of the complex, thanks to which train transport in this part of the city could become a full-fledged part of public transport.

BIG – BJARKE INGELS GROUP
BIG is a Copenhagen, New York, London and Barcelona based group of architects, designers, urbanists, landscape professionals, interior and product designers, researchers and inventors. The office is currently involved in a large number of projects throughout Europe, North America, Asia and the Middle East. BIG’s architecture emerges out of a careful analysis of how contemporary life constantly evolves and changes, not least due to the influence from multicultural exchange, global economic flows and communication technologies that all together require new ways of architectural and urban organization. More info: big.dk.

Google headquarters, USA. With Google and parent company Alphabet’s ever-expanding and ever-evolving ventures, occupying existing buildings for the expanding workforce has reached its organizational limitations – teams become spread across multiple buildings, separated by parking lots. On the other hand, a single centralized headquarters is also not the approach for Google, nor is it desirable for the city of Mountain View. Our mission is to create a replicable and scalable building typology that is also adaptable and inclusive to the various sites of North Bayshore and beyond. More info: big.dk/press/gce/

Toyota Woven City. Together with Toyota Motor Corporation, BIG unveils Toyota Woven City as the world’s first urban incubator dedicated to the advancement of all aspects of mobility at the foothills of Mt. Fuji in Japan. Envisioned as a living laboratory to test and advance mobility, autonomy, connectivity, hydrogen-powered infrastructure and industry collaboration, More info: big.dk/press/twc

Google London headquarter, UK.  Centrally located in King’s Cross and adjacent to the city’s largest station, Google’s London headquarters will be its first wholly owned and designed building outside the United States. The new 11-storey building, combined with Google’s current building at 6 Pancras Square and an additional third building, will create a King’s Cross Campus with the potential to house 7,000 Google employees. Comprising of more than 1 million sqft, of which Google will occupy 650,000 sqft, the purpose-built building is being developed from the ground up and will contribute to the Knowledge Quarter and King’s Cross’s growing knowledge-based economy. More info: big.dk/press/kgx

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

ESET啟動移動安全6.0版

BRATISLAVA – ESET, a global leader in cybersecurity, has launched version 6.0 of ESET Mobile Security (EMS), an award-winning solution that provides protection against a multitude of Android mobile security threats such as malware and phishing, and now has the added feature of Payment Protection for financial transactions.

ESET Mobile Security protects users’ data against loss, leakage and misuse through strong malware protection, as well as providing a safe browsing environment with its anti-phishing feature. EMS also protects users from physical loss and theft, connecting to my.eset.com to provide as much real-time information as possible about the status and whereabouts of the device.

Version 6.0 of the premium Mobile Security solution introduces a new layer of security for EMS users. The Payment Protection feature safeguards users from applications that utilize sensitive financial information such as banking transactions and online shopping. This feature automatically categorizes all installed applications from the Google Play Store that fall into the Finance category and scans them for potential threats. The user is also able to add other installed apps to the list that may fall outside of the Finance category.

A “safe launcher” icon is added to the user’s list of applications, and from there, apps pertaining to sensitive financial data can be launched and will be protected from malware or fake apps that may be attempting to steal credentials by replicating login screens. If an app is not launched from the safe launcher module, Mobile Security will continue to run a basic scan for unresolved antivirus issues, open network usage and the root state of the device.

To further cement ESET’s commitment to cutting-edge Android mobile protection, the company has been awarded the MRG Effitas Certificate in the Android 360° Assessment Programme Q1 2020 by MRG Effitas, a world leader in independent IT security efficacy testing, research and expertise. As the report highlights, Android devices are used by approximately 2.3 billion people around the globe, and with Android-based malware on a constant rise, it is vital that antivirus solutions protect against 100% of threats.

Version 6.0 has also undergone design changes to improve intuitiveness and ease-of-use features, such as the Call Filter feature that allows users to protect against unwanted incoming calls and a redesign of the Anti-Theft feature to allow for simpler onboarding and the resetting of passwords.

Branislav Orlík, product manager at ESET, states: “Mobile devices are a central part of our everyday lives and go far beyond just the need to call or message our friends and family. Our mobile devices are now a direct pathway to our wallets, our memories and our jobs, and it is vital that personal data is safely secured, especially sensitive financial data. With this latest version of ESET Mobile Security, we want to ensure our users feel completely secure when performing financial transactions on their devices, in addition to being protected from malware and phishing attempts. At ESET, we are dedicated to the safety of technology users across the globe and are proud to be recognized for our innovative and reliable security solutions.”

For further information on ESET Mobile Security, click here.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

Mozilla修復了會導致Android裝置被同一Wi-Fi網路駭客劫持的Firefox漏洞

這項漏洞是由澳洲研究人員Chris Moberly發現,它存在於Android版Firefox上的簡單服務發現協定(SSDP,Simple Service Discovery Protocol)中。SSDP為構成通用隨插即用(UPnP)技術的UDP協定;一臺裝置發送SSDP廣播訊息尋找到同一區域網路上的其他裝置,以分享內容。Android版Firefox即是透過發送SSDP訊息,尋找其他裝置,像是Roku,以實現第二螢幕(second-screen)的使用情境,例如播放影音或網頁內容,其影響了Firefox 79以前的Android版本 (68.11.0及更低的版本)。

在Firefox發送廣播訊息時,同一區域網路上的裝置會加以回應,並回傳一個UPnP裝置所在位置的訊息。Firefox就會試圖存取這位置,並下載符合UPnP規格的XML檔案。但研究人員發現,攻擊者可以設立一臺惡意SSDP伺服器,然後以包含指向Android intent URI的惡意訊息取代位置訊息,驅動Firefox瀏覽器執行這個意圖(intent)。例如迫使Android手機上的Firefox連向惡意網址,而全部都不需受害者的任何動作。

研究人員說,這個漏洞並非很新奇的記憶體毁損漏洞,只是簡單的邏輯bug,但是卻可以從遠端驅動,且這項漏洞像RCE (remote command execution)漏洞一樣,允許駭客在不經用戶互動下執行未授權的功能,唯獨它只能執行預先定義的應用意圖(intents)而非任意程式碼。但是光是如此,它就能可能造成網釣攻擊,或是攻擊別的App上已知有問題意圖。研究人員還示範了如何劫持同一網路下Android手機連上惡意網址、開啟郵件應用程式、或撥打電話,只要手機上安裝Firefox。

ESET資安專家建議用戶升級到79以後的版本,而桌機版則不受此影響。

原文出處:https://www.welivesecurity.com/2020/09/21/mozilla-fixes-flaw-let-attackers-hijack-firefox-android-wifi/

#若有任何資安需求,歡迎洽詢台灣二版資安專業團隊,服務電話:(02)7722-6899,或上官網查詢:https://version-2.com.tw/

關於ESET
ESET成立於1992年,是一家面向企業與個人用戶的全球性的電腦安全軟體提供商,其 獲獎產品——NOD32防病毒軟體系統,能夠針對各種已知或未知病毒、間諜軟體 (spyware)、rootkits和其他惡意軟體為電腦系統提供實時保護。ESET NOD32佔用 系統資源最少,偵測速度最快,可以提供最有效的保護,並且比其他任何防病毒產品獲 得了更多的Virus Bulletin 100%獎項。ESET連續五年被評為“德勤高科技快速成長500 強”(Deloitte’s Technology Fast 500)公司,擁有廣泛的合作夥伴網絡,包括佳 能、戴爾、微軟等國際知名公司,在布拉迪斯拉發(斯洛伐克)、布里斯托爾(英國 )、布宜諾斯艾利斯(阿根廷)、布拉格(捷克)、聖地亞哥(美國)等地均設有辦事 處,代理機構覆蓋全球超過100個國家。

關於 Version 2 Digital
資安解決方案 專業代理商與領導者
台灣二版 ( Version 2 ) 是亞洲其中一間最有活力的 IT 公司,多年來深耕資訊科技領域,致力於提供與時俱進的資安解決方案 ( 如EDR、NDR、漏洞管理 ),工具型產品 ( 如遠端控制、網頁過濾 ) 及資安威脅偵測應 變服務服務 ( MDR ) 等,透過龐大銷售點、經銷商及合作伙伴,提供廣被市場讚賞的產品及客製化、在地化的專業服務。

台灣二版 ( Version 2 ) 的銷售範圍包括台灣、香港、中國內地、新加坡、澳門等地區,客戶涵 蓋各產業,包括全球 1000 大跨國企業、上市公司、公用機構、政府部門、無數成功的中小企業及來自亞 洲各城市的消費市場客戶。

ESET Research發現CDRThief惡意軟件攻擊中國VoIP平台

BRATISLAVA – ESET researchers have discovered and analyzed malware that targets Voice over IP (VoIP) softswitches. This new malware, named CDRThief by ESET, is designed to target a very specific VoIP platform used by two China-made softswitches (software switches): Linknat VOS2009 and VOS3000. A softswitch is a core element of a VoIP network that provides call control, billing, and management. These softswitches are software-based solutions that run on standard Linux servers. Entirely new Linux malware is rarely seen, thus making CDRThief worthy of interest. The primary goal of the malware is to exfiltrate various private data, including call detail records (CDR), from a compromised softswitch.

“It’s hard to know the ultimate goal of attackers who use this malware. However, since it exfiltrates sensitive information, including call metadata, it seems reasonable to assume that the malware is used for cyberespionage. Another possible goal for attackers using this malware is VoIP fraud. Since the attackers obtain information about the activity of VoIP softswitches and their gateways, this information could be used to perform International Revenue Share Fraud,” says ESET researcher Anton Cherepanov, who discovered CDRThief. “CDRs contain metadata about VoIP calls such as caller and IP addresses of call recipients, starting time of the call, call duration, call fees, and other information,” he adds.

To steal this metadata, the malware queries internal MySQL databases used by the softswitch. Thus, attackers demonstrate a solid understanding of the internal architecture of the targeted platform.

“We noticed this malware in one of our sample sharing feeds, and as an entirely new Linux malware, it’s a rarity and caught our attention. What was even more interesting was that it quickly became apparent that this malware targeted a specific Linux VoIP platform,” explains Cherepanov.

To hide malicious functionality from basic static analysis, the authors encrypted any suspicious-looking strings. Interestingly, the password from the configuration file is stored encrypted. Despite this, Linux/CDRThief malware is still able to read and decrypt it. Thus, the attackers demonstrate deep knowledge of the targeted platform, since the algorithm and encryption keys used are not documented. Furthermore, only the malware authors or operators can decrypt any exfiltrated data.

“The malware can be deployed to any location on the disk under any file name. It’s unknown what type of persistence is used for starting the malware. However, it should be noted that once the malware is started, it attempts to launch a legitimate file present on the Linknat platform. This suggests that the malicious binary might somehow be inserted into a regular boot chain of the platform in order to achieve persistence and possibly masquerade as a component of the Linknat softswitch software,” concludes Cherepanov.

For more technical details about CDRThief, read the blog post “Who is calling? CDRThief targets Linux VoIP softswitches” on WeLiveSecurity. Make sure to follow ESET Research on Twitter for the latest news from ESET Research.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

網絡研討會:信用合作社如何確保安全的遠程網絡訪問

As the NCUA audits continue to expand, many credit unions struggle with finding an effective solution to meet Domain 3 controls within the ACET framework.

In this webinar, co-hosted by Portnox and Btech, find out how Portnox CLEAR is providing the remote network access control, off-campus endpoint awareness, risk and real-time remediation capabilities that either directly meet or highly contribute to many of the most difficult Domain 3 audit areas and requirements.

As part of this webinar, you will also hear from Utah-based University Federal Credit Union – a Portnox customer utilizing Portnox CLEAR’s zero-trust remote access-as-a-service capabilities.

The webinar will take place on Wednesday, October 14 at 3PM EST.

Michael Marvin

Director of Marketing

Mike leads global cross-channel marketing efforts at Portnox. Over the last ten years, Mike has led marketing and communications teams across a variety of areas in B2B tech, including AdTech and FinTech. He holds a B.A. in English and American Studies from Hobart College.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

馬丁·哈勒專訪GREYCORTEX

In the header of your blog there’s written “In the head of a Network Administrator: Thoughts, ideas, insights” – that brings up a question: what have you been dealing with in terms of security at your clients in the past few months?

That’s a pretty good question. I’ve been thinking about changing the header recently into something in the sense of “IT security lies in thorough and honest work”, which corresponds the most with what we come across during audits in companies.
IT departments often try to do “rocket science”. They consider advanced and expensive technologies, such as sandboxing and SIEM, skipping basic and simple concepts. For instance, they update servers twice a year, they use just a few passwords (as they haven’t adopted a password manager), they administer everything under the domain admin account and they haven’t performed a test disaster recovery from backup yet.
Don’t get me wrong. Sandboxing and SIEM are really useful technologies. It’s just that they belong to “add-on” technologies, and it’s necessary to get the network tidy first – get to know it inside out, be aware of all devices, setup the firewall and antivirus correctly. Basically, it’s important to focus first on activities that will contribute to security the most with the least effort.

You mention sophisticated attacks and chaotic arrangement of the infrastructure – what kind of impact might they have on organizations and companies? And what risks do you as an expert link with them?

When investigating attacks, I’m often taken aback by how fast the attackers manage to perform a “lateral movement”. It’s the stage of attacks in which attackers have a device under control, and they attempt to extend it to as much of the network as possible. In many cases they manage within a few hours. For example, in one case they managed to get a backdoor to a Director’s PA’s computer using spear-phishing. On Friday night they connected to it and within three hours they took over the domain administrator account and took control of the whole network. That’s a very short time and it’s really difficult for a company without 24/7 network security monitoring to react in time.
It’s critical to invest more time in securing the internal network to make “lateral movement” harder for the attackers and get time to detect and stop them.
Most administrators I meet put all their effort into protecting the “perimeter”. They see the security black and white – the Internet’s full of the bad, while the internal network seems safe to them. That’s a pity as the perimeter’s usually very well secured and the extra time invested has little effect. On the other hand, the internal network tends to be neglected security-wise, so every single day spent securing it is noticeable.

I understand there’s not a single correct approach that would protect all users. In your opinion, though, is there a “must” for the companies to protect their data nowadays? Something that’s changed in this respect in the past 10 years, e.g. new technologies or tools?

The thing is that security will probably never be 100 %. There will always be some zero-day vulnerabilities, human errors, and it won’t be possible to apply all security technologies (e.g. they won’t be compatible with business requirements). That’s why every company should have an efficient back-up system, resistant to hacker attacks. Thanks to that they’ll be able to get their data back without having to pay a ransom.
The development of the cloud and fast Internet has helped a lot in this area. It’s possible to make off-site backups in the cloud for a reasonable price, where the backups are protected against deleting (thanks to snapshotting, i.e. preserving a state of the storage where backups are located to a particular point in time) and natural disasters.
That doesn’t mean, though, that it isn’t necessary to deal with security anymore. A successful attack still means a downtime for days or weeks for companies as well as the risk of making their private data public.

So, it’s not just about eliminating the causes, but prevention – it’s clear that as an expert on IT security you often face misunderstanding from budget holders. What arguments or real-life cases do you use at such moments?

Exactly, the prevention is paramount. It’s cheaper to prevent problems than to deal with their consequences. Thanks to the media attention paid to the recent cyber attacks (on hospitals) the budget holders now realize the need to deal with security. The money is there. The issue is its effective allocation. Almost every IT company now “does” security. There’re also a lot of vendors of security SW / HW solutions. Security’s not a commodity, though, and the quality of individual solutions differs diametrically. The price isn’t a reliable indicator, either. Our strategy is to educate the public in the area of security. And we want Czech companies and institutions to have good security.

So far, the year 2020 seems to be a year full of changes and the need to be prepared even for the most unbelievable moments, which applies to cyberattacks, too. After all, some may be considered more likely a target than others. For example, in the USA there’ll be the presidential election, the Olympics in Tokyo (postponed to 2021), the world economics has shaken due to the coronavirus, and a lot of companies “go online”, which poses enormous risk in itself. Are there any other events or circumstances this year that, in your opinion, may carry a higher risk of attack?

Talking about the Olympics, I’ve read an article about a cyberattack on the 2018 Winter Olympics in PyeongChang, South Korea. It was a very interesting and sophisticated attack which didn’t turn into a fiasco only thanks to a coincidence and a bit of luck. I definitely recommend reading “The Untold Story of the 2018 Olympics Cyberattack, the Most Deceptive Hack in History”.
It’s hard to say whether companies “going online” will have any influence on cybercrime. Most companies were already ready for home office and remote work. On the other hand, there are still a lot of companies on the market that are only about to modernize and digitize their processes. Due to the lack of IT people on the market, it’s possible that some implementations of changes won’t be done very thoroughly.

Given the direction hacker attacks have taken recently – where do you see the future of security tools?

Good question. Apart from imposing restrictions, it’s also crucial to have an overview of your network. That’s the only way how to recognize that the “restrictions” have been overcome and there’s an intruder in the network. Systems such as IDS / IPS will help you with that, as well as honeypots, network traffic analyzers, or SIEM systems. The choice of the system depends on the needs and possibilities of each company, though.
Apart from an early warning about a network issue, the systems are also necessary for backward incident investigation. With their help, it’s possible to find out how far the attackers got, which accounts and devices were compromised, which techniques and programs they used during the attack, which data they took out, how long the network was compromised, or the intrusion vector (the route of the attack). Without such systems the investigation of attacks is strenuous and inaccurate. Especially nowadays, when ransomware groups not only encrypt the data, but also steal parts of it and subsequently publish it (unless paid), such systems are needed more than ever before. Without them it’s almost impossible to find out whether any of your data got stolen during the attack, or not. 
Due to the decreasing price of network analyzers, their constant debugging, and the increasing importance of IT, I expect their adoption to grow. These technologies have a very good price / performance ratio. 

Martin Haller

Martin Haller is a co-owner of PATRON-IT and a technician with all his heart. He specializes in cyber security and has experience as an ethical hacker. He believes it’s necessary to be able to break the network first in order to secure it well. On his blog martinhaller.cz he shares updates from the field of IT security as well as his own real-life insights. He also runs his own YouTube channel – you’ll find there e.g. what a webcam attack looks like.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About GREYCORTEX
GREYCORTEX uses advanced artificial intelligence, machine learning, and data mining methods to help organizations make their IT operations secure and reliable.

MENDEL, GREYCORTEX’s network traffic analysis solution, helps corporations, governments, and the critical infrastructure sector protect their futures by detecting cyber threats to sensitive data, networks, trade secrets, and reputations, which other network security products miss.

MENDEL is based on 10 years of extensive academic research and is designed using the same technology which was successful in four US-based NIST Challenges.