Skip to content

ESET在SE Labs的Enterprise Endpoint Protection測試中獲得最高獎項

BRATISLAVA – ESET, a global leader in cybersecurity, has earned the highest possible award in SE Labs’ Q1 2021 Enterprise Endpoint Protection test, the AAA award, for ESET Endpoint Security. ESET has claimed the AAA award for the third time, following recognition from SE Labs in both Q1 and Q3 of 2020.

A leading independent testing company, SE Labs aims to improve information technology security by assessing products and services designed to detect attacks and protect against intrusions. SE Labs tested 9 endpoint security solutions between January and March 2021 to evaluate product efficacy at detecting and protecting against threats in real time. ESET Endpoint Security received a total accuracy rating of 1,116, along with the second highest total accuracy percentage of 99%.

ESET Endpoint Security is designed to protect endpoints using multiple layers of protection, including Advanced Machine Learning, Host-based Intrusion Prevention System (HIPS), Exploit Blocker, Advanced Memory Scanner, and UEFI Scanner. In testing, the solution was exposed to a mixture of targeted attacks and public web-based threats. The results demonstrate that ESET Endpoint Security is consistently effective at blocking malicious URLs, handling exploits, and correctly classifying legitimate applications and websites.

Jiri Kropáč, Head of Threat Detection Labs at ESET, commented: “We are thrilled to be recognized by SE Labs with an AAA award for the third time. The award reflects our commitment to providing enterprise customers with the absolute best in cybersecurity solutions and highlights our consistent efforts to provide robust and reliable products as the threat landscape evolves in complexity. Testing our solutions in real-world environments is crucial in confirming to users that their businesses, data, and employees are in the best possible hands when it comes to malicious actors and cyberattacks. With cybersecurity as a top priority for businesses across the globe, ESET is proud to provide organizations with cutting-edge technology of the highest quality.”

You can find out more about ESET Endpoint Security here.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

調查發現英國數以百萬計的網際網路使用者正在使用老舊且不安全的路由器

消費者權益組織在去年(2020)12月調查,根據這些資料,發現如Virgin、EE、Sky、TalkTalk和Vodafone等路由器存在缺陷,大部分機型估計約有六百萬人的設備自2018年或更早的時候就沒有更新過韌體,這可能會使裝置暴露在風險之下;另一個則是較弱的預設密碼很容易被猜出來,這使得遠端攻擊者有可能控制裝置;還發現了本地網路漏洞,儘管這些漏洞需要攻擊者在Wi-Fi範圍內才能利用。

路由器安全性一直是一個長期存在的問題,並且自從*****COVID-19大流行迫使大多數人遠距(居家)辦公,更成為一個特別重要的資安議題*****。不受保護的路由器也將成為攻擊者的目標,藉以控制智慧家居裝置,竊聽通訊和網頁瀏覽等。

為了增加路由器的安全,ESET資安專家建議如下,
1.更改路由器的密碼(字母加數字的高強度密碼)
2.路由器預設的管理IP修改為自己指定的特殊IP;開啟路由器MAC位址過濾功能,只允許已知設備連入
3.關閉設備本身的WPS PIN碼與UPnP機制
4.常登錄路由器管理後台,看看有沒有不認識的設備連入了WIFI,如果有,及時將其清除
5.注意韌體更新,減少設備漏洞威脅
6.安裝知名防毒軟體(非常重要!!!), ESET Internet Security網路安全套裝配備【掃描路由器】功能,可協助在連線至外部網路時,識別駭客攻擊路由器並提高防護等級。

原文出處:https://www.welivesecurity.com/2021/05/07/popular-routers-vulnerable-hacker-attacks/

#安全居家辦公,請購買ESET網路安全套裝:https://www.eset.tw/estore/zh/

關於 Version 2 Digital

資安解決方案 專業代理商與領導者 台灣二版 ( Version 2 ) 是亞洲其中一間最有活力的 IT 公司,多年來深耕資訊科技領域,致力於提供與時俱進的資安解決方案 ( 如EDR、NDR、漏洞管理 ),工具型產品 ( 如遠端控制、網頁過濾 ) 及資安威脅偵測應 變服務服務 ( MDR ) 等,透過龐大銷售點、經銷商及合作伙伴,提供廣被市場讚賞的產品及客製化、在地化的專業服務。

台灣二版 ( Version 2 ) 的銷售範圍包括台灣、香港、中國內地、新加坡、澳門等地區,客戶涵 蓋各產業,包括全球 1000 大跨國企業、上市公司、公用機構、政府部門、無數成功的中小企業及來自亞 洲各城市的消費市場客戶。

關於ESET
ESET成立於1992年,是一家面向企業與個人用戶的全球性的電腦安全軟體提供商,其 獲獎產品——NOD32防病毒軟體系統,能夠針對各種已知或未知病毒、間諜軟體 (spyware)、rootkits和其他惡意軟體為電腦系統提供實時保護。ESET NOD32佔用 系統資源最少,偵測速度最快,可以提供最有效的保護,並且比其他任何防病毒產品獲 得了更多的Virus Bulletin 100%獎項。ESET連續五年被評為“德勤高科技快速成長500 強”(Deloitte’s Technology Fast 500)公司,擁有廣泛的合作夥伴網絡,包括佳 能、戴爾、微軟等國際知名公司,在布拉迪斯拉發(斯洛伐克)、布里斯托爾(英國 )、布宜諾斯艾利斯(阿根廷)、布拉格(捷克)、聖地亞哥(美國)等地均設有辦事 處,代理機構覆蓋全球超過100個國家。

安居樂業只有一種方式:安全的密碼管理

A few rules for safe password management

In this, our competent blog, we boast of always giving you good advice and providing you with the technological information necessary for your life as a technologist to make sense. Today it is the case again, we will not reveal the hidden secret about the omnipotence of Control/Alt/Delete, but almost. Today in Pandora FMS blog, we give you a few tips for safe password management.

Safe password management

The purpose of this article is for users to be responsible for keeping their coveted passwords or authentication information safe when accessing confidential information. Because think about it, dear reader, how long ago did you come up with your first password? Surely it was to enter your select club in the treehouse. Maybe you even still choose the same for your social networks, Netflix or office pc. Was it as ordinary as your birth date? Your name and the first two acronyms of your surname? “RockyIV”, which was the name of your fourth favorite pet and movie? I don’t blame you, we have all been equally original and carefree when choosing a password.

But that is over! Many things already depend on this password, on this motto or pass that must include more than eight characters and at least one capital letter and one number. Your company security is not a game, damn it! There is a lot of mischief and felon out there that can put you and your businesses in a loophole, because of a vulnerability such as having a poor password! But do not worry, we will help you, we will talk about safe password management. We are Pandora FMS blog, we like potato salad, Kubrick movies and fighting against injustices!

Recommendations for safe password management

*Obvious but vital fact: User IDs and passwords are used to check the identity of a user on systems and devices. I just point that out here as an outline in case someone is so lost that they don’t know this. I repeat that we are talking about strong password management, so knowing what a password is is a must and saves time.

Said passwords are necessary for users to have access to information, normally, even if the merit is not recognized: capital information in your company. User IDs and passwords also help ensure that users are held accountable for their activities on the systems they have access to. Because yes, telereader friend, users are responsible for any activity associated with their user IDs and passwords. For that reason, it is very important for you to protect the password with your life and comply with the following policies related to them:

  1. Users may not, under any circumstances, give their password or a password indication to a third party. *This seems obvious, but trust me, it is not. People sneak passwords like they’re office whispers or reggaeton choruses.
  2.  Users will not use user identifiers or passwords of other users. *As we can see, in this case, sharing is not living.
  3.  Users must change initial passwords or passwords received as temporary “reset” passwords immediately upon receipt. *For me, this is the most exciting and creative part, you never want to set the abstract code they give you, you want to improvise, imagine, CREATE!
  4.  Users should change their passwords if they suspect that their confidentiality may have been compromised, and immediately report the situation as a security incident. *Don’t be ashamed of yourself, admit that someone may have violated your secret and repent before it’s too late.
  5.  Users should not use the “remember password” function of programs. For example, if an application sends users the message of “automatically remember or store” the user’s password for future use, they will have to reject it. *This is a piece of information you did not know, huh? Well, it is as interesting as it is important.
  6.  Users should not store passwords without encryption, for example, in a text file or an office document. In this case, this document must be protected with access control.
  7.  When an administration password must be communicated, never send by the same means, the user and the password. For example, the user should be sent by email and the password by instant messaging. *I know that sometimes you try to save time, but with these things you better take your time and do not risk it.
  8.  Users should not set the password on a post-it on the monitor, nor on the table, nor in the drawer or “hidden” in another place in the office or among your personal belongings. *This is one of the big mistakes everyone makes. Yes, post-its or notebook sheets have always helped us, but this time they are too obvious to keep such a big secret.
  9.  Users should not use the same password for two systems or different applications. *Sorry, but you will have to memorize more than one. But rest assured, if a chimpanzee could recognize the descending sequence of nine numbers, someone who graduated from elementary school can do better.
  10.  Users who find out the password of other users must report it, ensuring it is changed as soon as possible. *Here fellowship first and foremost. It is not only right hugging after company dinners. Camaraderie above all!
  11.  Users must change their passwords at least once a year, or when indicated by the system, and in the case of administration passwords every 180 days, or in the event of changes of personnel in the company that may know them.
  12.  If now you are afraid because you do not have a strong enough password, it’s normal, but I repeat, calm down, follow the following rules for passwords creation (if the system supports them) and nothing will go wrong:
  •  a) Passwords must be at least six characters long.
  •  b) Passwords must not be easily predictable and must not be contained in dictionaries. For example: your username, date of birth, or 1234, we all know that one.
  •  c) Passwords must not contain consecutive repeating characters. For example: “AABBCC”.
  •  d) Passwords must have at least an alphanumeric character, a numeric character, and a special character.

Good, and so far that was the lecture about being responsible that you must assume and internalize if you want things to go smooth at least in terms of passwords and vulnerabilities. Oh, nothing to thank us for! You know: “Life is beautiful. Password yourself”. Look, that could be your new password, right? No, the answer is NO! REMEMBER EVERYTHING WE LEARNED TODAY IN THIS ARTICLE!

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About PandoraFMS
Pandora FMS is a flexible monitoring system, capable of monitoring devices, infrastructures, applications, services and business processes.
Of course, one of the things that Pandora FMS can control is the hard disks of your computers.

Portnox在2021年RSA大會上被提名為令人垂涎的全球InfoSec獎的獲勝者

Portnox Wins Award for “Cutting Edge NAC” in 9th Annual Global InfoSec Awards at RSAC 2021


NEW YORK–Portnox is proud to announce it has won the award for “Cutting Edge Network Access Control (NAC)” from Cyber Defense Magazine, the world’s leading information security e-magazine. “We’re thrilled to receive one of the most prestigious and coveted cybersecurity awards in the world from Cyber Defense Magazine. We knew the competition would be tough – after all, the judges are leading infosec experts from around the globe. We couldn’t be more pleased,” said Ofer Amitai, CEO at Portnox.

Portnox’s cloud-delivered NAC-as-a-Service – Portnox CLEAR – has taken the network access control (NAC) market by storm in recent years, seeing a surge of new customers seeking to move off of their legacy on-premise NAC solutions. In 2020, Portnox saw its revenue grow 30% year-over-year.

“As the only true SaaS NAC product on the market, Portnox CLEAR is making NAC implementation and deployment easier for enterprises – particularly those with highly distributed networks,” said Tomer Shemer-Buchbut, Vice President of Products at Portnox. “By eliminating on-going maintenance like upgrades and patches common of on-premise NAC, we’re offering companies far better total cost of ownership.”

“Portnox embodies three major features we judges look for to become winners: understanding tomorrow’s threats, today, providing a cost-effective solution and innovating in unexpected ways that can help stop the next breach,” said Gary S. Miliefsky, Publisher of Cyber Defense Magazine.

With 80 billion connected devices expected to be in use by 2025, the NAC market is growing rapidly – projected to reach nearly $12 billion globally. Device proliferation paired with an ever-expanding number of cyber threats and hybrid workforce operations has made network access control a critical component of any enterprise cybersecurity stack. “NAC is front and center for CISOs and their IT security teams. Expect the demand for network access control – particularly cloud NAC – to continue to grow as companies continue to embrace emerging networking models like SD-WAN, ZTNA and SASE,” said Amitai.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

About CDM InfoSec Awards
This is Cyber Defense Magazine’s ninth year of honoring global InfoSec innovators. Our submission requirements are for any startup, early stage, later stage or public companies in the INFORMATION SECURITY (INFOSEC) space who believe they have a unique and compelling value proposition for their product or service. Learn more at http://www.cyberdefenseawards.com

About the Judging
The judges are CISSP, FMDHS, CEH, certified security professionals who voted based on their independent review of the company submitted materials on the website of each submission including but not limited to data sheets, white papers, product literature and other market variables. CDM has a flexible philosophy to find more innovative players with new and unique technologies, than the one with the most customers or money in the bank. CDM is always asking “What’s Next?” so we are looking for Next Generation InfoSec Solutions.

About Cyber Defense Magazine
With over 5 Million monthly readers and growing, and thousands of pages of searchable online infosec content, Cyber Defense Magazine is the premier source of IT Security information for B2B and B2G with our sister magazine Cyber Security Magazine for B2C. We are managed and published by and for ethical, honest, passionate information security professionals. Our mission is to share cutting-edge knowledge, real-world stories and awards on the best ideas, products and services in the information technology industry. We deliver electronic magazines every month online for free, and special editions exclusively for the RSA Conferences. CDM is a proud member of the Cyber Defense Media Group. Learn more about us at https://www.cyberdefensemagazine.com and visit https://www.cyberdefensetv.com and https://www.cyberdefenseradio.com to see and hear some of the most informative interviews of many of these winning company executives. Join a webinar at https://www.cyberdefensewebinars.com and realize that infosec knowledge is power.

監控安全架構

Introduction

Do an exercise, ask five IT technicians -of any profile- what SNMP means.. If you’re close with them the better, so that the first thing they do is not go to Wikipedia to boast. Hopefully, they might tell you what they said to me when I was working in networks.

“Security is Not My Problem”

Taking into account that the SNMP protocol is one of the monitoring bases, and a system that has been in use for more than thirty years, this answer, “Security is Not My Problem”, sums up the current monitoring situation quite well: ignorance, laziness and lack of interest in monitoring security.

By the way, we talked about SNMP in another article on our blog and I will give you a teaser in advance, it means Simple Network Management Protocol and it comes from 1987.

Considering that monitoring is “key to the kingdom”, since it allows access to all systems and even access many times with administration credentials, shouldn’t we take security a little more seriously when we talk about it?

Recent vulnerabilities in well-known monitoring systems such as Solarwinds or Centreon make the need to take security seriously in the implementation of monitoring systems increasingly urgent, since these have a very strong integration with systems.

In many cases, security problems are not so much about one piece of software being much safer than another, but about poor configuration and/or architecture. It must be taken into account that a monitoring system is complex, extensive, and in general, it is highly adapted to each organization. Today it was Solarwinds, tomorrow it could be Pandora FMS or Nagios.

No application is 100% secure, nor is any corporate network secured against intrusion, whatever the type. This is an increasingly evident fact and the only thing that can be done about it is to know the risks and assume which ones you can take, which ones absolutely not, and work on the latter.

Safe monitoring architecture

It is essential to keep in mind at all times that a monitoring system contains key information for a possible intruder. If monitoring falls into the wrong hands, your system will be compromised. That is why it is so important to devote time to the architecture of your monitoring system, whatever it may be.

Carry out a first analysis, collecting the requirements and scope of your monitoring strategy:

  • Identify what systems you are going to monitor and catalogue their security levels.
  • Identify which profiles will have access to the monitoring system.
  • Identify how you will obtain information from those systems, whether through probes/agents or remote data.
  • Identify who is responsible for the systems you are going to monitor.

The architecture of a system will have, whatever the chosen software, the following elements and will have to take into account its network topology, its resources and the way to protect them properly:

  1. Information display interface (web console, heavy application).
  2. Data storage (usually a relational database).
  3. Information collectors (intermediate servers, pollers, collectors, etc.).
  4. Agents (optional).
  5. Notification system (alerts, notices, etc.).

Monitoring system securing

No matter how correct the implementation of a system, its architecture and its design as a whole is, if one of the elements that make it up is violated, the damage it may suffer by a malicious attack compromises the entire structure. For this reason, in security there is a saying, “Security is a chain and your real security always depends on its weakest point.”

This list of security concepts applied to the architecture of a monitoring system can be summarized as the features that a monitoring product must have to ensure maximum security in an implementation:

  • Encrypted traffic between all its components.
  • High availability of all its components.
  • Integrated backup.
  • Double access authentication.
  • Delegated authentication system (LDAP, AD, SAML, Kerberos, etc.).
  • ACL and user profiling.
  • Internal audit.
  • Password policy.
  • Sensitive data encryption.
  • Credential containers.
  • Monitoring of restricted areas/indirect access.
  • Installation without superuser.
  • Safe agent/server architecture (passive).
  • Centralized and distributed update system.
  • 24/7 support.
  • Clear vulnerability management policy by the manufacturer.

Monitoring infrastructure basic securing

The management console, monitoring servers and other elements should never be on an accessible public network. The console should always be protected on an internal network, protected by firewalls and, if possible, on a network independent from other management systems.

The operating systems that host the monitoring infrastructure should not be used for other purposes: for example, to reuse the database for other applications, nor the base operating systems to run other applications.

Safe and encrypted traffic

You should make sure that your system supports SSL/TLS encryption and certificates at both ends at all levels: user operation, communication between components or sending data from the agent to the servers.

If you are going to use agents in unsafe locations, it is highly recommended that you force all external agents to use certificate-based authentication at both ends, to avoid receiving information from unauthorized sources and to prevent information collected by agents to not travel transparently.

On the other hand, it is very important for you to activate encryption on your web server to provide an encrypted administration console and prevent any attacker from seeing access credentials, remote system passwords or confidential information.

Full High Availability

For all elements: database, servers, agents and console.

Integrated backup

The tool itself should make this as easy as possible, as settings and data are often highly distributed and consistent backup is complex.

Clear vulnerability management policy by the manufacturer

Every day, dozens of independent auditors test the strengths and weaknesses of all kinds of business applications. They seek to gain a foothold in the sector by publishing an unknown ruling to increase their reputation. Many clients, as part of their internal security management processes, execute external and internal security audits that target their IT infrastructure.

Be that as it may, all products have security flaws, the question is: how are those flaws handled? Transparency, diligence and communication are essential to prevent customers from having problems derived from vulnerabilities in the software they use. It is essential that there is a clear policy in this regard, so that it is known which public vulnerabilities have been reported, when they have been corrected and if a new one is detected, the steps to follow for notification, mitigation and distribution to the end customer.

Dual authentication system

Pandora FMS has an -optional- system based on google authenticator that allows forcing its use for all users for security policies. This will make user access to the administration console much safer, preventing that due to privilege escalation the system can be accessed as administrator, which is, at best, the highest risk that can be run.

Delegated authentication system

Complementary to the previous one, you can delegate management console authentication to authenticate against LDAP, Active Directory, or SAML. It will enable a centralized access management, and combined with the double authentication system your access will become much safer.

ACL and user profiling

Identify and assign different users to specific people. Do not use generic users, assign only the necessary permissions and do not use “super administrators”. They are good practices not only for monitoring tools but for any business software implementation with access to sensitive information.

Nowadays, any professional tool to define an access profile for each user will do so in such a way that no user has “absolute control”, but only has the minimum required access to their functions.

Internal audit system

You must have a system in place to record all user actions, including information on altered or deleted fields. Said system must be able to be exported abroad so that not even the administrator user can alter said records.

Password policy

A basic element that allows you to enforce a strict password management policy for access to application users: minimum password size, password type, their reuse, forced change once in a while, etc.

Sensitive data encryption

The system must allow the most sensitive data to be stored encrypted and safely, such as access credentials, monitoring element custom fields, etc. Even if the system itself contains the encryption “seed”, it will always be much more difficult for a potential attacker to access this information.

Credential containers

Or an equivalent system for the administrator to delegate credential use to other users who use said credentials to monitor elements without seeing the passwords contained in the container.

Restricted area monitoring

In these systems, information will be collected remotely by a satellite server and will be available to be collected from the central system (in Pandora FMS through a specific component called Sync server). That way, data can be collected from a network without access to the outside, ideal for very restrictive environments where the impact is drastically reduced if an attacker takes over the system.

Agent remote management locking system

For critical security environments, where the agent cannot be remotely managed once it is configured. This is especially critical in monitoring, since if a system is compromised and its administration is accessed, by the way the system is configured itself, it will have access to all systems from where it receives information. In critical systems, the remote management capacity must be deactivated, even if that makes administration more tricky. The same applies to automatic updates on the agent.

Design of safe architecture for communication with agents

Sometimes known as passive communication. That way, agents will not listen to a port nor have remote access from the console. They are the ones who will connect to the central system to ask for instructions.

Installation without root

Pandora FMS can be installed in environments with custom paths without running with root. In some banking environments, it is a requirement that we meet.

Notification and reporting system (alerts, notices, etc.)

A monitoring system is only useful if it shows accurate information when it is needed. Alert or weekly report reception is the culmination of all the previous work and for that you will have to take into account some “obvious” points that are often overlooked. Protect those systems, wherever they may be.

Periodic updates

All manufacturers now distribute regular updates, which include both bug fixes and security problems. In our case, we publish updates approximately every five weeks. It is essential to update systems as soon as possible, because when a vulnerability is reported, product managers ask external security researchers who have reported the bug, not to publish anything about the vulnerability until a patch is published. Once the patch is published, the researcher will publish the information in more detail as wished, a fact that can be used to exploit and attack non-updated software versions.

Pandora FMS has a vulnerability disclosure public policy as well as a public catalog of known and reported vulnerabilities. Our policy has maximum transparency and full communication with security researchers, always to mitigate the impact of any security problem and to be able to protect our clients as a top priority.

24/7 support

In our support, the technician who answers the phone has the whole team backing him up. If there is a security issue and a security patch has to be published within hours. We not only have the technology to spread the patch to all our customers, but also the team to develop it in record time.

Base system securing

Hardening or system securing is a key point in the global security strategy of a company. As manufacturers, we issue a series of recommendations to carry out a safe installation of all Pandora FMS components, based on a standard RHEL7 platform or its equivalent Centos7. These same recommendations are valid for any other monitoring system:

Hardening checklist for monitoring base system:

  • System access credentials.
  • Superuser access management.
  • System access audit.
  • SSH securing.
  • Web server securing.
  • DB server securing.
  • Server minimization.
  • Local monitoring.

Access credentials

To access the system, nominative access users will be created, without privileges and with access restricted to their needs. Ideally, the authentication of each user should be integrated with a double authentication system, based on token. There are free and safe alternatives such as Google Authenticator that can be easily integrated into Linux, although outside the scope of this guide. Seriously consider its use.

If it is necessary to create other users for applications, they must be users without remote access (for this, it is necessary to deactivate their Shell or some equivalent method).

Superuser access through sudo

In the event that certain users must have administrator permissions, SUDO will be used.

Base system access audit

It is necessary to have the security log /var/log/secure active and monitor those logs with monitoring (which we will see later).

By default CentOS has this enabled. If not, just check the /etc/rsyslog.conf or /etc/syslog.conf file.

We recommend you to take the logs from the audit system and collect them with an external log management system. Pandora FMS can do it easily and it will be useful to set alerts or review them centrally in case of need.

SSH server securing

The SSH server allows you to remotely connect to your Linux systems to execute commands, so it is a critical point and must be secured by paying attention to the following points:

  • Modify default port.
  • Disable root login.
  • Disable port forwarding.
  • Disable tunneling.
  • Remove SSH keys for remote root access.
  • Investigate the source of keys for remote access. To do this, look at the content of the file /home/xxxx/.ssh/authorized_keys and see which machines they are from. Delete them if you think there shouldn’t be any.
  • Establish a standard remote access banner that clearly explains that the server is a private access server and that anyone without credentials should log out.

MySQL server securing

Listening port. If MySQL server has to provide service to the outside, just check that the root credentials are safe. If MySQL only gives service to an internal element, make sure that it only listens on localhost.

Web server securing

We will modify the configuration to hide the Apache and OS version in the server information headers.

If you use SSL, disable unsafe methods. We recommend the use of TLS 1.3 only.

System service minimizing

This technique can be very exhaustive. It consists simply of eliminating everything that is not necessary in the system. Thus we avoid possible problems in the future with poorly configured applications that we really did not need and that can be vulnerable in the future.

Local monitoring

All the internal monitoring systems would have to be monitored to the highest level, specially information registries. In our case the following active controls in addition to the standard controls are always recommended:

  • Active security Plugin.
  • Complete system inventory (specially users and installed packages).
  • System logs and server security.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About PandoraFMS
Pandora FMS is a flexible monitoring system, capable of monitoring devices, infrastructures, applications, services and business processes.
Of course, one of the things that Pandora FMS can control is the hard disks of your computers.

【重要訊息公告】ESET 全系列產品售價調整及版本更名

致 各經銷合作伙伴

承蒙各位親愛的夥伴多年來長期對台灣二版及 ESET 資安軟體的支持與愛
護。自 2021/6/14(一)起,ESET 全產品進行售價調整及版本更名,更多詳細內
容與價格請洽各專屬業務詢問。

◆ 附註:
目前已報價或已報備之客戶不受影響,唯須於6/14前下單。
以上特此公告。


台灣二版有限公司
2021 年 5 月 14 日

Pandora FMS 中的工程和開發

Pandora FMS started as a totally personal open source project back in 2004. I wasn’t even a professional programmer, I was doing Unix security consulting. In fact, I chose PHP but Pandora FMS was my first application with PHP, I knew some things about ASP and my favorite programming language had been C.

A project with a single programmer and no professional users of his software yet is very different from a project with several dozen programmers and hundreds of clients using the software in critical environments. The evolution that Pandora FMS has undergone from 2004 to 2021 is a real case of steady improvement in software engineering.

Fortunately, I did not pay much attention to that subject of the degree, because most of the things that work and that I have learned with practice do not come in a book, nor are they explained at the university, because each software project and each team of people is very different. It may sound cliché, but it is the truth, and it is better to accept it and avoid formulas, because building a solid software product that can grow over time is not trivial at all.

In this article, I am going to talk about our experience, our evolution over time, but above all, about how our engineering processes work today. I have always believed that the most important part of open source is transparency, and that this should apply to everything, not only to software but also to processes and knowledge in general.

Version control system

It is an essential part of any software project. Today the ubiquitous GIT is everywhere (by the way, not everyone knows that Git is the work of Linus Torvalds, original author of the Linux kernel). A version control system helps, in short, a group of developers work without overlapping their jobs.

When the Pandora FMS project started, I was working without version control, because there were no other people. When some people began to collaborate on it, we realized that a simple shared directory was not worth it, because we were overlapping the code and, yes, making backups to save old versions was not a very efficient method.

The first version control system we used was CVS, which we have been using for eight years or more. Around 2008, we started using SVN (Subversion) another slightly more efficient system and it wasn’t until 2013 when we started using GIT and opened our official repository on Github.

Ingeniería-y-desarrollo-en-Pandora-FMS

Pandora FMS public repository on Github

Since Pandora FMS has an open source version and an Enterprise version -with proprietary code and commercial licenses- we have two GIT projects, one public on GitHub and the other private, which we manage with GitLab. The GitHub version is in sync with our private copy on GitLab at our offices. Some partners who collaborate with us in developing have access to this private repository, and through an extension of our support application (Integria IMS) we share all development planning tickets by releases with some of our partners, so that they can see in real time, the development planning based on “releases” and all the details of each ticket.

Ingeniería-y-desarrollo-en-Pandora-FMS

GitLab ticket view in Integria IMS/em>

Ingeniería-y-desarrollo-en-Pandora-FMS

Release ticket view

Development methodology used in Pandora FMS

At Pandora FMS, we have been using our own methodology from the beginning, although we have borrowed many ideas from agile methodologies, especially from SCRUM. From a life cycle point of view, we use an adaptation of the Rolling Release methodology

These are some important definitions when defining how we work, some of them come from Scrum, others from other methodologies.

Objectives of Pandora FMS work methodology

The objectives involve not only the development members, but also QA, the documentation team and part of the marketing team:

    • Maximum visualization: The entire team must see the same information, and it must flow from bottom to top and from top to bottom. By sharing objectives we will be able to do a more effective job.
    • What is not seen does not exist, which implies that all information relevant to the project must be reflected in the management, implemented with Gitlab. What is not seen does not exist, and what does not exist will not be taken into account for any purpose. Strictly following this methodology will allow everyone to be very aware of the planning:

-Strict deadline compliance.

-Advance planning without last minute modifications.

-Clearer information and in due time.

-Elimination of work peaks and etc.

  • Integrity,, with an increasingly large and complex project, it is imperative to keep integrity during development. All code must follow standards..


Ticket

The ticket is the minimum work unit. There is a single person responsible for its completion and it is planned to be carried out in a milestone (version release).

A ticket is the way in which the development work is broken down, so a big feature will be made up by different tickets, on which ideally several people can work.

The ticket must contain a functional or description of the requirements, which can include diagrams, specifications, interface diagrams (mockup), test sets, examples, etc. In some cases it may even contain the analysis and design of the whole solution.

A completed ticket must perform as specified in the functional document (ticket) and the changes that have been made to these specifications must be reflected in the ticket.

The functional is key so that QA can validate a ticket or not. QA will have to reopen a ticket if it does not meet any of the functional aspects.

Members and working groups

Product Owner (PO)

The PO defines where Pandora FMS has to go, in contact with customers, support and
the “real” market situation, providing technical and functional guidelines but without getting involved in development as such.

Product Committee

Group of people who will meet permanently with the PO to agree where the product is going to, trying to ensure that all PO decisions are collegiate. It is made up of the leader of each Development, QA, Support, Projects and Documentation team.

Development Manager (DM)

The DM will manage the entire development cycle: define milestones, priorities, manage
individually all members and make operational decisions. The DM reports exclusively to PO and is the leader of the development team.

Development Team

They are in charge of the development of large features and product improvements, complete code refactoring, change development (small features), bug fixes and product maintenance improvements.

QA Team

They verify that each development atomic unit works as defined in the
specifications. They will also create and maintain an ecosystem of automated testing for both backend and user experience.

Support Team

They are the ones who deal directly with the client solving issues. Their experience with the product’s day-to-day means that their opinions must be taken into account, that is why they are part of the product committee.

Project team

They implement it on the end customer and are the ones closest to the customer, since they are often there before the project exists, and they usually offer ideas and all kinds of features in hand, for all purposes they are the “speaker” of the commercial department, therefore they are part of the product committee.

Training and Documentation Team

Responsible for training and the product’s documentation. They coordinate with the marketing team and the translation team.

Remote working

All team members (development, QA, documentation) telework freely. In fact, developers from Europe, Asia and America participate in Pandora FMS, and within Spain they are distributed throughout the national territory. We are a 100% distributed and decentralized company, although with traditional hierarchies.

In order to telework, we need each member to take responsibility for their work, be autonomous and commit to planning. Teleworking entails minimizing the need for oral communication and physical personal meeting, replacing them not with teleconferences, but with a precise use of the tools of the development process.

Development watch-keeping

A developer on the team is especially devoted to solving incidences involving code, in permanent connection with the support team (from 8 am to 8 pm, CEST). This allows not only to have maximum agility when solving a problem on a client, but also code changes are integrated into the code repository in an organized way.

Ticket creation and classification process

Any member of the company (including salespeople) can create a ticket in GitLab. This includes customers and partners, although in their case there is a prior filter by the support team and the sales team respectively.

The more detailed the ticket, the more unequivocal the development will be. Add images, gifs, animations and all the necessary clarifications. As well as the way to access the environment where the problem has been found or the contact persons. A developer will never contact a customer directly. If there is the need to interact with them, it will be done through the support or project team.

Nobody, except for the DM or PO, can change a ticket milestone. On creation, the ticket will not have an assigned milestone or assigned user. The task of defining which release a ticket belongs to is the responsibility of PO and DM exclusively.

When a ticket is finished and the developer thinks it should be reviewed by a colleague, they mention it in the merge request through @xxxxx. The review must be nominal. This review is independent of the code review carried out by the department manager.

General ticket workflow

  • The ticket is assigned to a programmer by the DM. If it does not have a ticket assigned, the ticket will be auto-assigned. (See below the terms that regulate this system).
  • The developer must understand/solve any questions that may arise after reading the functional document, if necessary, check with the DM or the author of the ticket. This must be done before starting to develop. Once read, you must, in order:
  1. Evaluate (by assigning labels) its complexity and size, reaching a prior consensus with the DM.
  2. Develop the feature following the ticket specifications
  3. Document everything developed in the same ticket or, if required, in a new documentation ticket. This ticket must relate to the “parent” ticket by ticket #ID.
  4. The developer must test its functionality at least in:
    -standard docker development environment
    -docker development environment with data.
  • When it is deemed complete, it will be tagged ~ QA Pending and placed in the hands of QA.
  • For each FEATURE ticket, there will be a reference person, generally from projects, support or even the PO itself. This person will be the one who will define part of the functional (together with the DM and PO), but above all, this person will be the reference person for the developer to ask any details during development, and most importantly, should see the development progress, step by step, so that it is validated.
  • Any change to the functional will be reflected by the reference person in the ticket as comments, without altering the original functional.
  • If there is a child documentation ticket, QA will validate the ticket using the documentation generated by the reference person, NOT by the functional of the ticket, validating the documentation and the feature at the same time.

Release planning

When creating a ticket, the milestone must be empty (not assigned) like the user. The only ones that can classify a ticket are: DM and PO.

A series of milestones have been defined to support the ticket classification process, some of them, those dated (releases), can be seen as milestones, while the rest should be seen as simple ticket containers.

  • (Not allocated): It is the absence of milestones in a ticket. For all intents and purposes, this ticket “does not exist yet.” The DM and PO will validate each and every one of these tickets to see if they make sense in the product roadmap. No developer should take any of these tickets.
  • Feature backlog: Tickets that will be made at some indeterminate time in the future that sooner or later will have to be addressed. No developer should take any of these tickets.
  • Low priority bugs: Reported bugs with no priority assigned yet by PO/DM. No developer should take any of these tickets.
  • STAGE: Tickets proposed by each department for planning in a product release. At each planning meeting, these tickets will be discussed, and moved to other milestones. At the end of the cycle start meeting, this milestone should be empty. The DM is the one who has the final decision as to which STAGE tickets are assigned to a certain release and which are not, relying on the product committee if necessary. No developer should take any of these tickets.
  • XXX: Release XXX. Milestone that groups a series of tickets that will be released on a certain date. A milestone has a deadline associated with it. In the case of RRR releases, this date could change, in the case of LTS not.
  1. The development of the tickets associated with a release must be finished 5 days before the scheduled day for the release. Tickets not completed before that date will be delayed to the next release and the delay will have to be justified to the DM.
  2. There are two types of release milestones:
    -LTS: in April and November. They are 6 months apart.
    -Regular Releases (RRR): There will be 2 to 4 regular releases between LTS releases.
  • A developer with no assigned tasks for a release, as long as there are no pending assignment tickets in the release milestones for the developer’s team, can take one of the unassigned tickets from:
    -The closest release, based on date.
    -Second closest release, based on date.

CICD

Pandora FMS developers integrate the code of their branches in a central repository several times a day, causing a series of automatic tests to be executed whose objective is to detect faults as soon as possible and improve the quality of the product.

These tests run dynamically in a series of executors or “runners”, some of them specific, for certain architectures (e.g., ARM), that execute static code analyzers, unit tests, and activate containers to carry out integration tests in a real installation of the application.

The generation of Pandora FMS packages is completely automated. Packages are generated every night from the development branch for manual testing. They can also be generated on demand by any developer or member of the QA or support teams, from any branch through the GitLab web interface.

When a release is made from the stable branch, in addition to package generation, a series of steps are executed that deploy them to Ártica’s internal package server, to SourceForge, to Ártica’s customer support environment, and that, likewise, update the Debian, SUSE and CentOS repositories along with the official Docker images.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About PandoraFMS
Pandora FMS is a flexible monitoring system, capable of monitoring devices, infrastructures, applications, services and business processes.
Of course, one of the things that Pandora FMS can control is the hard disks of your computers.

數字化轉型時期的主動監控

Pandora FMS is a proactive, advanced, flexible and easy-to-configure monitoring tool according to each business. Pandora FMS integrates with the needs of the business, being able to monitor servers, network equipment, terminals and whatever is necessary.

In this article we will focus on monitoring using Pandora FMS, bearing in mind the new reality, which has arrived to stay, known as “Digital Transformation”.

Digital Transformation

First of all, let’s start by understanding what Digital Transformation is all about, a widely used term, but at the same time somewhat confusing for many people, due to its broad definition.

Digital transformation is a concept that encompasses the integration of the different technologies, used in the different areas of a company, fundamentally changing the way it works and delivers value to its customers. It is also a cultural shift that requires organizations to constantly challenge the status quo, experiment, and feel comfortable with the change.

It is not new that technology advances faster and faster generating a constant challenge, that is why we must be on the watch for these advances, to be able to adopt new technologies and achieve the cycle of “Continuous Improvement”, taking advantage of the tools that allow us to be more and more efficient.

As part of this change, there are key technologies that allow us to digitize our information and adapt to this new reality that is here to stay.

  • Cloud Computing (Amazon AWS, Microsoft Azure, Google Cloud): It gives your organization faster access to the software it needs, new features and updates, as well as data storage. Cloud computing allows you to be agile enough to transform quickly.
  • Information technology: It allows an organization to focus its investment on talent, research and development, and customized solutions that support the requirements and processes that differentiate it in the market.
  • Machine learning and artificial intelligence technologies: They provide organizations with more accurate information for decision-making on sales, marketing, product development and other strategic areas.
  • Other technologies that drive business transformation are: blockchain, blockchain, augmented reality and virtual reality, social networks, and the Internet of Things (IoT).

Since the beginning of computing, companies had at least one server/computer as part of their daily tasks. This implied additional tasks such as: technical support, and infrastructure maintenance.

Some years ago, it was common to find email servers, installed in the company, generating the great challenge to keep a critical service, like this one, running 24/7. Today there are private cloud solutions such as: Microsoft 365 or Google Apps, that allow you to have email with a very high SLA, without the need for your own infrastructure, using the service as SAAS (Software as a Service).

To understand where we are at and where to start, with the digital transformation process, we are going to explain the four most common infrastructure scenarios:

On-Premise (Local Infrastructure): Servers that work in the company and require a great effort to maintain them.

IaS Cloud (Infrastructure as a Service): In this scenario, virtual machines can be run in the cloud, such as, for example, a Windows Server, some Linux distribution where you install the essential tools to use the corporate application that you need to use. The provider ensures the availability of the virtual machine and the company is responsible for the software that is installed. In this case, Amazon AWS, Microsoft Azure, Google Cloud, etc. can be used.

PaaS Cloud (Platform as a Service): Services that work in the cloud and that have a platform such as: SQL Server, Oracle, SAP, Docker, Etc.

SaaS Cloud (Software as a Service):
 Services that work in the cloud and have a management tool, such as Exchange Online, Google Apps (Corporate Gmail), OneDrive, Google Docs, Etc.

After this introduction, we are going to understand the value of Pandora FMS for any of the previous scenarios, at the time of Digital Transformation.

Some time ago, we already published an article on this blog with the installation script for IaS Cloud. As a requirement you need to have a Virtual Machine with CentOS 7, which has 2 GB of RAM and 20 GB of Disk.

Executing the following command: curl -Ls https://pfms.me/deploy-pandora | sh on a computer that has an Internet connection, you will obtain an installation of Pandora FMS Community in an On-Premise scenario or in the cloud that you use:

https://pandorafms.com/community/get-started/

For the Enterprise version, we have a Free 30-day Trial. 

Now that you know that you can install Pandora FMS in the scenario that is most convenient for you, we are going to see which are the required ports to be able to use the tool from a public cloud:

PortDescription
443 TCP (https)WEB console
41121 TCP (Tentacle)Software Agent Connection/td>

With this configuration you can use Pandora FMS key features. We are going to see just a few of them. Very useful for this reality of continuous changes.

Remote Configuration, Policies and Collections: With this configuration you can make all the changes on the monitoring agents, using Pandora FMS web console, being able to build the Agent Plugins and distributing them in a centralized and simple way.

Agents with Remote Configuration

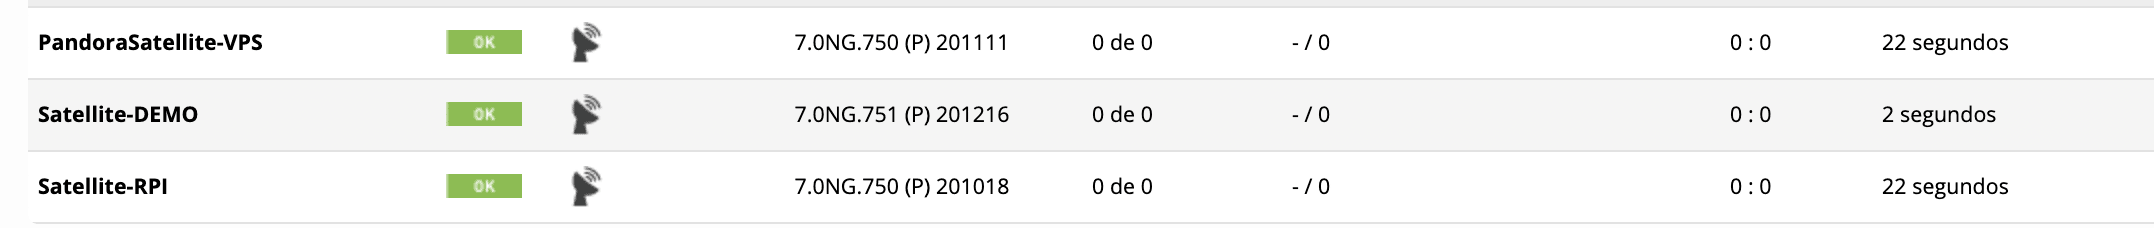
Satellite Server: A very interesting possibility is to set up an agent with advanced features. It allows you to discover the different remote networks, servers, and network computers, using ICMP, SNMP and WMI protocols. It is not necessary to open any ports on the firewall, where the Satellite Server is installed. You have the possibility of reaching Pandora FMS server with port 41121 TCP Tentacle and, for example, remotely monitor the devices from the different locations and/or branches.

 Several Satellite Servers, reporting to a console in Azure


Ubiquiti AP UC-AC-LR (Satellite through SNMP)

Pandora FMS Ubiquiti AP UC-AC-LR Web Console

https://pandorafms.com/docs/index.php?title=Pandora:Documentation_es:Arquitectura#Servidor_Sat.C3.A9lite

Finally, and as a complementary tool, you can count on the possibility of having usage and consumption metrics in the cloud, from the “Discovery” option, or with add-ons from the Enterprise library.

Discovery Cloud View

At the time I wrote this article, the clouds supported by Pandora FMS were:

*It is possible that new cloud technologies will be added over time.

In the next tree view you can see some of the metrics that we have available for AWS and Azure. In this view, you can see the status of the virtual machines, the consumption of Network, Memory, etc.
All these parameters are configured according to the specific needs of each client.

https://pandorafms.com/docs/index.php?title=Pandora:Documentation_en:Discovery#Discovery_Cloud (Discovery Cloud Documentation)

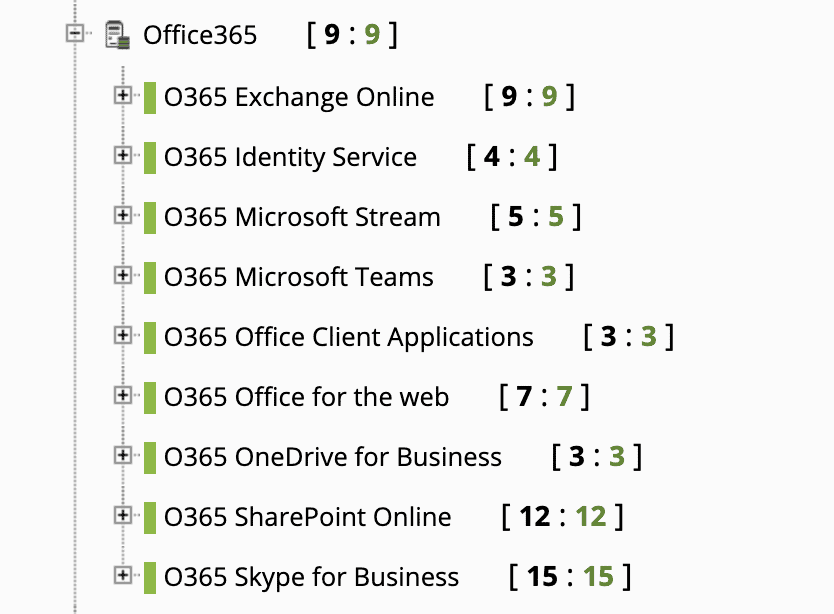
Finally, Microsoft 365 cloud has an API to be able to monitor the health status of its services. Pandora FMS has a plugin in the Enterprise library that allows you to collect data from the Microsoft 365 API.

https://pandorafms.com/library/pandora-office-365-monitoring/

Partial View of Microsoft 365 Services

I hope this article was useful for you to understand what the best monitoring scenario for your company is.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About PandoraFMS
Pandora FMS is a flexible monitoring system, capable of monitoring devices, infrastructures, applications, services and business processes.
Of course, one of the things that Pandora FMS can control is the hard disks of your computers.

什麼是新的 Pandora FMS 754

What’s new in Pandora FMS latest release, Pandora FMS 754

Let’s take a look together at the features and improvements included in this new Pandora FMS release: Pandora FMS 754.

NEW FEATURES AND IMPROVEMENTS

Metaconsole Dashboards

Dashboards can now be used within the Metaconsole, to be able to centrally manage all the information more visually.

New AWS monitoring. Amazon S3

The possibility of monitoring Amazon S3 cubes has been added to be able to monitor the files they include, the size of each file, the number of items in each cube, permissions, etc.

New installers for Cloud

In previous versions, we prepared a remote script to install Pandora FMS in any environment: virtual, cloud or physical, by just having access to the internet. In this version, we have done the same to install Pandora FMS agents, in a customized way with just one click.

Check out the documentation or try it yourself:

curl -Ls https://pfms.me/agent-deploy | bash

Improved event widget in Dashboard

It now allows you to incorporate saved filters, so that the widget will show events using those custom filters.

Release-754

Visual enhancements to console settings

Pandora FMS console setup display has been improved to not show anymore all the options in a single column and thus be able to see it more easily and quickly.

Release-754

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About PandoraFMS
Pandora FMS is a flexible monitoring system, capable of monitoring devices, infrastructures, applications, services and business processes.
Of course, one of the things that Pandora FMS can control is the hard disks of your computers.

ESET發現EmissarySoldier:LuckyMouse APT小組破壞了中亞和中東的政府網絡和私人公司(電信,媒體和銀行)

The research featured in ESET’s industry report on government works in concert with perspectives from the European Commission, CERN and Europol presented at the ESET European Cybersecurity Day virtual conference on April 28.

BRATISLAVA – The European Union’s cybersecurity strategy, and that of all governments globally, has been challenged not only in its move to “digital by default,” but also by the COVID-19 pandemic, the mass movement to working from home, and threats such as cyberespionage, ransomware and supply-chain attacks. Above all, the most formidable challenge, and foe, shared by all governments is advanced persistent threat (APT) groups.

APT groups leveraging evolved tools
The ESET industry report on government examines the threatscape APT actors are erecting, and underlines its complex nature with an exclusive look at EmissarySoldier, a malicious campaign brought to bear by the LuckyMouse APT group using its SysUpdate toolkit to compromise machines, some of which were running the popular application Microsoft SharePoint.

This dive into LuckyMouse examines its relatively unknown SysUpdate toolkit – the first samples of which were discovered in 2018. Since then, the toolkit has seen various development stages. LuckyMouse’s current modus operandi is to install its implants via a so-called trident model that uses three components: a legitimate application vulnerable to DLL hijacking, a custom DLL that loads the payload and a raw Shikata Ga Nai-encoded binary payload.

Overview of the trident model

Since SysUpdate’s modular architecture enables its operators to limit exposure of malicious artifacts at will, ESET researchers did not retrieve any malicious modules and expect this to be an ongoing challenge in future analyses. Regardless, LuckyMouse increased its activity in 2020, seemingly going through a retooling process where various features were being incrementally integrated into SysUpdate’s toolset.

The evolution of tools leveraged by APT groups like LuckyMouse is of key concern as governments are vested with the responsibility to ensure stability for citizens, the business environment and engagement with other nation-states. These tasks of governance are under threat as LuckyMouse and other APT groups, including state actors and their collaborators, home in on widespread collaboration platforms like Microsoft SharePoint and digital by default service provision.

Government in focus
The years 2020 and 2021 have seen several ESET research collaborations come to maturity, including engagements with the likes of the European Organization for Nuclear Research (CERN, Europol, and the French National Cybersecurity Agency (ANSSI). Many of their perspectives, shared at the virtual event and in the report, stress that governments and their IT infrastructure exist as default targets.

The report highlights the need for technologists to continue supporting governments in closing security gaps and monitoring the tactics, techniques and procedures of APT groups via the various endpoint detection and response technologies at their disposal. To download the report, visit WeLiveSecurity.com and make sure to follow ESET Research on Twitter.

關於 Version 2 Digital

資安解決方案 專業代理商與領導者 台灣二版 ( Version 2 ) 是亞洲其中一間最有活力的 IT 公司,多年來深耕資訊科技領域,致力於提供與時俱進的資安解決方案 ( 如EDR、NDR、漏洞管理 ),工具型產品 ( 如遠端控制、網頁過濾 ) 及資安威脅偵測應 變服務服務 ( MDR ) 等,透過龐大銷售點、經銷商及合作伙伴,提供廣被市場讚賞的產品及客製化、在地化的專業服務。

台灣二版 ( Version 2 ) 的銷售範圍包括台灣、香港、中國內地、新加坡、澳門等地區,客戶涵 蓋各產業,包括全球 1000 大跨國企業、上市公司、公用機構、政府部門、無數成功的中小企業及來自亞 洲各城市的消費市場客戶。

關於ESET
ESET成立於1992年,是一家面向企業與個人用戶的全球性的電腦安全軟體提供商,其 獲獎產品——NOD32防病毒軟體系統,能夠針對各種已知或未知病毒、間諜軟體 (spyware)、rootkits和其他惡意軟體為電腦系統提供實時保護。ESET NOD32佔用 系統資源最少,偵測速度最快,可以提供最有效的保護,並且比其他任何防病毒產品獲 得了更多的Virus Bulletin 100%獎項。ESET連續五年被評為“德勤高科技快速成長500 強”(Deloitte’s Technology Fast 500)公司,擁有廣泛的合作夥伴網絡,包括佳 能、戴爾、微軟等國際知名公司,在布拉迪斯拉發(斯洛伐克)、布里斯托爾(英國 )、布宜諾斯艾利斯(阿根廷)、布拉格(捷克)、聖地亞哥(美國)等地均設有辦事 處,代理機構覆蓋全球超過100個國家。