Skip to content

為了打擊勒索軟件黑客,耗盡了加密貨幣沼澤

This kind of digital extortion – increasingly viewed as terrorism – would be impossible without the ability to move money around anonymously

Last month, a cybercriminal group penetrated the Colonial Pipeline. This wasn’t just “another” hack, with privacy consequences and threats on personal information. The severe results were shown instantly. Gas supply to millions of Americans was disrupted leading to a spike in gas prices and panic buying causing local fuel shortages in the southeast, and resurfacing old memories of the infamous gas crisis in the US in the late 1970s.

It becomes evident, and not for the first time, that ransomware has the potential to affect the personal lives of innocent citizens tremendously. The problem is worsening by the day as groups improve their ransomware code and collect easy money.

The US authorities responded – a national cyber investigative task force was formed and last night, DOJ told Reuters that US authorities will “give ransomware hacks similar priority as terrorism”. This begs the question, however: will it be possible to stop ransom hacks without treating its originator?

The fact is we’re not looking at this problem holistically. There is one factor making this problem possible, and systemic: cryptocurrency. Ransomware hacks thrive due to the possibility to transfer cryptocurrency easily, rapidly and without leaving traces. The criminals are not required to deal with complex transfers. Gone are the days where hostage-takers demand one million dollars in small-unranked-paper-bills, with a jet on the runway ready to take them to some foreign land where there’s no extradition agreement. All they need is a Bitcoin address, Monero, or ZCash, and a few command lines – and voila – the money lands safely at the hands of the criminals. It’s almost a sterile crime.

In fact, those money transfer machines enable the prosperity of a global crime industry, fueled by corporate extortion funds. For instance, in the case of the Colonial Pipeline, despite the involvement of the FBI and the law authorities, a five million dollar ransom was paid in order to free the systems. Some of the funds were recovered, in an unprecedented operation, and yet, the damage remained.

This is not pocket change. Each win – no matter how financially lucrative – builds on itself and gives these cybercriminals more confidence to fuel the next attack. For example, in dark web forums the phenomenon of “ransomware hack as a service” is gaining popularity, and criminals are offering ransomware for rent. The thieves have become so contented, that they are allowing others to use their tools, while they’re resting safely as ordinary software vendors.

In order to stop terror, we have to stop its funding. However, when it comes to ransomware hacks there is still no internalization of the fact that strict limitations should be put on its primary funding source – cryptocurrencies. The promise for liberty and freedom from censorship made by theoreticians in this field are shattered daily, and instead of a paradise for innocent civilians, we’re left with the opposite – a utopia for criminals. In fact, untraceable cryptocurrencies are the swamp in which the disease of ransomware flourish.

This swamp must be dried up. If governments around the world seriously intend to stop the phenomenon of ransomware hacks, they have to put strict limitations on money transfers via crypto currencies. They must supervise cryptocurrencies the same way they do with cash, bank transfers, diamonds or weapons. Countries should demand users to expose their money sources and prevent them from doing major deals not conducted through the supervised international banking system.

Governments should also implement methods of tracking cryptocurrencies and sound the alarm when illegal activity is detected. If they cannot decide on or implement a system to administer this, governments should consider the unpopular step of complete prohibition of holding and trading cryptocurrency. Drying up of the funding sources for these attacks may be the only viable approach to stop their continued proliferation. If we do not take immediate action to dry those swamps, we will find ourselves in the near future too weak and too ill to recover.

Originally posted on Times of Israel

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

About CDM InfoSec Awards
This is Cyber Defense Magazine’s ninth year of honoring global InfoSec innovators. Our submission requirements are for any startup, early stage, later stage or public companies in the INFORMATION SECURITY (INFOSEC) space who believe they have a unique and compelling value proposition for their product or service. Learn more at http://www.cyberdefenseawards.com

About the Judging
The judges are CISSP, FMDHS, CEH, certified security professionals who voted based on their independent review of the company submitted materials on the website of each submission including but not limited to data sheets, white papers, product literature and other market variables. CDM has a flexible philosophy to find more innovative players with new and unique technologies, than the one with the most customers or money in the bank. CDM is always asking “What’s Next?” so we are looking for Next Generation InfoSec Solutions.

About Cyber Defense Magazine
With over 5 Million monthly readers and growing, and thousands of pages of searchable online infosec content, Cyber Defense Magazine is the premier source of IT Security information for B2B and B2G with our sister magazine Cyber Security Magazine for B2C. We are managed and published by and for ethical, honest, passionate information security professionals. Our mission is to share cutting-edge knowledge, real-world stories and awards on the best ideas, products and services in the information technology industry. We deliver electronic magazines every month online for free, and special editions exclusively for the RSA Conferences. CDM is a proud member of the Cyber Defense Media Group. Learn more about us at https://www.cyberdefensemagazine.com and visit https://www.cyberdefensetv.com and https://www.cyberdefenseradio.com to see and hear some of the most informative interviews of many of these winning company executives. Join a webinar at https://www.cyberdefensewebinars.com and realize that infosec knowledge is power.

RADIUS 身份驗證,現在在雲端

Understanding RADIUS Authentication

Remote Authentication Dial-In User Service (RADIUS) is a protocol that was historically designed to authenticate remote users to a dial-in access server. Today, RADIUS authentication is used across an array of scenarios and is well known for it AAA capabilities — authentication, authorization, and accounting. By centralizing AAA capabilities, organizations give themselves improved security and greater efficiency. RADIUS servers provide each business with the ability to preserve the privacy and security of both the system and each individual user.

A basic RADIUS accounting process includes:

  1. The process starts when the user is granted access to the RADIUS Server.
  2. The RADIUS Client sends a RADIUS Accounting-Request packet known as Accounting Start, to the RADIUS Server. The request packet comprises the user ID, network address, session identifier, and point of access.
  3. During the session, the Client may send additional Accounting-Request packets known as Interim Update to the RADIUS Server. These packets include details like the current session duration and data usage. This packet serves the purpose of updating the information about the user’s session to the RADIUS Server.
  4. Once the user’s access to the RADIUS Server ends, the RADIUS Client sends another Accounting-Request packet known as Accounting Stop, to the RADIUS Server. The packet includes information such as total time, data, and packets transferred the reason for disconnection, and other information relevant to the user’s session.
  5. Ultimately, RADIUS authentication prevents your organization’s confidential data from being leaked. It also allows easy depreciation capabilities and enables individual users to be assigned with unique network permissions based on their location, role, etc.

RADIUS Authentication in the Cloud

It’s well known today that RADIUS authentication is an effective way of enhancing network security, visibility and control. Just as more and more organizations move their enterprise software stack to the cloud, so too are they demanding flexibility and ease of deployment as it relates to RADIUS. This has given rise to the cloud RADIUS, a modern take on the traditional on-premise RADIUS server.

Standing up a cloud RADIUS offers several benefits for your organization, including:

  • Built-in redundancy
  • Ease of deployment
  • Cost efficiency
  • Auto-scaling
  • ..the list goes on…

For these reasons, network engineers are turning cloud RADIUS solutions in droves. And as vendors like Portnox continue to make advances in machine learning, the reliability and feature sets of cloud RADIUS options become more and more appealing.

Portnox CLEAR’s Cloud RADIUS

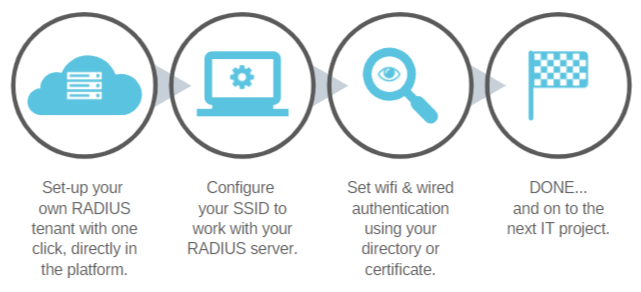
Securing your network will always be a priority – no doubt one of many priorities your IT team is faced with – but it doesn’t need to be a drain on time and resources. With Portnox’s RADIUS-as-a-Service solution, companies can now efficiently and affordably authenticate to wifi, VPN, switches and network devices, while simplifying administration and enabling long-term scalability.

Tired of all the heavy lifting when it comes to standing up RADIUS servers? We feel your pain, that’s why we’re making it easier than ever to securely authenticate and control wired and wireless network access for all your users and devices.

How it Works

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

美國著名大學利用 Cloud NAC 克服網絡訪問挑戰

The University of Denver is a leading private research institution in the United States with nearly 13,000 undergraduate and graduate students, and roughly 4,300 staff members. The university has a prestigious reputation, often ranking among the top 100 universities in the country, and is the oldest research institution in the Rocky Mountain Region of the U.S.

In late 2019, the University of Denver’s information security team, led by Marcelo Lew, went out in search of a network access control solution to help manage access to the institution’s guest network, as well as to its growing eduroam WiFi network roaming service. “Internally, we had an initiative to move our security stack to the cloud,” Lew said. “We’re really focused on bringing in solutions that are lightweight and don’t require an FTE to come in and manage them.”

Choosing Simplicity in Uncertain Times

As an existing HPE Aruba ClearPass customer, and having evaluated Cisco’s Identity Services Engine (ISE) NAC solution, Lew and his team felt that Portnox CLEAR had the potential to deliver the needed functionality without all of the heavy systems lifting to stand up and maintain required of traditional on-premise NAC. “Some of the legacy NAC solutions out there have a million knobs, making them complex to configure and difficult to troubleshoot. Most institutions like us don’t need all of that,” Lew continued.

aruba clearpass replacementLew and his information security team set their sights on Portnox CLEAR NAC-as-a-Service, moving to a PoC in early 2020. The untimely rise of the Coronavirus pandemic in March of 2020 in the U.S. put a damper on the team’s initial efforts to test the platform. “COVID-19 forced the PoC to take a bit longer due to operational challenges, but in general, we really liked what we saw,” said Lew. “Portnox CLEAR really had the potential to get us where we wanted to be with regards to moving NAC to the cloud.”

Coverage for the Guest Network

Portnox CLEAR would eventually be rolled out in full across the university’s guest network, with full coverage up to 10,000 devices. “We have hundreds and even thousands of users on our guest network at any given time. We’ve had no issues and our network engineers have found Portnox CLEAR very easy to configure. The team particularly likes that there’s no on-prem component or need to upgrade servers on a regular basis,” Lew went on to say.

Starting with the guest network was a strategic decision. The university often hosts conferences and events with thousands of non-staff visiting for the day and needing wireless connectivity, making the guest WiFi network target number one for potential cyber threats. “We’re also situated in a populated neighborhood community in Denver. We’re fine with the community being able to utilize our WiFi, but we needed a mechanism to allow for this while keeping the university’s data safe,” said Lew. “After all, our motto here is A Private University Dedicated to the Public Good – that concept extends to our network as well.”

cloud nacExpanding to Eduroam & Beyond

As Lew and his team look ahead, they plan to extend CLEAR’s access control capabilities to the university’s eduroam wireless network used by staff, as well as to the many wired ports across the campus. “We have a few quiet periods during the year where network activity is low – typically in the summer, and about 3-4 weeks in December. We’re planning to tackle eduroam coverage with Portnox CLEAR in the fall of 2021, and the wired ports over the Christmas break,” said Lew.

The move off of its reliance on HPE Aruba ClearPass for NAC to Portnox’s cloud-delivered NAC-as-a-Service signifies a larger initiative within the institution even beyond cloud transformation. “The hard perimeter-based security approach doesn’t work anymore because devices are no longer limited to the university network,” Lew continued. “So, we cannot assume that everything inside the perimeter (or enterprise firewalls) is safe. We are working towards a zero trust but always verify environment, where for users like campus guests are given the minimum possible access needed.”

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

Portnox在2021年RSA大會上被提名為令人垂涎的全球InfoSec獎的獲勝者

Portnox Wins Award for “Cutting Edge NAC” in 9th Annual Global InfoSec Awards at RSAC 2021


NEW YORK–Portnox is proud to announce it has won the award for “Cutting Edge Network Access Control (NAC)” from Cyber Defense Magazine, the world’s leading information security e-magazine. “We’re thrilled to receive one of the most prestigious and coveted cybersecurity awards in the world from Cyber Defense Magazine. We knew the competition would be tough – after all, the judges are leading infosec experts from around the globe. We couldn’t be more pleased,” said Ofer Amitai, CEO at Portnox.

Portnox’s cloud-delivered NAC-as-a-Service – Portnox CLEAR – has taken the network access control (NAC) market by storm in recent years, seeing a surge of new customers seeking to move off of their legacy on-premise NAC solutions. In 2020, Portnox saw its revenue grow 30% year-over-year.

“As the only true SaaS NAC product on the market, Portnox CLEAR is making NAC implementation and deployment easier for enterprises – particularly those with highly distributed networks,” said Tomer Shemer-Buchbut, Vice President of Products at Portnox. “By eliminating on-going maintenance like upgrades and patches common of on-premise NAC, we’re offering companies far better total cost of ownership.”

“Portnox embodies three major features we judges look for to become winners: understanding tomorrow’s threats, today, providing a cost-effective solution and innovating in unexpected ways that can help stop the next breach,” said Gary S. Miliefsky, Publisher of Cyber Defense Magazine.

With 80 billion connected devices expected to be in use by 2025, the NAC market is growing rapidly – projected to reach nearly $12 billion globally. Device proliferation paired with an ever-expanding number of cyber threats and hybrid workforce operations has made network access control a critical component of any enterprise cybersecurity stack. “NAC is front and center for CISOs and their IT security teams. Expect the demand for network access control – particularly cloud NAC – to continue to grow as companies continue to embrace emerging networking models like SD-WAN, ZTNA and SASE,” said Amitai.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

About CDM InfoSec Awards
This is Cyber Defense Magazine’s ninth year of honoring global InfoSec innovators. Our submission requirements are for any startup, early stage, later stage or public companies in the INFORMATION SECURITY (INFOSEC) space who believe they have a unique and compelling value proposition for their product or service. Learn more at http://www.cyberdefenseawards.com

About the Judging
The judges are CISSP, FMDHS, CEH, certified security professionals who voted based on their independent review of the company submitted materials on the website of each submission including but not limited to data sheets, white papers, product literature and other market variables. CDM has a flexible philosophy to find more innovative players with new and unique technologies, than the one with the most customers or money in the bank. CDM is always asking “What’s Next?” so we are looking for Next Generation InfoSec Solutions.

About Cyber Defense Magazine
With over 5 Million monthly readers and growing, and thousands of pages of searchable online infosec content, Cyber Defense Magazine is the premier source of IT Security information for B2B and B2G with our sister magazine Cyber Security Magazine for B2C. We are managed and published by and for ethical, honest, passionate information security professionals. Our mission is to share cutting-edge knowledge, real-world stories and awards on the best ideas, products and services in the information technology industry. We deliver electronic magazines every month online for free, and special editions exclusively for the RSA Conferences. CDM is a proud member of the Cyber Defense Media Group. Learn more about us at https://www.cyberdefensemagazine.com and visit https://www.cyberdefensetv.com and https://www.cyberdefenseradio.com to see and hear some of the most informative interviews of many of these winning company executives. Join a webinar at https://www.cyberdefensewebinars.com and realize that infosec knowledge is power.

Portnox CLEAR與本地NAC:總擁有成本(TCO)

On-Premise NAC vs. SaaS NAC


Set-Up & Configuration

Unlike traditional on-premise NAC solutions that require hardware appliances, software, and other on-premise elements, you can create your dedicated instance of Portnox CLEAR cloud-delivered NAC-as-a-Service in minutes.

Portnox CLEAR has been built from the ground up to simplify policy configuration, allowing for deployment timelines that can be measured in hours. In contrast, traditional on-premise NAC deployments can be measured in weeks or months.

Set-Up Costs Eliminated with Portnox CLEAR: Need for on-site appliances, need for third-party expertise, man-hours dedicated to systems training

Savings Value: HIGH


Scalability & Performance

As a cloud service, Portnox CLEAR eliminates the need for the capacity planning of on-premise NAC software or appliances. It also eliminates the need to expand capacity or upgrade appliances to meet future growth needs as required by traditional on-premise NAC.

Portnox CLEAR can automatically control the virtual machine size and the scale up or down rules. Dedicated F5 load balancers are spun up as well as auto-scale, so you never have to be concerned with service performance or scalability – it will automatically expand as needed to meet demand.

Performance Costs Eliminated with Portnox CLEAR: Man-hours dedicated to capacity planning, need for on-site appliance upgrades, need for local load balancing

Savings Value: MODERATE


Lifecycle Maintenance

Another hidden cost of on-premise is maintenance. All you have to do is search the web – in most cases you’ll find that vendors have lengthy manuals that outline the painful steps and procedures necessary to keep the software or its associated appliances updated.

These upgrades often come with time limits that can force you to start over and re-do your work. Worse yet, one simple mistake during these upgrades can take your network down for many hours or days. And guess what? You often get to go through these upgrades multiple times per year.

With Portnox CLEAR, never worry about software or hardware end-of-life, or costly, complex upgrades requiring hours and days of work and a never-ending checklist of to-dos. As a cloud-delivered service, Portnox CLEAR is always running the most up-to-date version with the latest features and capabilities. At the end of the day, Portnox CLEAR customers enjoy continuous service availability with ZERO lifecycle maintenance costs.

Maintenance Costs Eliminated with Portnox CLEAR: Software upgrades, NAC downtime, need for third-party expertise

Savings Value: HIGH

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

作為數字轉型的一部分,大型活動場地從本地遷移到雲NAC

Founded in 2004 and located in the heart of Cardiff Bay, Wales Millennium Centre (WMC) is Wales’ national arts centre and a major events venue in the region. It seats nearly 2,500 guests, and hosts events ranging from performances by the Welsh National Opera, to concerts, West End musicals, an annual arts festival and more.

Increasingly Cloud-Friendly

WMC has been a long-standing customer of Portnox, having signed on to use Portnox CORE, our on-premise network access control (NAC) solution, in 2012. By early 2020, however, WMC was in the midst an internal push for digital transformation, which focused on adopting cloud technologies in exchange for existing legacy on-premise systems. “Moving from on-prem to cloud is something we’ve begun to undertake over the last year across nearly every system that we use,” said Richard Williams, IT Infrastructure Engineer.

After migrating WMC’s payroll system to the cloud, with several other systems also awaiting migration, Williams and his team began to assess the venue’s current cybersecurity posture. “For a while now, I have been looking at various aspects of security across our business. We’re looking to tighten things up, and much of that has begun with training for staff, such as teaching people to be more aware of phishing emails, etc. It’s now time to begin really assessing the systems we have in place, particularly when it comes to network security,” Williams continued.

As the team turned its focus to its existing network access control capabilities with Portnox CORE, it decided that this component of the cybersecurity stack should also migrate to cloud NAC as part of the WMC’s digital transformation program.

Elevating Network Security

As a public venue, WMC is open to a variety of non-staffers for long periods of time throughout the day. “On a daily basis, we have large numbers of contractors, performers – all kinds of people in the backstage area – and historically we had limited visibility of what was being plugged into our network,” Williams went on to say.

With a number of wired ports located throughout the building, as well as a guest wireless network that was freely accessible, this limited visibility meant that WMC’s network was especially vulnerable and could potentially be breached by anyone with a moderate level of IT know-how.

“While we hadn’t fully leveraged all of the functionality available to us within Portnox CORE, I knew that Portnox CLEAR would be a much better fit for us as an organization after seeing it in action,” Williams stated. “With Portnox CLEAR, we can simply login and see exactly who is on the network, via which access layer, their device type, etc. We have much more visibility and control today as a result.”

Better Agility & Visibility in Times of Crisis

As the Coronavirus pandemic unexpectedly swept the globe in the early months of 2020, WMC’s choice to transition to Portnox CLEAR’s cloud NAC yielded a surprising benefit. “As a public events venue that had to shut its doors for several months due to the pandemic, we were forced to downsize our staff and send most of the remaining workforce home to continue operations,” Williams went on to say.

With an uncharacteristically large remote team, Williams and his colleagues were able to extend Portnox CLEAR’s NAC capabilities to the organization’s VPN access layer, ensuring that the corporate network, resources and various enterprise cloud applications were being accessed by remote staff in a secure manner.

Future-Proofed for Whatever Lays Ahead

While the future for nearly every organization remains uncertain as the pandemic drags on, Williams and WMC are confident that Portnox CLEAR will continue to deliver the needed stability, visibility and control it requires to keep its network safe. “From the end-user’s point-of-view, Portnox CLEAR is very stable. My team connects to CLEAR first thing in the morning, and simply disconnects at the end of each day. Now, we always know what’s happening on the network. There are no blind spots,” Williams explained.

cloud nac visibility security

With Portnox CLEAR cloud NAC, WMC is future-proofed for any new network security challenges that lie ahead, thanks to the platform’s superb uptime, on-going upgrades, and flexibility to manage from anywhere if needed.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

網絡安全的未來:身份,分段和邊緣保護

What it takes to properly secure corporate networks in the world of remote work, BYOD & IoT

The workplace has changed thanks to COVID-19. Many of us continue to spend most, if not all, of our workdays at home, juggling Zoom meetings, kids, pets, relationships, cooking, cleaning…you name it. Since at least February 2020, organizations around the world have altered the way they operate – encouraging their employees to stay home, stay safe, but stay available.

On top of the immediate operational challenges that companies faced when shifting to full or hybrid work environments, the rise of remote work in response to COVID-19 has pushed a number of network security shortcomings to the surface. In response, cybersecurity vendors and IT professionals have accelerated the development of and search for solutions to fill these network security gaps.

As we return to the office and arrive in a post-COVID-19 world, these areas will dominate the evolutionary direction of corporate network security…

The Role of Identity

As people, we represent the weakest link in the network security armor. While we may wish we were infallible, we’re really full of bad cybersecurity habits, like weak passwords, forgetting to back up data, or clicking on hyperlinks in emails from strangers. Our identities, however, can also be our strongest means of securing networks. The rise of multi-factor authentication (MFA) identity and access management (IAM) tools is allowing organizations to verify employee identity and authenticate their access to the network in real-time, no matter the employee’s location or whether they’re attempting to connect with a managed or personal (BYOD) device.

Network Segmentation

Segmenting the network is a cybersecurity best practice. Period. For any companies, this practice is even a regulatory requirement (e.g., the Payment Card Industry data security standard (PCI)). Network segmentation is simply a means of dividing up a network into smaller parts, ensuring the right people only have access to the parts of the network that are relevant to them. It is a measure that improves the effectiveness of an organization’s investments in other security tools, and can help to prevent significant damage to critical data across the network after a company has experienced a breach.

Securing the Edge

Gartner introduced SASE a few years ago. It represents a new enterprise networking technology category that converges the functions of network and security solutions into a single, unified cloud service. This marks an architectural transformation, as it allows IT teams to leverage a holistic and flexible service to their businesses. Critical to this budding area is NAC. Specifically, the movement of NAC to the cloud eliminates expensive on-site hardware and hidden maintenance costs. With cloud NAC, like Portnox CLEAR, all that’s needed to control network access across a geographically dispersed network is an internet connection.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

醫療保健提供商從Aruba ClearPass轉移到Portnox CLEAR

AbsoluteCare is a fast-growing regional integrated healthcare provider headquartered in Baltimore, Maryland, with facilities up and down the East Coast, including Atlanta, Philadelphia, and Washington, DC. Since 2000, AbsoluteCare has provided medical assessment and treatment to tens of thousands of people through its “wrap-around” care model.

“Several years ago, as the company continued to grow, many of our customers, including companies like Anthem and BlueCross BlueShield said we needed to be HITRUST certified in order to work with them,” said Chris Becker, AbsoluteCare’s National IT Director. As part of that journey towards HITRUST certification, Becker and his team discovered that they would need to implement a network access control (NAC) solution.

“At that time, we looked at HP Aruba ClearPass and Cisco ISE, and decided to go with Aruba,” Becker continued. “We spent quite a bit of money to get it implemented – relying on outside consultants to get it up and running and conduct training – it’s a rather large application. We ultimately used it minimally because much of the functionally was overly complex.”

In general, the company utilizes managed corporate devices across its workforce, specifically Dell laptops running Windows X, as well as a number of iPads and iPhones. “We have a small population of BYOD, but we don’t encourage it – it’s just more work to manage the compliance of those devices with the limited internal IT resources we have,” Becker stated.

Migration Challenges

In the summer of 2020, AbsoluteCare found itself in a bind during a datacenter migration. “We decided to move our Aruba servers from one datacenter to another, and we found out – oh my gosh – this is going to cost us like $30,000 just to move it,” continued Becker. The hidden costs didn’t end with just the migration, however. Becker and his team realized they would have to incur more fees to upgrade ClearPass because the version was nearly three years old.

“We saw dollar signs. Lots of dollar signs. Not only that, but ClearPass really didn’t grow with us – you almost have to be an HP Aruba expert to really make the solution work for you the way you need it to,” Becker recalled.

clearpass nac quote

Headed in a Different Direction

To avoid paying staggering professional services fees for the expertise needed to execute the ClearPass server transfer, Becker and his team opted to go out in search for a new NAC solution that would eliminate these hidden costs and provide a lightweight, flexible option for network access control.

“We definitely wanted cloud. We’re fans of cloud – both private and public,” Becker indicated. “Portnox CLEAR definitely fit the core requirement to act as our NAC solution, but it also offered other benefits through its optional agent that made it the clear winner for us.”

Out With the Old, In With the New

AbsoluteCare was able to swiftly roll out Portnox CLEAR with its AgentP add-on, allowing Becker and his team to leverage the platform’s on-or-off network endpoint risk posture assessment and automatic device remediation capabilities for users on its wired and wireless networks.

“This is one of the things I really liked about Portnox,” said Becker. “When we initially got access to the environment to conduct our proof of concept, we set up our account and then set a meeting for a week out to assess where we were and what we still needed to do. Well, my systems admin basically got everything configured in a few days all on his own.”

portnox clear v. aruba clearpass

For AbsoluteCare, Portnox CLEAR’s ease of use was a major selling point. “I mean, coming off of something like ClearPass, where you basically need to be a systems engineer to figure it out – Portnox CLEAR was just a piece of cake,” Becker reveled…

Want to read the full case study? Download it today.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

企業 WiFi 身份驗證,解釋

Gartner Reviews NAC Tools for 2021

Types of WiFi Authentication

There are several different methods for authenticating wireless clients. Some have fallen out of favor due to security weaknesses, ultimately being replaced with newer, more secure authentication methods. These include :

  • Open authentication to the access point
  • Shared key authentication to the access point
  • EAP authentication to the network
  • MAC address authentication to the network
  • Combining MAC-based, EAP, and open authentication
  • Using CCKM for authenticated clients
  • Using WPA key management

WiFi Authentication Challenges

From its outset, WiFi posed a unique challenge when it came to authenticating identities since users were no longer physically connecting to ethernet ports. Originally, there were several methods used to authenticate users across wireless networks:

  1. Separation: One was to separate the WiFi network and enable it to access the Internet. If you needed to access on-prem applications or resources, you would VPN into the network just as if you were remote. In this case the solution for WiFi authentication was the implementation of the SSID and password which was shared across any users of that particular network. In this case, there wasn’t really a connection to the main network even though the WiFi network was located alongside the internal network. It operated more as a separate network for a variety of reasons.
  2. SSID: Another path is to simply leverage an SSID and passphrase and let anybody on the network that has that. Subsequently the user could authenticate to the directory service, but even if they failed the authentication, they would still have access to the WiFi network.
  3. RADIUS Authentication: Yet, another path was to leverage the RADIUS authentication protocol to auth access to the WiFi network which would subsequently authenticate access with Active Directory. The RADIUS server was the intermediary between the WiFi access point and the core identity provider. RADIUS was able to speak to the WiFi access points and then translate for the directory to authenticate user access. Of course, the downside of this approach was more servers, more integration, and more configuration on end user devices.

WiFi Authentication with Portnox CLEAR

WiFi extends beyond your walls. Employees harmlessly share company WiFi passwords with guests, contractors, business neighbors without ever stopping to think about the network and information security risks this poses to their organization. It’s not just outsiders, however. Today, nearly 20% of SMBs experience a data breach by a former employee who still has WiFi access.

It’s never been easier to secure your WiFi. With Portnox’s WiFi Security-as-a-Service, complex integrations and RADIUS server setups that traditionally required skilled IT staff and extensive training have been eliminated. Now, you can set-up user and device authentication that comply with security regulations in minutes.

Watch How it Works

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

SASE 與網絡訪問控制的未來

Gartner Reviews NAC Tools for 2021

The current enterprise network security practices focus on verifying the identity of the user and the device in a perimeter-less environment, where cloud-hosted technologies prevail in the enterprise and where remote sites include branch offices and employees working from home.

In Gartner’s paper “The Future of Network Security is in the Cloud”, one of the key findings is that “network security architectures that place the enterprise data center at the center of connectivity requirements are an inhibitor to the dynamic access requirements of digital business.” And there is a recommendation for enterprises to move their security into the cloud, based on a networking and security model called Secure SASE, a term coined by Gartner’s leading security analysts.

What is SASE?

SASE, pronounced “sassy”, stands for Secure Access Service Edge. It is a cloud-based network security model and category, proposed by Gartner in 2019, to support agile secure access to enterprise assets. This model includes the network security solutions in a global and cloud-native service that allows IT teams to easily connect and secure all of their organization’s networks and users in an agile, cost-effective, and scalable way. This is especially useful in the currently globally dispersed digital enterprise.

According to Gartner’s analysis, SASE can be characterized as an identity-driven, cloud-native, globally distributed technology that supports and impacts all enterprise edges and IT domains. For example, this would include a branch office in LA along with the main HQ in London, while traveling/mobile team members can connect on the go.

“SASE capabilities are delivered as a service-based upon the identity of the entity, real-time context, enterprise security/compliance policies and continuous assessment of risk/trust throughout the sessions. Identities of entities can be associated with people, groups of people (branch offices), devices, applications, services, IoT systems, or edge computing locations.” (Gartner)

SASE addresses the numerous problems with traditional network security methods, many of which are rooted in the idea that network security architectures should be placed at the center of connectivity in the HQ or data center, where typically branch locations are more vulnerable to attack.

Why should I care? What’s the problem?

Network security legacy applications cannot efficiently support newer networking use cases that have moved to “the edge”, such as cloud applications, dynamic services, and distributed data in remote branch offices. Traditional on-premises architectures introduce challenges such as latency, large management overhead, networking blind spots, and continuous reconfiguration work by the IT team as vendors, services, and equipment change. Even though the SASE model is not without its own challenges, it can eliminate these issues by removing cumbersome technologies and networking complexities, while moving the entire security process to the network edge (The point where the enterprise-owned network connects to a third-party, particularly cloud technologies. Oftentimes, network administrators refer to their “WAN edge” or “internet edge”).

If enterprises try to solve IT challenges as they emerge, with ad-hoc/point solutions, they will be leading themselves into technical compounds that are complex and costly to manage, and that will not necessarily work well with each other in terms of efficiency and speed. Complex and cumbersome communications between IT components slow down IT and its response rate to different business requirements.

SASE can change this paradigm because as mentioned, it is identity-driven, cloud-native, globally distributed, and securely connects all edges (WAN, cloud, mobile, and IoT). With SASE, enterprises can reduce the time it takes to develop new products, deliver them to the market, and respond efficiently and appropriately to the increasing changes in business conditions.

Shift happens.

In the last few years, as more organizations around the world became more decentralized, each office location is considered to be a remote site/ a branch office location, by organizational security controls. Companies either consume access security services in a costly method through data centers, implementing redundant controls in each location, or worse, neglecting the security for that part of the enterprise network altogether.

In simple terms, we are talking about delivering an all-access security suite from the cloud and not from the data center. This is in line with the trend of identity brokers moving to the cloud (such as Azure, G Suite, Okta, and others) as well as the continued migration to the cloud of many other cyber-security architectures and IT services.

In a scenario where you are implementing an on-premises NAC solution that goes with your on-premises network equipment, you can easily identify and authenticate the end-users. However, if your organization is distributed and like many others, has transitioned to using a cloud-delivered ID broker, then continuing to consume authentication and access services from the cloud make much more sense.

In the diagram, on the left side, we can see the price of not leaving any remote site exposed – either you pay a very high price for each location, or you need to duplicate your security mechanisms in each location which is costly. The second option is to authenticate and obtain your access rights and compliance needs via the closest, geo-redundant cloud service available.

OK, so what happens now?

The sensible course of action is to plan a security strategy to be scalable and efficient in the present, while at the same time future-proofing the organization’s security. With the organizational data migrating to the network edge, it makes sense to authenticate and authorize users and devices in a cloud format, thereby assuring that regardless of the equipment and geolocation, employees can securely connect in a cost-efficient and secure method to the needed resources.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。