Skip to content

我們的城堡沒有圍牆! 萬籟俱寂,零信任

Gartner Reviews NAC Tools for 2021

Why today’s boundless company networks are like castles without walls being protected by network security systems stuck in the middle ages.

Today, your network is likely comprised of your LAN, MPLS, SD-WAN, employees’ homes, Azure, Starbucks, Marriott, any airport…you get the idea. Your network extends to wherever authorized devices connect to gain access to company resources.

All of this proprietary, confidential or merely sensitive data being accessed across these parts of the network is no longer safe behind your castle walls. Access to everything (from everywhere) has changed the security dynamic.

new network perimeter

How does zero trust factor in?

Enter zero trust, a new – well, maybe not that new – but let’s say in vogue network security model that is focused to address the challenges posed by today’s increasingly complex and extended corporate networks.

The zero trust model does not require or expect you to have walls around your networks. With zero trust, as the name implies, NOTHING inside or outside a company is trusted. That means no devices or systems used by employees is automatically trusted.

Traditional NAC meet zero trust requirements

Now, this security model may seem familiar. Isn’t this just like network access control (NAC)? Well, yes and no. NAC has been around since the early 2000s, and has been primarily focused on ensuring only valid and authorized devices can access your network. Traditionally, however, NAC solutions have only focused on the LAN, as that was what existed within the castle walls of an organization. But as I’ve stressed, the typical network extends far beyond the LAN today.

To truly achieve zero trust, organizations need a NAC solution that can easily and effectively work when your castle has no walls.

NAC for today’s sprawling networks

Since your employees are likely on the move and using several different devices (desktop, laptop, phone, etc.), any NAC would need to have device awareness no matter where the device is geo-locationally. And that means not only when it is joining the LAN, but also when it is connecting from home, from a remote office, from Starbucks – awareness anywhere and everywhere, always.

Perhaps the most critical factor when assessing your network security needs is having the ability to continuously monitor endpoint risk. After all, you can’t just go around authorizing every company PC to connect if it’s not “trusted.”

Ensuring endpoints are in a company compliant state, minimizing or eliminating the potential for endpoints to be hacked and used to bridge your network is crucial. This requires a NAC that is always aware of endpoint risk and can use that to allow or block access. Today, this mixture give your network the best chance of minimizing such threats.

It’s the control part of NAC that ultimately brings the most added value versus endpoint-only zero trust solutions. The ability to not only allow access to your trusted devices, but also to control that access by placing them on the proper VLAN or under an appropriate access control list (ACL) adds a powerful layer of security.

The answer is in the cloud

Lastly, a NAC for today’s boundless network must be “light weight.” You don’t want to be deploying appliances or software in every remote location, store or office. It takes an immense amount of bandwidth and expertise to properly execute. Can’t that investment be better spent elsewhere?

This is where traditional NAC solutions fall short. Since they were designed for the old castle network model, they simply aren’t equipped to give you the full visibility and control you need over your extended network to prevent breaches.

The answer is NAC delivered as a cloud service. Manageable from anywhere, coverage for everywhere, and with continuous device awareness – a cloud-delivered NAC adhering to the zero trust model can future-proof your increasingly extended network.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

Portnox 獲得 Microsoft 金牌雲平台能力

Portnox demonstrates best-in-class capability and market leadership through demonstrated technology success and customer commitment.


NEW YORK, NY – November 4, 2020 – Portnox, a fully cloud-delivered network access control (NAC) provider, today announced it has attained a Gold Cloud Platform competency, demonstrating a “best-in-class” ability and commitment to meet Microsoft Corp. customers’ evolving needs in today’s mobile-first, cloud-first world and distinguishing itself within Microsoft’s partner ecosystem.

To earn a Microsoft Gold competency, partners must successfully complete exams (resulting in Microsoft Certified Professionals) to prove their level of technology expertise, and then designate these certified professionals uniquely to one Microsoft competency, ensuring a certain level of staffing capacity. They also must submit customer references that demonstrate successful projects, meet a performance (revenue and or consumption/usage) commitment (for most Gold competencies), and pass technology and/or sales assessments.

The cloud-delivered CLEAR NAC platform from Portnox is designed to help partners capitalize on the growing demand for infrastructure and software-as-a-service (SaaS) solutions built on Microsoft Azure. With built-in scalability, no on-site hardware, multitenancy and other benefits, the platform allows Microsoft partners to empower their customers by eliminating the traditional complexities associated with on-premises NAC.

“This Microsoft Gold Cloud Platform competency showcases our expertise in and commitment to today’s technology market and demonstrates our deep knowledge of Microsoft’s products and services,” said Ofer Amitai, CEO at Portnox “We plan to accelerate our customers’ success by serving as technology advisors for their business demands.”

“By achieving a Gold competency, partners have demonstrated the highest, most consistent capability and commitment to the latest Microsoft technology,” said Gavriella Schuster, corporate vice president, One Commercial Partner (OCP) at Microsoft Corp. “These partners have a deep expertise that puts them in the top of our partner ecosystem, and their proficiency will help customers drive innovative solutions.”

Cloud Platform

The Cloud Platform competency is designed for partners to capitalize on the growing demand for infrastructure and software-as-a-service (SaaS) solutions built on Microsoft Azure. Differentiate your company with the Cloud Platform competency, and you will be eligible for Signature Cloud Support, Azure deployment planning services, Azure sponsored credit, direct partner support, eligibility to deploy certain on-premises, internal use software on Microsoft Azure, and access to the cloud platform roadmap.

The Microsoft Partner Network helps partners strengthen their capabilities to showcase leadership in the marketplace on the latest technology, to better serve customers and to easily connect with one of the most active, diverse networks in the world.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

Portnox CLEAR 的 5 個關鍵價值

The problem with most traditional on-premise network access control solutions is their complexity across many fronts, including initial setup, configuration, scalability, and on-going maintenance and upgrades. As a truly cloud-delivered NAC service, Portnox CLEAR delivers SIMPLICITY across all of these critical areas.

VALUE 1: Setup Simplicity

Unlike traditional on-premise solutions that require hardware appliances, software, and other on-premise elements, with Portnox CLEAR, you simply create your dedicated instance in Microsoft Azure using your company email or via SSO (such as Azure AD or GSuite) in a matter of just minutes!

With your dedicated instance of CLEAR created, you simply check the appropriate box(s) to create your RADIUS instance. Dedicated F5 load balancers are spun up as well as auto-scale, so you never have to be concerned with service performance or scalability – it will automatically expand as needed to meet demand.

Portnox CLEAR’s simplicity extends with out-of-box integration and one-click set-up for several common directory services, including:

  • On-premise AD
  • Azure AD
  • G-Suite
  • Okta Universal Directory

SIEM integration is as simple as providing the IP/port, protocol type (TCP, UDP, HTTPS), and data format (JSON/CEF).

VALUE 2: Configuration Simplicity

The complexity of traditional on-premise NAC does not stop at the initial set-up of the local appliance(s), load balancing, RADIUS, and other on-premise components. As shown in the sample policy screenshots below, the complexity of traditional NAC extends to policy configuration that is often layered with multiple and nested interdependencies.

From inception, the focus with CLEAR has been to simplify policy configuration, allowing CLEAR to be fully deployed and operational in a measure of hours/days vs. traditional NAC, which typically can take weeks, or in many cases, months to roll out. Intuitive, easy-to-configure access control, risk, and remediation policies are at the foundation of Portnox CLEAR as reflected in the sample screenshots below.

Risk Policies

Easily configure risk-based access controls for all devices or different groups of devices (i.e. accounting, engineering, etc.), by simply assigning a risk value to each group’s relevant compliance checks.

A simple slide bar easily turns risk values into action (allow, alert, block). It’s that SIMPLE! Unlike traditional NAC that monitors a device risk ONLY when it is on or connected to the network, Portnox CLEAR will monitor risk all the time regardless of if the device is on or off-network.

Remediation Policies

While it is important to continuously be aware of the current risk posture of a device and to be able to use that awareness as part of access control. The ability to proactively take action on the endpoint to help assure a minimum level of compliance is always maintained can be equally important. As with all other policy configurations, setting group-specific remediation policies in CLEAR is as simple as a few clicks.

Unlike traditional NAC that will take remediation actions ONLY if the device is on the network, Portnox CLEAR proactively enforces remediation actions all the time regardless if the device is on or off-network.

VALUE 3: On-Demand Auto-Scale

Delivered as a cloud service, Portnox CLEAR eliminates the need for the capacity planning of on-premise software or appliances. Eliminates the need to expand capacity or upgrade appliances to meet future growth needs. Portnox CLEAR services will automatically expand on-demand to meet any demand spikes and future growth.

Our Azure services are scaling up (and down) automatically based on usage and load. We can automatically control the VM size and the scale-up / down rules.

For the RADIUS component, we use Azure Kubernetes to manage the instances and allow scaling based on demand. We use F5 load balancer to channel the traffic to the right instances and make sure the scaling is transparent to the end-user.

VALUE 4: Ease of Integration

Portnox CLEAR continues to expand native integrations and simplified out-of-band integration through and included restAPI.

Current integrations include:

  • Active Directory
  • Azure AD
  • GSuite
  • MS Intune
  • OKTA
  • Palo Alto
  • SIEM (any/all leading vendors)

Portnox CLEAR also integrates with all leading anti-virus providers to validate and remediate (update) as part of CLEAR compliance and remediation capabilities. Portnox CLEAR also includes a REST-full API over HTTPS that can be used in any programming language that supports REST calls or invoked directly through any HTTPS client such as cURL.

VALUE 5: Zero-Touch Maintenance

As a true SaaS solution, Portnox CLEAR is truly zero-touch!

  • No on-going software updates/patching
  • No management of scheduled downtime
  • No hardware or software end-of-life issues

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

網絡研討會:網絡訪問控制:網絡安全工具庫中的必備功能

In this webinar, co-hosted by Portnox and CyberTEK, we examine how Portnox CLEAR – the first and only cloud-delivered NAC-as-a-Service – is helping organizations gain actionable network visibility and continuous risk monitoring of all endpoints across all access layers – no matter device type or geo-location.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

台灣二版獨家代理Portnox網路存取控管(NAC)解決方案,協助企業內部資安防禦輕鬆佈局

近年來駭客入侵內網的事件頻傳,知名企業重要資料被偷竊的事件不斷時有所聞,故對於防範從企業內部入侵與攻擊的需求,也隨之成為關注的話題。談到企業內部網路防禦,長久以來乙太網路已成為基礎網路的標準,但是同時也因先天上簡單的設計,沒有任何管理或控制連網設備的機制,造成不易管理、無法有效監控上線設備的問題;又隨著BYOD(Bring Your Own Device)各種移動設備的盛行,需求不斷地成長,再加上內網安全與管理需求不斷地增加,NAC (Network Access control)解決方案也隨之產生,而其主要的功能就在於解決設備在連上企業或組織內部網路的第一時間,如何來判斷其是否合法,有無權限進入網路的問題。就好像從旅客國外回國進入海關,海關第一時間就會檢查你是否有合法授權可以入境。

台灣二版多年來深耕資訊科技領域,致力於提供與時俱進的產品及解決方案,結合亞洲區的代理優勢與在地化專業的服務經驗,獨家引進Portnox 的網路存取控管(NAC)解決方案,提供了完整的網路存取控制、可視性、管理和策略合規性,以確保企業於當今複雜的網路環境裡能夠平穩、安全地運行。

Portnox成立於2007年,為網路存取控管(NAC)解決方案,其遍及所有網路層面-乙太網、無線、虛擬、VPN和雲,它可以直接與所有現有的交換機、無線存取控制器、路由器和防火牆進行通訊,進而可以在接入網路的第一時間,就能對設備或使用者進行身份認證並監控企業內部或外部的每個端點,無論是IoT、BYOD或公司託管的設備。由於Portnox的解決方案不需要更改任何設備、代理或現有的基礎架構,且無論規模大小,它都能在所有的環境中快速部署。其尖端的技術可協助企業保護、聯繫和管理任何用戶、任何設備、任何地方的網路所面臨的可能風險,以確保當今複雜的網路能夠平穩,安全地運行。

欲完整了解Portnox網路存取控管(NAC)解決方案,產品連結網址:
https://version-2.com.tw/portnox/
或歡迎電洽台灣二版專業資安團隊(02)7722-6899。

【關於台灣二版 Version 2】

台灣二版(V2) 是立足亞洲的代理商及IT開發者。公司發展及代理各種不同的互聯網、資訊科技、多媒體產品,其中包括資安、網絡、雲端、基礎設施、通訊系統、軟體開發運營、商業應用、多媒體、生產力及消費市場產品。透過公司龐大的網絡、銷售點、分銷商及合作夥伴,台灣二版(V2)提供廣被市場讚賞的產品及服務。台灣二版(V2)的銷售網絡包括台灣、香港、澳門、中國大陸、新加坡、馬來西亞等各亞太地區,客戶來自各行各業,包括全球 1000 大跨國企業、上市公司、公用事業、醫療、金融、教育機構、政府部門、無數成功的中小企及來自亞洲各城市的消費市場客戶。

【關於Portnox】

Portnox提供了易於部署、操作和維護及具安全性、可視性的網路存取控管(NAC)解決方案,該公司的創新成果獲得了”Info Security Products Guide “及”Cyber Defense Magazine”等媒體的肯定,Portnox在美國,歐洲和亞洲皆設有辦事處,協助全球數百家企業解決因互聯世界不斷發展所產生的多元網路挑戰。

網絡身份驗證和 Portnox 清除

Traditionally, enterprises have enabled network authentication via usernames and passwords. As we now know today, this method of network authentication can be easily compromised by bad actors, making it no longer sufficiently secure for enforcing network access control. As a means of elevating and strengthening network authentication, Portnox has introduced several new and powerful certificate authority services within Portnox CLEAR, our cloud-delivered network access control solution.

Types of Network Authentication with Portnox CLEAR

Self-Onboarding (Agent-Based)

When an endpoint enrolls using AgentP, Portnox CLEAR will automatically generate a supplicant certificate for the endpoint. This is true for all supported operating systems (Windows, OSX, Linux, etc.), and for all AgentP enrollment methods.

Self-Onboarding (Agentless)

For those not using AgentP, Portnox CLEAR generates an organizational root certificate upon org creation in the system and adds the root certificate to its list of trusted root certificates.

Simple Certificate Enrollment Protocol (SCEP)

To make certificate issuance easier for our customers, Portnox CLEAR also supports SCEP, the open-source protocol, which issues a one-time password to the user transmitted out-of-band.

Microsoft InTune

Portnox CLEAR customers utilizing our MS InTune integration can use InTune to authenticate devices to the network as an alternative to Portnox’s agent-based or agentless options.

EAP-TLS 802.1X

EAP-TLS is considered by many to be the gold standard when it comes to network authentication. EAP-TLS 802.1X authentication is available with Portnox CLEAR out of the box.

Simple, Secure Certificate Authority Services

With Portnox’s ability to offer companies an easy and secure certificate authority services, each customer can leverage its own certificate authority in the cloud, allowing for simpler, more seamless and secure user onboarding. Once configured, Portnox CLEAR will issue every user an identity certificate for self-enrollment via the portal. Once the user has a certificate, he/she will then be granted password-less authentication.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

網絡研討會:信用合作社如何確保安全的遠程網絡訪問

As the NCUA audits continue to expand, many credit unions struggle with finding an effective solution to meet Domain 3 controls within the ACET framework.

In this webinar, co-hosted by Portnox and Btech, find out how Portnox CLEAR is providing the remote network access control, off-campus endpoint awareness, risk and real-time remediation capabilities that either directly meet or highly contribute to many of the most difficult Domain 3 audit areas and requirements.

As part of this webinar, you will also hear from Utah-based University Federal Credit Union – a Portnox customer utilizing Portnox CLEAR’s zero-trust remote access-as-a-service capabilities.

The webinar will take place on Wednesday, October 14 at 3PM EST.

Michael Marvin

Director of Marketing

Mike leads global cross-channel marketing efforts at Portnox. Over the last ten years, Mike has led marketing and communications teams across a variety of areas in B2B tech, including AdTech and FinTech. He holds a B.A. in English and American Studies from Hobart College.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

掌握遠程訪問安全性的五種方法

Remote Access Security: A New Reality

No matter what industry you’re in, your company has likely been affected by the coronavirus outbreak. In fact, you’re probably reading this from home as we speak. Remote work is a new reality. While many of us will return to the office when it’s deemed safe, many companies have seen first-hand the value and ability of employees to work from home and will look to enhance and expand their remote workforces when things return to normal.

For network security teams, this poses a host of new challenges, particularly given the loss of physical control over those newly at-home corporate devices. But have no fear…we’re here to share the important and often overlooked remote access security best practices to consider as you elevate your remote access visibility and security.

I. A Bridge Too Far

No,we’re not talking about the 1977 WWII film starring Michael Caine and Sean Connery (albeit a great movie). Today, companies use VPN gateways and/or virtual remote desktops to provide their remote employees with access to the corporate network and other internal resources.

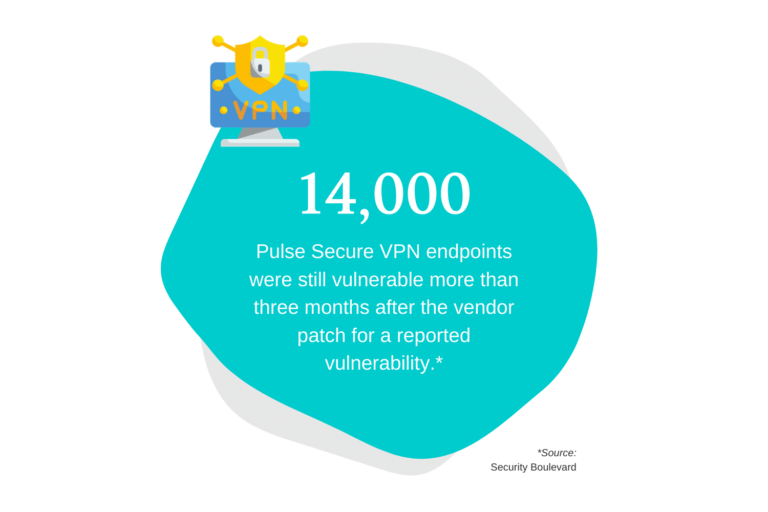
The problem, however, is that some of the most popular VPN vendors have admitted to significant vulnerabilities that would allow any person from the internet with no credentials to use the VPN gateway as the bridge to your corporate network and crown jewels.

II. Are You Afraid of the Dark?

90s kids will get this Nickelodeon reference, although it’s not the show we’re focused on today. We’re all afraid of the dark, and rightly so…scary stuff happens in the dark. That’s why you need to be continuously aware of the risk posture of every remote device connecting to the network continuously – all the time, every time, no matter location or device type. This will allow you to react in real-time to potential threats before $#!% really hits the fan.

Want to unlock the next three remote access security best practices? Download the full eBook today!

Michael Marvin

Director of Marketing

Mike leads global cross-channel marketing efforts at Portnox. Over the last ten years, Mike has led marketing and communications teams across a variety of areas in B2B tech, including AdTech and FinTech. He holds a B.A. in English and American Studies from Hobart College.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

關於NAC (Network Access Control) 網路存取控管解決方案:什麼是802.1X EAP

First Thing’s First

As we’ve written about previously, the standard authentication protocol used on encrypted networks is Extensible Authentication Protocol (EAP), which provides a secure method to send identifying information for network authentication. 802.1x is the standard that is used for passing EAP over wired and wireless Local Area Networks (LAN), as it provides an encrypted EAP tunnel that prevents outside users from intercepting information. The EAP protocol can be configured for credential (EAP-TTLS/PAP and PEAP-MSCHAPv2) and digital certificate (EAP-TLS) authentication and is a highly secure method for protecting the authentication process.

Throughout this article, we will look at how to monitor 802.1X EAP and why doing so is important from a network security perspective.


MAC Authentication Bypass (MAB)

MAB enables port-based access control using the MAC address of the endpoint. A MAB-enabled port can be dynamically enabled or disabled based on the MAC address of the device that connects to it. The below diagram illustrates the default behavior of a MAB-enabled port.


EAP MAC authentication bypass

Session Initiation

From the switch’s perspective, the authentication session begins when the switch detects link-up on a port. The switch will initiate authentication by sending an EAP Request-Identity message to the endpoint. If the switch does not receive a response, the switch will retransmit the request at periodic intervals. If no response is received after the maximum number of retries, the switch will let IEEE 802.1X time out and proceed to MAB.


MAC Address Learning

During the MAC address learning stage, the switch begins MAB by opening the port to accept a single packet from which it will learn the source MAC address of the endpoint. Packets sent before the port has fallen back to MAB (that is, during the IEEE 802.1X timeout phase) are discarded immediately and cannot be used to learn the MAC address.

The switch can use almost any Layer 2 and 3 packets to learn MAC addresses, with the exception of bridging frames such as Link Layer Discovery Protocol (LLDP), Spanning Tree Protocol, and Dynamic Trunking Protocol (DTP). 1

After the switch learns the source MAC address, it discards the packet. Then the switch crafts a RADIUS Access-Request packet. A sample MAB RADIUS Access-Request packet is shown in the snapshot below.


RADIUS Access-Request Packet for MAB

By default, the Access-Request message is a Password Authentication Protocol (PAP) authentication request, The request includes the source MAC address in three attributes: Attribute 1 (Username), Attribute 2 (Password), and Attribute 31 (Calling-Station-Id). Although the MAC address is the same in each attribute, the format of the address differs. This feature is important because different RADIUS servers may use different attributes to validate the MAC address. Some RADIUS servers may look at only Attribute 31 (Calling-Station-Id), while others will actually verify the username and password in Attributes 1 and 2.

Because MAB uses the MAC address as a username and password, you should make sure that the RADIUS server can differentiate MAB requests from other types of requests for network access. This precaution will prevent other clients from attempting to use a MAC address as a valid credential. Cisco switches uniquely identify MAB requests by setting Attribute 6 (Service-Type) to 10 (Call-Check) in a MAB Access-Request message. Therefore, you can use Attribute 6 to filter MAB requests at the RADIUS server.


Session Authorization

If the MAC address is valid, the RADIUS server will return a RADIUS Access-Accept message. This message indicates to the switch that the endpoint should be allowed access to the port. Optionally, the RADIUS server may include dynamic network access policy instructions (for example, a dynamic VLAN or access control list [ACL]) in the Access-Accept message. In the absence of dynamic policy instructions, the switch will simply open the port. No further authentication methods will be tried if MAB succeeds.

If the MAC address is not valid or is not allowed to access the network for policy reasons, the RADIUS server will return a RADIUS Access-Reject message. This message indicates to the switch that the endpoint should not be allowed access to the port based on the MAC address.

If no fallback authentication or authorization methods are configured, the switch will stop the authentication process and the port will remain unauthorized.


Session Accounting

If the switch can successfully apply the authorization policy, the switch can send a RADIUS Accounting-Request message to the RADIUS server with details about the authorized session.


EAP Request Frame

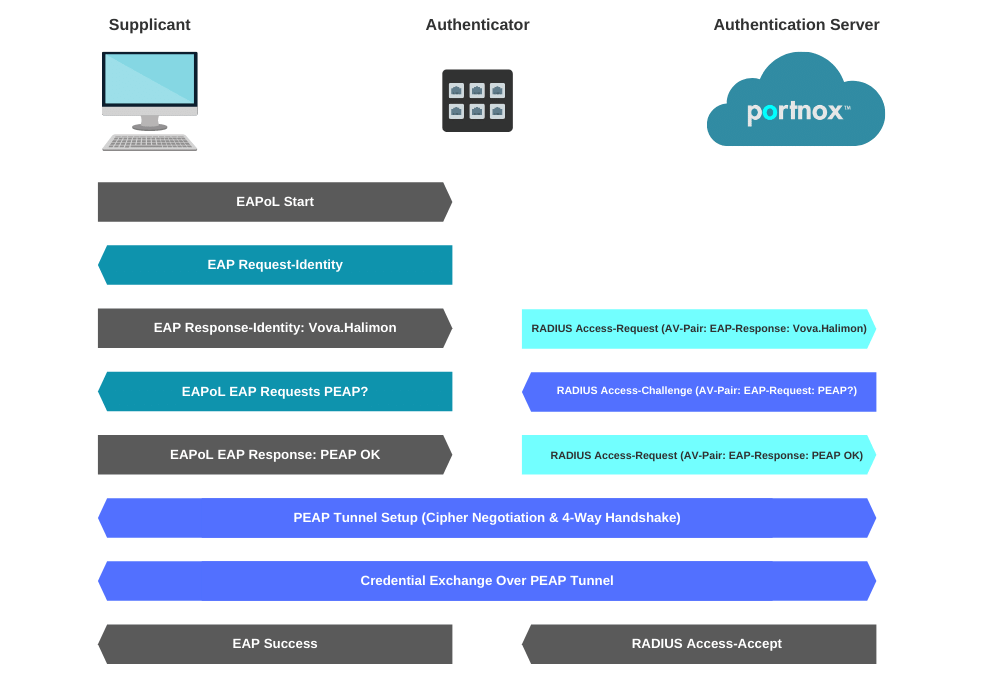
In the diagram above, the first frame sent is an EAPOL-Start frame. This frame is not critical, and the process can be started by the authenticator sending the EAP-Request Frame.

Next, the supplicant responds with an EAP-Response. Messages from the Authenticator to the Radius server use the radius protocol (UDP 1812 for Authentication)When the authenticator receives an Access-Accept packet from the radius server it will authorize the port and allow access to the supplicant. If access is denied by the Radius server an Access-Reject message will be sent to the authenticator and the port will stay unauthorized.

The supplicant can terminate the authentication of the port by sending an EAPOL-logoff frame to the authenticator.


Supplicant to Authenticator (EAPoL)

This is the communication method utilized that provides the Authenticator and the Client a line of communication prior to network access. This is what the capture will look like:


EAPoL communication

The EAPoL portion of communication will vary depending on the authentication type. In my examples, we are using EAP-PEAP w/EAP-MsCHAPv2. This is a fairly standard form of authentication.

The useful portions that can usually be derived from a pcap are:


EAP-Identity Response

In this frame, you can see the Client’s (Supplicant) Identity being used of “Vova.Halimon“. This can be extremely useful when trying to determine if the supplicant is going to authenticate as the user or the machine account as well as what the user could be typing into the username prompt.

For more information on EAP types, visit the IANA EAP registry.

EAP-TLS (Certificate Example)


EAP Auth Method Negotiation and Credential Exchange:


EAP Auth Method

The first message in the above screenshot is the server’s proposal of EAP-PEAP (EAP-TLS, EAP-TTLS EAP-FAST, EAP-LEAP, EAP-MD5) then the client’s response with, “EAP-PEAP good for me” In some situations, depending on the RADIUS server configuration, the client may try to propose a method that is not permitted or supported by the server. This is where you would see that negotiation fail, and ultimately an Access-Reject / EAP-Failure.

EAP Success (Wired & Wireless) & 4-Way Handshake (Wireless):


EAP Success


EAP Code Type
1 Request
2 Response
3 Success
4 Failure

Once the client has been successfully authenticated and authorized, there is an EAP Success message sent back to signify the end of the process. If this is a wired client, the process is over, and the client is able to start transmitting and receiving data frames. If this is a wireless client, the station will utilize a few EAP attributes and the AP will utilize two MPPE (Microsoft Point-to-Point Encryption – key attributes in the RADIUS Access-Accept response to perform the 4-way handshake and create the encryption keys for secure communication.


Extensible Authentication Protocol (EAP) Authentication Types

  • MD5 isn’t typically used as it only does a one-way authentication, and perhaps even more importantly doesn’t support automatic distribution and rotation of WEP keys so does nothing to relieve the administrative burden of manual WEP key maintenance.
  • TLS, while very secure, requires client certificates to be installed on each Wi-Fi workstation. Maintenance of a PKI infrastructure requires additional administrative expertise and time in addition to that of maintaining the WLAN itself.
  • TTLS addresses the certificate issue by tunneling TLS, and thus eliminating the need for a certificate on the client side. Making this an often preferred option. Funk Software* is the primary promoter of TTLS, and there’s a charge for supplicant and authentication server software.
  • LEAP has the longest history, and while previously Cisco proprietary (works with Cisco Wi-Fi adapters only), Cisco has licensed LEAP to a variety of other manufacturers through their Cisco Compatible Extensions program. A strong password policy should be enforced when LEAP is used for authentication.
  • EAP-FAST is now available for enterprises that can’t enforce a strong password policy and don’t want to deploy certificates for authentication.

The more recent PEAP works similarly to EAP-TTLS in that it doesn’t require a certificate on the client side. PEAP is backed by Cisco and Microsoft and is available at no additional cost from Microsoft. If desired to transition from LEAP to PEAP, Cisco’s ACS authentication server will run both.


EAP-TLS Example


EAP-TLS example

However, in this graphic, you can see the client and server negotiate EAP-PEAP. Once that is completed, the server will present the client with its certificate. If the client does not trust the certificate from the server, and the user does not accept the certificate(The end-user might be presented with a dialog to trust this certificate), the exchange will fail after the first frame or two of the handshake.

In this situation, however, the client trusts the server certificate, and the two endpoints secure the medium with a TLS tunnel. Once secured you should notice that the protocol becomes purely TLS and since the traffic is encrypted, we can only see that the frames are “Application Data”. This is the point at which the client and server are exchanging inner authentication data such as EAP-MsCHAPv2 or EAP-TLS.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。