Skip to content

ScottMadden 如何推出與 Azure AD 的安全集成

ScottMaden is a management consulting group that supports Fortune 500 companies. The service provider focuses on two primary business areas: the energy sector and corporate & shared services. With 40-year experience in the industry, ScottMadden provides its clients with strategic planning through implementation across different business fields and functions.

Addressing numerous global clientele challenges represents ScottMadden’s expertise in sophisticated planning. Therefore, how does a company with up to 250 full-time employees throughout the United States and three local East Coast offices face internal security issues? Clinton Miller, IT Director of ScottMadden, shares their story on filling in the missing links in the organization’s cybersecurity strategy.

The Challenge

Securing employees on the go the right way

The company consults domestic and international clients — employees travel quite a bit to client sites and work hands-on on their projects. Hence, a hybrid work model wasn’t the new normal for the organization once the pandemic hit.

ScottMadden consultants spend a lot of time in airports and other public spaces where they would connect to the airport or mobile hotspots and hotel wifi. Yet, the company’s solution wasn’t as good for protecting and running smoothly while traveling.

“The concern was to improve the existing security model and ensure our employees had an encrypted connection regardless of which network they were on.”

Click to tweet

Having better performance, following industry best practices, and fulfilling client requirements to protect data outside the office were the driving factors in looking for a change. But is there a solution that can solve the problem effectively and efficiently onboard?

The Solution

Streamlined client drive-out to different environments

The traveling ScottMadden consultants and employees working from home used to rely on browser-based encryption. Using built-in data encoding in Office365 applications allowed them to perform job tasks and communicate with teams with some security levels.

However, the issue was the poor connection flow while video conferencing — latency is a deal breaker for online business meetings in a remote setup.

“Everyone during the pandemic did a lot of video conferencing via Google Meet, Microsoft Teams, or Zoom. We aimed to ensure there was a minimal impact on video calls.”

Click to tweet

One thing is handling latency to elevate employees’ and clients’ experience. But can the transition process administratively have a minimal impact on existing company infrastructure and cybersecurity strategy?

“One of the things we wanted to do was to push out the client fairly easily, operating on an SSO solution already in use.”

Click to tweet

ScottMadden uses solution Azure AD single sign-on solution for user identification within the organization. The company operates in macOS and Windows environments, so the chosen solution had to fit into the criteria for integration and simplicity.

Why choose NordLayer?

NordLayer solution is compatible with major service providers on the market. Thus, the company could integrate with AzureAD IAM solution and roll out organization-wide onboarding to a new solution using existing SSO.

The endpoint management solution allowed remote access in macOS and Windows environments.

“The implementation of NordLayer went a lot easier when we connected clients to Azure AD. It relieved us from setting up new individual accounts for every 250+ people in the organization.”

Click to tweet

The IT Director handled the process — it didn’t require a lot of resources and time to deploy the solution in the organization.

Organization onboarding using Azure AD by ScottMadden

According to Clinton Miller, the IT Director of the company, the longest step was to create an Azure group and add NordLayer. Once it was solved, the complete rollout to NordLayer solution took only a few hours.

The Outcome

Onboarding to a chosen solution enabled the company to secure team connections and extensive access to functionalities that comply with ScottMadden set benchmarks. Achieving data security didn’t have to compromise connection speed and video conferencing quality.

“Anytime employees are outside the office – at home or coffee shop – wherever they might be, we validated that they can reach all the services they needed, and speed wasn’t an issue.”

Click to tweet

The t
ransition to the new tool was heavily based on the company’s SSO. The documentation, knowledge base, and support team are highly responsive with communication to walk IT leaders through the process.

“For other potential decision-makers: onboarding NordLayer isn’t a heavy lift — you have the support and knowledge base ready, so it’s pretty straightforward.”

Click to tweet

Moreover, NordLayer’s Control Panel provides a good cross-reference point for those using the tool while working outside the office by filtering ongoing active connections.

It also delivers another step in the reporting process for the IT admin and the whole organization. For instance, it verifies that the organization follows internal policies by exporting connection data to verify and justify to a third-party audit.

Pro cybersecurity tips

Different sectors, industries, and services, but the same goal unites every organization’s IT leaders — securing their company assets. Following best practices and professional knowledge helps achieve security targets easier. Clinton Miller, the IT Director at ScottMadden, shares his top-on-the-list tips:

Do you need to upgrade existing tools used in your organization to align with best practices in the industry, improve processes and performance for the team, or expand your capabilities of tracking and reviewing the implemented security strategy?

Using NordLayer, you can integrate more features and functionalities with the organization’s preferred tools, service providers, and IAM solutions. It is possible without committing to massive changes and re-organizing current policies and infrastructure. Reach out to find out about your options on how to secure connections for the off-office employees and improve their experience while working online.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.


檔案類型檔案名稱下載分享
產品資料Atera for MSPs Features List (PDF)
產品資料Atera for IT Departments Features List (PDF)

雲數據:共同責任和備份的重要性

So, who is ultimately responsible for safeguarding cloud-based data? Surprisingly, this simple-sounding question is often overlooked until it’s too late, which is why SaaS customers need to be proactive when it comes to protecting their own data.

Niels van Ingen

Contributed article by Keepit’s own Niels van Ingen

Niels van Ingen, industry veteran and COO at Keepit, shares his perfective on why shared responsibility for cloud data backup and recovery is the only way forward. He says to look at Microsoft’s own documentation, which states, “it’s critical to understand the Shared Responsibility model and which security tasks are handled by the cloud provider and which tasks are handled by you.

For all cloud deployment types, you own your data and identities. You are responsible for protecting the security of your data and identities, on-premises resources, and the cloud components you control (which varies by service type).” 


To dive into the full article on vmblog.com, click here to learn “Why Shared Responsibility for Data Backup and Recovery Is the Only Way.” 

About Keepit
At Keepit, we believe in a digital future where all software is delivered as a service. Keepit’s mission is to protect data in the cloud Keepit is a software company specializing in Cloud-to-Cloud data backup and recovery. Deriving from +20 year experience in building best-in-class data protection and hosting services, Keepit is pioneering the way to secure and protect cloud data at scale.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

國際數據隱私日:為什麼這個日期很重要?

On January 28, we celebrate the International Day for the Protection of Personal Data, or Data Privacy Day. This date leads us to reflect on the importance of laws that safeguard the correct processing of private information in the most diverse countries. Data Privacy Day began with an educational action by the Council of Europe, which began celebrating the date in 2007, and two years later, in 2009, the United States followed. The purpose of Data Privacy Day is to make people aware of best practices for protecting their personal data in the online environment, especially on social media. Nowadays, the day is celebrated in 47 member states of the European Union, the United States, and countries such as Canada, Israel, and Brazil. We prepared this article to address topics related to Data Privacy Day. To facilitate your understanding, we divided our text into the following topics:
  • Data Protection Day: Background
  • How Data Protection Laws Work
  • About GDPR
  • LGPD: Brazilian Data Protection Law
  • How to Protect Personal Data
  • About senhasegura
  • Conclusion
Enjoy the read!

Data Protection Day: Background

In April 2006, the Council of Europe chose January 28 to celebrate Data Protection Day. The date was stipulated in reference to Convention 108, established on January 28, 1981, which addresses the automated processing of personal data. This document was signed by all member states of the Council in the period, to ensure the fundamental right to privacy, including good data processing practices. Currently, it is celebrated to make people aware of its importance, taking into account that, every day, organizations collect and process more information, which needs to be monitored so that the rights of data subjects are not put at risk.

How Data Protection Laws Work

Data protection laws establish personal information protection policies, determining how corporations should treat the data of their customers, employees, and business partners. In practice, it is necessary for individuals, companies, and governmental organizations to apply certain rules related to how they handle this information, such as collection, processing, and storage, to ensure compliance with current legislation. Moreover, companies wishing to conduct business with another country must respect the data protection laws present in both nations.

About GDPR

European standards regulating the use of personal information in electronic environments are contained in the General Data Protection Regulation (GDPR), which requires the responsible use of personal information. Its mass spread is still recent. For this reason, not all countries in Europe have adhered to the GDPR. On the other hand, countries that conduct commercial transactions with European nations should pay attention to the requirements of the Regulation, which addresses criteria such as consent of owners, notification of data breach to authorities, and users’ rights, including:
  • Being notified about the collection and use of their personal information;
  • Requesting a copy and details on how the collection is performed, what data is being collected, and who has access to it;
  • Requiring rectification of incomplete or incorrect data;
  • Demanding that their data be deleted within 30 days;
  • Restricting their personal information;
  • Ensuring the transfer of personal data securely;
  • Opposing the way data is used (except for information used by legal authorities).

LGPD: Brazilian Data Protection Law

The General Data Protection Law (LGPD) is Brazilian legislation that has the function of protecting the personal information of citizens living in Brazil. It details what personal data is and what information should be prioritized when protecting it. According to the LGPD, even companies based outside the country must respect the rules established by the legislation.

How to Protect Personal Data

It is possible to have control over your data through good practices that reinforce its security. Here are some of them:
  • Keep your devices’ software up-to-date to prevent threats that could damage your devices and compromise your personal data;
  • Verify that web pages are reliable before inserting your data, making sure that addresses start with http:// or https:// and that the lock icon or security certificate is present;
  • Avoid exposing personal information on social media such as Facebook, LinkedIn, Instagram, and TikTok, and set up your privacy in posts;
  • Do a general scan to know what data is being shared and, if necessary, disable options;
  • Do not enter sensitive data on public Wi-Fi networks;
  • Use strong passwords. For this, you can combine uppercase, lowercase, numbers, and special characters. It is also important to avoid obvious things like names, phone numbers, and dates of birth.

About senhasegura

We, from senhasegura, are part of MT4 Tecnologia, a group of companies focusing on information security, founded in 2001 and operating in more than 50 countries. Our commitment is to provide digital sovereignty and security to our clients, grant control over privileged actions and information, and prevent data breaches and leaks. For this, we follow the lifecycle of privileged access management through machine automation, before, during, and after accesses. In short, our initiatives aim to:
  • Avoid interruption of companies’ activities, which may impair their performance and profitability;
  • Provide advanced PAM solutions;
  • Automatically audit privileged changes in order to identify privilege abuses;
  • Automatically audit the use of privileges;
  • Reduce cyber threats; and
  • Bring organizations into compliance with audit criteria and standards such as HIPAA, PCI DSS, ISO 27001, and Sarbanes-Oxley.
Conclusion In this article, we have shown the importance of Data Protection Day and laws related to the preservation of personal information, in addition to some measures that can be adopted to protect sensitive data. Was our content relevant to you? Then share it with someone also interested in the topic.

About Segura®
Segura® strive to ensure the sovereignty of companies over actions and privileged information. To this end, we work against data theft through traceability of administrator actions on networks, servers, databases and a multitude of devices. In addition, we pursue compliance with auditing requirements and the most demanding standards, including PCI DSS, Sarbanes-Oxley, ISO 27001 and HIPAA.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

合規專家對 2023 年的期望

The consequences of non-compliance can be devastating.

In 2023, businesses have more to fear than just the formal penalties issued by regulatory or legislative entities. With cybercrime rates at a seemingly all-time high, and even once-trusted cybersecurity companies proving susceptible to breaches, organizations are on high alert.

Failing to comply is more than just a compliance issue or an unchecked box. It can represent an unchecked vulnerability that may give way to a data breach that will have your brand name on consumers’ lips for all the wrong reasons.

That’s why we invited two compliance and security experts to speak on the future and state of compliance. Here’s a short recap of the conversation moderated by Gerald Kasulis, VP of business operations at Nord Security, with:

  • Deena Swatzie, SVP, Cyber Security Strategy and Digital Innovation at Truist,

  • Joy Bryan, GRC/Privacy Technology Analyst, RNSC Technologies, LLC.

Kasulis asked the panelists astute questions about the implications of adopting tech powered by AI, the current corporate climate, and how businesses can prioritize compliance on a shoestring budget.

Watch the webinar recording in full right now or keep reading to find out three takeaways that will help kickstart or support your compliance agenda this year.

Increasingly savvy consumers will hold businesses accountable

When data breaches happen, usually it’s the consumers who suffer. The consequences range in severity and kind, but whether major or minor, reputational or financial, a violation of one’s privacy through personal data exposure is never a welcome outcome.

As businesses become hyperaware of the likelihood of a data breach, consumers are equally tuned in.

quotes

Consumers are getting smarter in that [data privacy] space. They’re going to expect more, they’re going to hold companies accountable. And so that’s why your compliance needs to be in place.

– Joy Bryan

GRC/Privacy Technology Analyst at RNSC Technologies, LLC

Consumers are more likely than ever to want assurances that their personal data will be kept safe as concerns surrounding data privacy become more mainstream. They want to know how their information will be stored and what measures businesses are taking to protect it.

In today’s climate, trust is a linchpin of customer satisfaction. A recent survey revealed that 71% of consumers are unlikely to buy from a company that loses their trust — which is bad news for businesses that have suffered major breaches.

Meeting compliance standards and earning certifications can be a shorthand for establishing (or re-establishing) customers’ confidence: this ensures that businesses are following the agreed-upon best practices in a verifiable way.

At the end of the day, the buck stops with corporations who collect and store personal data. They will be held accountable for their (in)ability to protect the data they keep.

“Consider yourself as the consumer,” says Swatzie. She suggests that businesses should use the golden rule as a framework — treat consumer data as you would hope and expect yours to be treated.

Additional resources may not be the answer

quotes

Even when we talk about talent and the workforce, everyone’s immediate response is ‘we need more resources.’ You don’t always necessarily need more resources.

– Deena Swatzie

SVP, Cyber Security Strategy and Digital Innovation at Truist

Swatzie explained that it’s important to understand what exactly is required to meet compliance standards so that you can balance what you have with what you need. Here, collaboration between teams is key. Security and compliance initiatives will overlap.

Both experts agree that it’s best to start by looking at in-house tech and talent before making an investment. And on the occasion when you do require an additional resource, like software, be sure that you’re adopting tools that serve multiple functions.

quotes

I think that whatever platforms and technologies are implemented should have a collaborative feel — where you’re tackling multiple things at once.

– Joy Bryan

GRC/Privacy Technology Analyst at RNSC Technologies, LLC

NordPass Business, for instance, delivers so much more than password management. Get a powerful data breach scanner, password health metrics, a detailed activity log, company-wide advanced security settings, and multi-factor authentication.

On the topic of breaches, take solace in NordPass’ zero-knowledge architecture which ensures that only you hold the key to your business credentials and vault items. In the unlikely event of a breach at NordPass, your private information will remain encrypted and out of reach to cybercriminals.

New investments in tech solutions should add value to what many teams are likely to prioritize the most: workflow efficiency. Consider how and whether security and compliance tools speak to that need.

Get into the nitty gritty. Take the time to consider your existing and prospective tools’ full scope to avoid overinvesting in overlapping functions.

According to Swatzie, “Privacy is everybody’s responsibility. Security is everybody’s responsibility. Compliance is everyone’s responsibility.” For that reason, it’s important not to take buy-in for granted with a top-down approach.

Ask yourself: will my team be open to adopting this policy or software? Does it promote or detract from their respective top priorities?

The word of the day is “proactive”

If we had to summarize the experts’ advice in just two words: be proactive. Specifically, on the topic of lessons learned from a turbulent 2022:

quotes

I would hope that in terms of lessons learned, it allows businesses to be a little bit more proactive in their approach and in their strategies.

– Joy Bryan

GRC/Privacy Technology Analyst at RNSC Technologies, LLC

If your compliance and security strategy is only reactive, then it shows a lack of forward-thinking, meaning you’re likely to be continuously caught off guard and lagging behind. Swatzie suggests that compliance professionals and business leaders “put on their auditor hat.”

quotes

I’m used to being heavily regulated and audited so I’ve learned enough from the auditors to know exactly what they’re going to ask me before they ask me. So going back to what Joy said earlier, be as proactive as possible.

– Deena Swatzie

SVP, Cyber Security Strategy and Digital Innovation at Truist

Where possible, brace your business for what’s likely to come down the compliance pipeline by studying the standards themselves. With an intimate understanding of the “spirit of the law” you should be able to intuit what’s next and prepare accordingly.

That being said, it’s not a lack of motivation that leaves security and compliance professionals in a reactive position. When it comes to cyber incidents, board and senior leadership members sometimes struggle to see prevention as the cure — waiting until after an event has occurred to implement more stringent security measures.

To learn more about how to get buy-in from colleagues and management before the fact, read our guide on how to campaign internally for cybersecurity.

Summary

Facing increasingly savvy and appropriately demanding consumers, businesses should understand that they will be held accountable for breaches of personal data and plan accordingly.

But, that doesn’t necessarily mean rushing to acquire additional talent and technological resources. Invest wisely and make it count. In particular, security software should be multi-functional.

Finally, the key to success is in forward-thinking. Adopt a proactive strategy to avoid a constant scramble to respond after-the-fact.


About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About Nord Security
The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

NordLayer 功能回顧:DPI Lite

The lines are blurred in the modern business lifestyle. There’re no boundaries between employees working from the office or anywhere in the world. And technological privilege enables linking personal devices to work applications for user and organization convenience.

This flexibility and ability to be mobile also mean that business matters simultaneously mix with personal activities online. And mobility is not alone to blame — the internet is often a necessary tool to perform job tasks and operate in different organization layers. Uncontrolled access to the internet provides vast resources incompatible with the work environment. How to manage what employees can do online without imposing risks on the company?

Deep Packet Inspection (DPI) is one of the most straightforward tools that limit free roaming online while connected to the company network. Establishing a set of restrictions helps create a secure perimeter for online activities within the company network.

It’s an important feature that supports performance and security efforts. Non-work-related activities can distract and reduce productivity. Moreover, entering various websites and apps can lure employees into malicious activities, so DPI is a choice for IT administrators to get a grip on the company’s traffic flow.

DPI solution using NordLayer

NordLayer solution offers a DPI Lite feature that allows IT administrators to control what user-requested data goes through or gets blocked from entering the company’s network.

The DPI Lite technology at NordLayer works on nDPI open-source protocol classification engine. It offers the most popular and acknowledged services  (ports and protocols) that are used by websites and network apps to operate on the internet.

With NordLayer, admins choose specific ports and protocols they want to include in the custom-defined block list. The policy applies only when a user is connected to the organization’s virtual private gateway. Thus, employees who work on job-related projects can’t simultaneously use blocklisted online resources and network applications with restricted access.

How does NordLayer’s DPI Lite feature work?

The cloud-based feature is available only with a virtual private gateway configuration. It’s set to active within 24 hours upon request. IT admins can add or remove specific ports and protocols open to access through the company’s network. They can do it by submitting an inquiry via NordLayer’s Control Panel.

The IT administrators can navigate and choose from a wide range of alphabetically arranged services (no slot restriction) that cover dual-use online resources, potentially harmful to business operations:

  1. Apple services

  2. Domain Name System

  3. E-commerce

  4. Email client protocol/Email services

  5. File sharing

  6. Gaming

  7. Google services

  8. Hypertext Transfer Protocol

  9. Identity

  10. Infrastructure/Networking

  11. IP tunneling protocol

  12. Messaging protocol/services

  13. Microsoft services

  14. Monitoring/SCIM

  15. Music streaming services

  16. News services

  17. Peer-to-peer file sharing

  18. Remote Access

  19. Social media

  20. Software Development

  21. Streaming services

  22. VoIP protocol

  23. VPN services

  24. Other (miscellaneous)

Our internal data shows the tendency to stop services primarily related to unapproved Peer-to-peer file sharing, Social media, and Gaming categories. It comes as no surprise that customers are particularly interested in limiting access to non-work-related services that impose the biggest risks to company assets and staff performance.

Infographic for employee accessHowever, if an employee needs access to company-level blocked sources, for example, a Social Media Manager working on Facebook and LinkedIn, IT administrators can purchase a separate dedicated Virtual Private Gateway for such employees and configure it with fewer restrictions.

The categories expand to a complete list of 250 available ports and protocols. You can choose only certain types of services, like blocking all messaging services except Slack, used for organizational communication.

NordLayer’s DPI Lite feature is managed only by the IT administrator and doesn’t have an ON/OFF function on the user side. The feature operates on the Application layer (OSI model Level 7) and Browser layer (OSI model Level 3). It means DPI inspects incoming data on the web and within network apps.

Enabled DPI Lite runs when the user, connected to the company’s virtual private network (or VPN), sends a request to access online resources or uses network-dependent applications. Once disconnected from the organizational network, the DPI policy isn’t active. Thus, it’s crucial to permit access to internal resources and applications only when they are connected to the network.

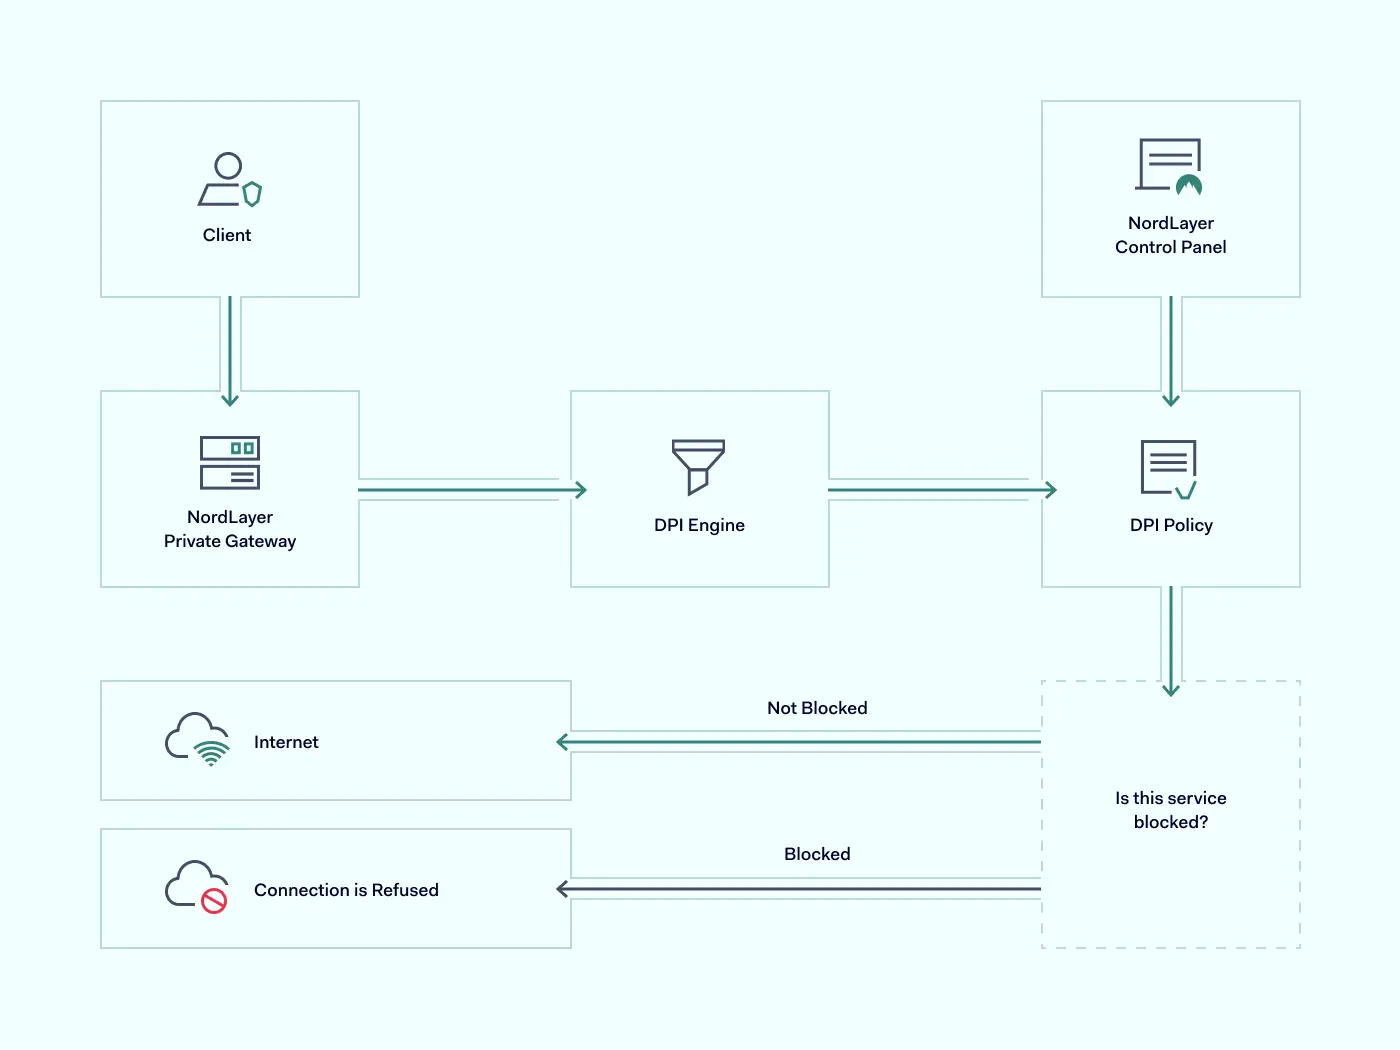
deep packet inspection scheme

The incoming data is screened and filtered using the nDPI engine against the DPI Policy defined by the company’s IT administrator. The user is connected to a requested website if traveling data packets don’t include blocked services.

However, the connection to the requested online resource is restricted if there is a match between the data packet and the DPI block list policy.

How NordLayer’s DPI Lite is different?

Some solutions allow DPI to incorporate extensive categories and be customizable for every client’s preferences to restrict content online. However, a more complex approach may lead to excessive expenses. It may also require challenging configuration and become limiting to the company’s disadvantage.

Extensive data processing defined with all types of possible keywords can disrupt the connection flow and block access to online resources that initially weren’t intended to be restricted. On the other hand, if the company is set for hardware infrastructure and decides to continue with the same type of DPI technology, it will need to know how to configure and perform in-house maintenance. All these additional steps create an unnecessary workload for IT administrators.

To streamline the DPI implementation to the company infrastructure, NordLayer incorporates an easy-to-launch and control DPI Lite feature. It is cloud-native and easy to add or remove without investing in excessive resources. Its activation takes short notice and can be managed centrally, enabling flexibility and focus to the teams and operations:

  • Keep productivity on point. NordLayer’s DPI Lite feature encloses the company network with work-only online resources within employees’ reach. Leave no space for distractions, so teams are less likely to spend time on their personal activities and decrease the chances of human error.

  • Establish security levels. Entering unsecured websites or downloading data to work-linked endpoints can become a freeway for malicious actors accessing internal data and resources. DPI Lite can help filter out hidden remote computer access and control software planted by cybercriminals.

  • Quick implementation and adoption. DPI Lite, like all the other NordLayer features, is entirely cloud-based and thus simple to integrate into existing infrastructure. Besides short enablement time, it is compatible with other data processing features like DNS filtering by category, constructing a more robust organization security posture.

  • Easy to adhere to business needs. The categories or services of DPI Lite are simple to manage. A complete list or a few exceptions can be added or removed from the DPI Policy as required to suit the company’s service scope.

NordLayer offers a packet inspection solution that doesn’t overwhelm network security strategy and focuses on the most common business pain points. A well-sifted service list doesn’t leave space to overthink data to block or spend time researching what online resources to consider, so no openings are left. Overall, DPI Lite helps organizations handle their teams’ efficiency and activity while at work.

Benefits of DPI Lite

Establishing limits for online activity while working is like a reminder to focus on your tasks. But it’s not just about preventing employees from distractions using company gateways.

Adding DPI Lite as an additional security measure fortifies network security and advances business performance in different ways.

Prevent data leaking

Whether intentional or accidental, data leaks are damaging to businesses. DPI Lite adds to security measures by restricting the download of data-leaking apps or the usage of data-sharing and emailing services. Suppose employees try to send files from the company network via Dropbox or Google Drive. In that case, DPI Lite will recognize data packets containing related ports, protocols, and headers and will stop the action from completing the request.

Eliminate traffic overload

Online activities create traffic on network gateways: the more requests, the more overloaded infrastructure, ultimately resulting in performance issues. DPI Lite implementation to the virtual private gateways helps limit created traffic as users cannot access online resources. Online streaming and seeding services or visual-heavy social media increase network usage a few folds. Hence, with DPI blocking, fewer data packets must be inspected and unclog the network. Out of user sight, out of admin mind.

Protect static IP addresses

Unrestricted internet usage could create convenient conditions for employees to hide behind company IP addresses to perform illegal activities. For exampl
e, using torrents on a work network can result in copyright holders initiating blocked IP addresses or even legal prosecution for piracy on the organizational level.

With open internet access, scam attempts have a free pass. If law enforcement authorities identify IP during their investigation of a crime done by your employee from the company’s IP address, it might lead to the company’s liability and even hardware confiscation. Hence, whether the network is managed internally or via a vendor like Internet Service Provider (ISP), deep packet inspection as an additional security measure can help establish internal online activity limits to prevent any illicit acts from happening under the company name.

Entering NordLayer’s DPI Lite

Organization-first mindset while at work or dealing with company-related content can be seen as restricting user activity. Although it’s a strong push toward cybersecurity strategy implementation, preventing possible gaps and openings.

Deep packet inspection is part of the bigger picture when combined with other NordLayer security features like DNS filtering by category, ThreatBlock, and Jailbroken/rooted device detection. Enforcing our remote network access solution into your company infrastructure and activating the DPI Lite feature is a matter of a couple of days or less. Organization administrators need to access NordLayer Control Panel, navigate to Servers or Gateways under the Network tab, and configure it by selecting Deep Packet Inspection (Lite) categories as required.

Utilizing simple and affordable tools like NordLayer’s DPI Lite doesn’t overcomplicate the existing cybersecurity strategy and upgrades team productivity, network performance, and company security for better business performance.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.


檔案類型檔案名稱下載分享
產品資料Atera for MSPs Features List (PDF)
產品資料Atera for IT Departments Features List (PDF)

ESET 發現針對台灣和香港等地區的數個帶有特洛伊木馬之假冒應用程式

<新聞摘要>

  • ESET 研究人員發現一個針對東南亞和東亞地區的惡意軟體
  • 手法為駭客將假冒網站放置在 Google 搜索結果的「廣告」位置;ESET同時通報Google ,而這些廣告也已被立即刪除
  • 從這個網站下載的安裝程式大多是中文版本,且部分沒有在中國地區提供下載
  • 受害地區主要集中在東南亞和東亞(馬來西亞、日本、菲律賓、泰國、新加坡、印尼、緬甸、中國大陸、香港和台灣)
  • 此次散播的惡意軟體為 FatalRAT,是一種遠端存取木馬,可以在受害者的裝置上執行各種惡意行為

2023 年 2 月 – 國際ESET 資安大廠研究人員發現了一個針對東南亞和東亞地區的惡意軟體,其透過Google 搜索結果之廣告,進而誘導用戶下載帶有木馬的安裝程式。駭客製作了與 Firefox、WhatsApp、Signal、Skype 和 Telegram 等流行應用程式相似的假冒網站,散播名為 FatalRAT 的惡意軟體,它是一種遠端存取木馬,讓駭客可以控制受害者的裝置,此次攻擊主要影響中國大陸、香港和台灣等地區的用戶。

FatalRAT 可以在受害者的裝置上執行各種惡意行為,包括記錄按键點擊、竊取或刪除某些瀏覽器儲存的數據,以及下載和執行文件。ESET 研究人員是在 2022 年 8 月至 2023 年 1 月期間偵測到此次的攻擊,但根據觀察,此波攻擊應是從 2022 年 5 月就開始了。

駭客註冊了各種域名,這些域名都指向同一個 IP 地址,由一個伺服器託管多個下載木馬軟體的網站,而假冒網站看起來與正版網站一樣,駭客更將這些網站翻譯成中文,提供原本在中國地區未能下載的軟體,例如 Telegram;根據一家中文新聞網站報導,他們在使用 Firefox 瀏覽器時,會看到一則指向這些惡意網站的 Google 廣告,而駭客的手法就是將假冒網站放置在 Google 搜索結果的「廣告」位置。ESET同時通報Google ,這些廣告也已被立即刪除。

ESET 研究人員進而說明 :「雖然已經無法重現此類搜索結果,但判斷這些廣告只提供給目標地區的用戶。由於攻擊者為其網站註冊的許多域名與合法域非常相似,駭客應是依靠 URL 誘使並吸引潛在受害者造訪他們的網站,駭客於竊取網路憑據等資訊後,就可以在暗網販售獲利,或進行其他類型的犯罪行為。ESET資安專家提醒,在下載軟體之前,檢查正在瀏覽的 URL 之合法性是很重要的。

以下為ESET 在 2022 年 8 月至 2023 年 1 月期間偵測到被攻擊的國家 / 地區

關於ESET
ESET成立於1992年,是一家面向企業與個人用戶的全球性的電腦安全軟體提供商,其 獲獎產品——NOD32防病毒軟體系統,能夠針對各種已知或未知病毒、間諜軟體 (spyware)、rootkits和其他惡意軟體為電腦系統提供實時保護。ESET NOD32佔用 系統資源最少,偵測速度最快,可以提供最有效的保護,並且比其他任何防病毒產品獲 得了更多的Virus Bulletin 100%獎項。ESET連續五年被評為“德勤高科技快速成長500 強”(Deloitte’s Technology Fast 500)公司,擁有廣泛的合作夥伴網絡,包括佳 能、戴爾、微軟等國際知名公司,在布拉迪斯拉發(斯洛伐克)、布里斯托爾(英國 )、布宜諾斯艾利斯(阿根廷)、布拉格(捷克)、聖地亞哥(美國)等地均設有辦事 處,代理機構覆蓋全球超過100個國家。

關於 Version 2 Digital
資安解決方案 專業代理商與領導者
台灣二版 ( Version 2 ) 是亞洲其中一間最有活力的 IT 公司,多年來深耕資訊科技領域,致力於提供與時俱進的資安解決方案 ( 如EDR、NDR、漏洞管理 ),工具型產品 ( 如遠端控制、網頁過濾 ) 及資安威脅偵測應 變服務服務 ( MDR ) 等,透過龐大銷售點、經銷商及合作伙伴,提供廣被市場讚賞的產品及客製化、在地化的專業服務。

台灣二版 ( Version 2 ) 的銷售範圍包括台灣、香港、中國內地、新加坡、澳門等地區,客戶涵 蓋各產業,包括全球 1000 大跨國企業、上市公司、公用機構、政府部門、無數成功的中小企業及來自亞 洲各城市的消費市場客戶。

Azure 安全最佳實踐

Microsoft Azure is a dominant cloud hosting platform, serving around 70 percent of organizations worldwide. A popular hosting environment for SQL databases, Azure also provides a flexible way to run up to 200 cloud applications.

This flexibility is a game-changer for many businesses. But there’s a catch. To function properly, it’s essential to create a secure Azure environment. Otherwise, cloud apps and databases can leak sensitive data. Credentials may be at risk, and companies can suffer huge compliance penalties.

Fortunately, solutions exist. This blog will explain how to secure your cloud environment with Azure security best practices. And we will look at how to create a layered security strategy that goes beyond Microsoft’s controls.

Why is securing access to Azure so important?

Azure security matters because Microsoft’s cloud platform hosts a range of critical assets. Companies use Azure to host .Net apps for web applications or gaming DevOps. Azure storage accounts host SQL databases containing client data, while Kubernetes clusters support private cloud infrastructure.

Whatever Azure services companies rely on, security is a priority. Insecure Azure apps can leak data and provide an entry point for cyber attackers. And you cannot rely on Microsoft to cover every security challenge.

Azure clients have wide areas of responsibility to secure their cloud configuration. Clients need to restrict access to sensitive data. Users must manage access and exclude malicious actors. They also have to manage how data flows between cloud apps. The need for an Azure security policy is obvious when you put these tasks together.

Microsoft Azure security best practices

Any companies that rely on Microsoft’s cloud services should get to know Azure security best practices.

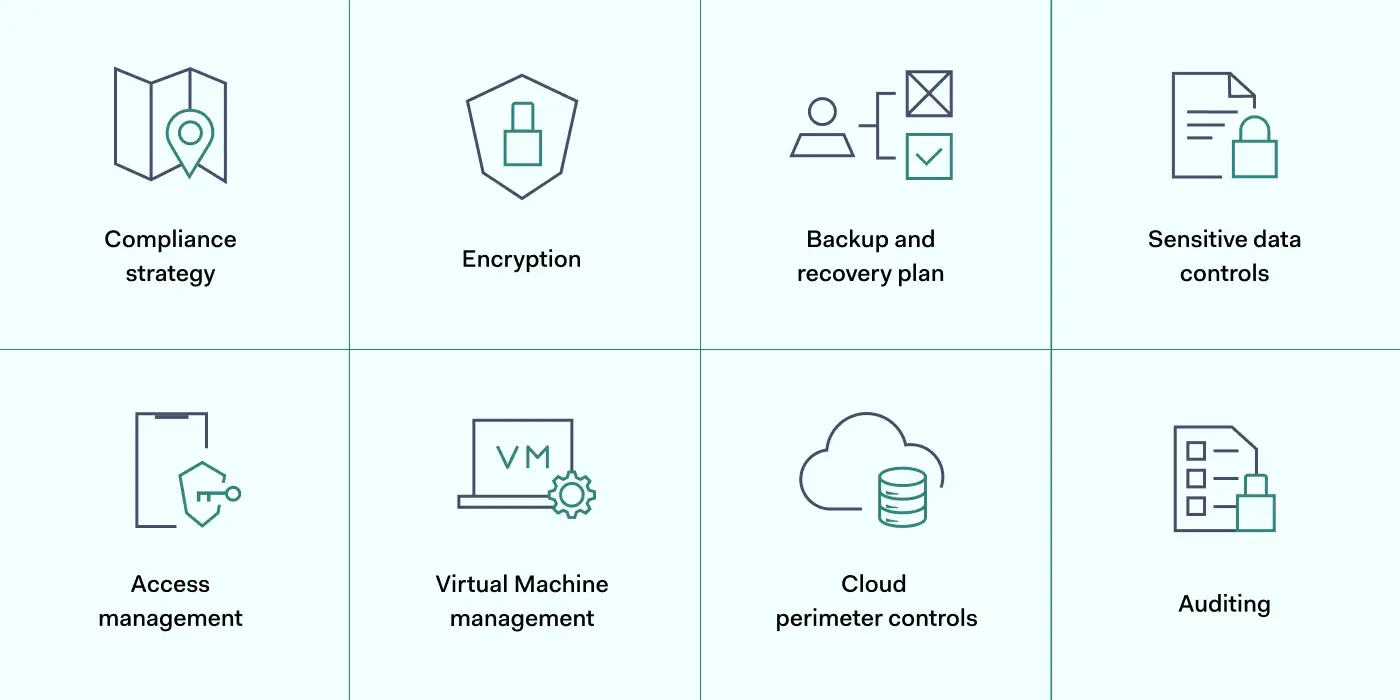
The best approach is adopting a layered strategy. Users should exploit security tools provided by Microsoft. But they should add additional security controls where necessary. These Azure security best practices will explain how the layered security approach works.

1. Map Azure assets and create a compliance strategy

The first step in layering Azure security is understanding the cloud environment. Before applying any of the best practices below, you must understand what assets need to be protected.

Map the cloud assets on your Azure platform. Include all apps and data stores, and classify data according to importance. You should know exactly where client data is stored and who has access to that data.

It is also advisable to create a clear compliance strategy for Azure environments. Define your core goals, including HIPAA, DCI-PSS, or GDPR compliance. Use these data security frameworks as a baseline to improve Azure security and meet regulatory requirements.

Track your compliance progress with the scoring tools in the Azure Security Center. The compliance dashboard provides detailed information about security levels and required actions.

2. Encrypt critical data

Data security on Azure apps is the responsibility of clients, not Microsoft. So take action to encrypt data and hide it from malicious actors.

Encrypt sensitive data at rest using Microsoft’s server-side symmetric key encryption tools. You can use these tools to segment data by importance. This ensures that operational data is available to employees. But financial or personal information is only accessible to users with specific encryption keys.

Azure Disk Encryption works alongside Microsoft’s SSE. It creates another layer of data security for virtual machines and data containers. This reduces the risk of attackers exploiting Virtual Hard Disk (VHD) files. Attackers will find it much harder to create virtual machines within Azure environments.

When you apply Azure encryption, key storage is your responsibility. Secure encryption keys in IAM controls in place to prevent unauthorized access. The Azure Key Vault is a good key management solution and integrates well with Azure app environments.

Users should also encrypt sensitive data in transit. Data constantly flows between Azure apps, remote devices, and on-premises workstations. VPN encryption provides a solution, adding another layer of protection above Azure security controls.

3. Create a backup and disaster recovery plan

A strong Azure security posture features a fall-back plan when systems fail, or attackers succeed. Microsoft offers an end-to-end DR service via Azure Site Recovery (ASR). Combine this with Azure Backup to create tailored data backup plans.

With an ASR failover plan, you can recover application states with minimal information loss. You might also add Azure Storage Replication, which regularly generates multiple copies of important files.

4. Secure sensitive data with robust controls

Encryption is not the only data security control for Azure users. Consider a range of additional tools and find a mix that secures sensitive data without compromising user experience. Options to think about include:

  • Activate auditing tools. Users can instruct Azure to audit databases. This creates a data stream that tracks database changes. Data visibility makes it easier for security teams to detect anomalies and unsafe user activity.
  • Add Azure SQL threat detection. Many Azure apps rely on SQL, but SQL presents critical security threats. Using SQL databases, turn on SQL threat detection to isolate security weaknesses and secure the threat surface.
  • Use Azure Firewall. Azure Firewall adds another layer of data security protection for Azure-hosted apps. You can manage firewall settings centrally, and coverage can increase as new apps come online. Cloud-native TLS inspection provides valuable protection against malware attacks.
  • Enable Azure Monitor alerts. Gain additional awareness by engaging Azure Monitor alerts. Users can target alerts at single resources and use many metrics to identify vulnerabilities. Azure Monitor Action Groups make it easy to automate alerts and deliver precise information when threats arise.
  • Implement Azure Defender. Defender is a subscription-based security service that leverages extended threat detection and response (XDR) and contextual security. It covers hybrid and multi-cloud environments, delivering threat protection and remediation advice. Azure Defender may well be a sensible addition when securing complex cloud environments,
  • Use Shared Access Signatures. Created via Active Directory, Shared Access Signatures let you manage access to Azure resources to third parties and employees for limited periods. Best practices include creating a SAS for all short-term network users, as it allows admins to set granular controls.

5. Manage access with IAM

Preventing illegitimate access to cloud infrastructure is one of the most important Azure security best practices. The best way to manage user access is by adding Identity and Access Management (IAM) to your security arsenal.

Microsoft provides a cloud-native IAM system called Azure Active Directory (AAD). AAD authenticates logins and compares user credentials to a secure Active Directory database.

IAM best practices for Azure include using AAD to set role-based access controls (RBAC). With RBAC, admins can put the Zero Trust ‘principle of least privilege’ into action. Every user has very limited privileges. Privileges only apply after users supply multiple credentials.

Role-based privileges have big practical benefits. Developers will not retain access to resources when their project involvement ends. Attackers obtaining their credentials will be relatively powerless. They will struggle to achieve Virtual Machine access. Breaching Azure SQL databases will be much harder.

Add another layer to your security posture by combining AAD with Single-Sign-On (SSO). SSO combines all cloud and on-premises assets. Remote workers can log in to the apps they need via a single sign-on portal.

Users can apply Multi-Factor Authentication (MFA) at this stage. This requests an extra authentication factor for each login, such as biometric data or one-time codes delivered to smartphones.

IP allowlisting also features in recommended Azure security best practices. Allowlisting lets you specify trusted IP addresses. You can add remote work devices or employee smartphones and exclude every other device until it passes MFA and IAM controls.

6. Add workload and VM protection

Azure security best practices include securing virtual machines via specialist controls. For instance, Azure includes the option of applying just-in-time controls for VMs. These Azure security controls allow users to access VMs for limited periods, removing the possibility of accessing assets after sessions expire.

VM controls also allow administrators to lock vulnerable ports and limit access to authorized users. Restrict access to RDP, WinRM, and SSH ports commonly used by VMs. Access should only be available when absolutely required.

You can apply controls easily by assigning workloads and VMs to Network Security Groups (NSGs). These groups define security procedures for each asset and add another protective layer via the Azure Firewall.

Additionally, remember to keep workload patches up to date. Unpatched Azure apps can be vulnerable to exploits. Automate software updates where possible and audit unpatched tools to minimize your exploit vulnerability.

7. Control the cloud perimeter with network security

Internal Azure cloud security works alongside general network security. Attackers can steal credentials from devices outside the cloud or launch attacks via internet-facing endpoints. This is why Azure’s best practices include measures to harden on-premises security. These measures can protect the whole network perimeter:

  • Track internet-facing cloud endpoints and minimize the contact between the wider web and company resources.
  • Use a Security Information and Event Management solution. SIEM tracks network traffic and identifies potential threats. Integrate it with Azure Defender to cover external and cloud-based vulnerabilities.
  • Apply network segmentation. Separate cloud endpoints from data centers and workstations with internet access.
  • Install a VPN or similar security tool to encrypt data and conceal user identities.

8. Audit user identities and access policies

Your Azure cloud security posture can weaken over time. What works now may degrade and create new vulnerabilities.

Azure security teams must audit every cloud security control and ensure continuing app and data protection. Audit app ownership regularly to ensure only active users have administrative privileges. Clean up Azure platforms by removing obsolete services, groups, and users.

Use the Azure Security Center to improve auditing procedures. The ASC includes machine learning analysis tools that provide feedback and suggest security posture improvements. Real-time monitoring and audit logs provide evidence to fine-tune your security setup.

How can NordLayer secure your access to Microsoft Azure?

Microsoft Azure cloud security requires a layered mix of internal cloud-based controls and solid external security. Users must protect data at the app level, followed by workgroups, platforms, and the entire company network.

The best practices listed above provide a roadmap to achieve security at the cloud level. Encrypt data and manage Active Directory identities. Leverage the Security Center to track user activity and run regular audits. And target virtual machines and apps with specific protection.

But that’s not enough. Add an extra security layer for rock-solid SaaS access control by safeguarding the network edge and protecting credentials outside the cloud.

NordLayer will help you achieve this. Encrypt in-transit data, apply for SSO, and screen access with IP allowlisting. Limit access to trusted IP addresses and exclude everything else – an important step towards a Zero Trust security posture.

Prevent data leaks by blending NordLayer’s network security tools with Microsoft Azure’s internal controls. To find out more, get in touch with our team today.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.


您如何為您的公司選擇最佳的網絡安全項目?

The IBM Cost of a Data Breach 2022 report brought a lot of information that shows the importance of choosing a good cybersecurity project for your organization.

According to information extracted from this document which included interviews with more than 3,600 people working in companies that had their data violated, it was possible to find alarming conclusions.

First, 83% of the organizations surveyed suffered some kind of breach between March 2021 and March 2022. Also, 60% of these attacks increased prices for customers.

It has also been identified that 79% of critical infrastructure organizations have not implemented a zero-trust plan to prevent cyber threats, and 19% of violations occur due to a compromised business partner.

Faced with so many digital security gaps, it can be difficult to know where to start deploying a cybersecurity project. Therefore, we address this issue here. To facilitate your reading, we divided our text into topics. These are:

  • About Cybersecurity
  • Importance of Cybersecurity
  • Cybersecurity Project: What Is It, and What Is Its Importance?
  • What Are the Five Types of Cybersecurity?
  • People, Processes, and Technologies: Crucial Elements for the Success of Every Cybersecurity Project
  • Guidelines for Prioritizing Cybersecurity Projects within a Company
  • Key Cyber Threats Faced by Companies
  • About senhasegura
  • Conclusion

Enjoy the read!

About Cybersecurity

When we talk about cybersecurity, we refer to a set of technologies, procedures, and methods used to prevent attacks on devices, programs, data, and networks, avoiding the activity of hackers and ensuring the privacy of a company’s data, which must be protected from insider and external threats and natural disasters.

However, accelerated by the Covid-19 pandemic, digital transformation has brought several vulnerabilities, such as those related to remote work. As a result, there was a significant increase in data leaks, phishing emails, and account invasions.

Importance of Cybersecurity

Currently, processes in companies are migrating to the online world due to digital transformation, which can “facilitate” the loss of information of great importance to a business.

Thus, organizations need to invest in cybersecurity in order to ensure their operations and prevent threats, such as malware, viruses, and phishing.

One should also be aware that malicious attackers have been improving their techniques over time, so it is increasingly challenging to maintain data security and avoid compromised business.

Another novelty is data protection laws, which have been holding organizations accountable for the exposure of sensitive information from their customers, employees, and business partners, generating million-dollar sanctions.

In practice, these legislations have several requirements to be respected in order to avoid accidental or intentional data loss.

That is, investing in a good cybersecurity project is the recommended measure to avoid inconvenience, financial losses, loss of credibility, and closure of companies.

Cybersecurity Project: What Is It, and What Is Its Importance?

Cybersecurity projects are aimed at promoting digital security within any company. Its importance lies in the possibility of avoiding cyber threats, such as hacker invasions. It also contributes to the fact that errors -whether deliberate or not, of employees or third parties – have fewer impacts on the organization and reduce the possibility of losses, such as: loss of data, credibility, millionaire sanctions imposed by data protection laws, which can even cause the end of a business. And in small companies, this is even more crucial: according to a Cisco study, 60% of organizations affected by a cyberattack shut down operations within 6 months of the incident.

What Are the Five Types of Cybersecurity?

There are five types of cybersecurity. These are:

  • Critical Infrastructure Security;
  • Application Security;
  • Network Security;
  • Cloud Security; and
  • Internet of Things (IoT) Security.

Check out each of them in detail below:

Critical Infrastructure Security

What Is It?
When talking about critical infrastructure security, we refer to the area that contemplates the security of systems, networks, and assets in industries that are essential to ensure the security of a country’s economy, health, and public services. These sectors include the chemical, communications, utilities, energy, and financial industries.

What Are the Challenges?
A major challenge for critical infrastructure is the security issues its systems present versus the limited protection features.

Application Security

What Is It?
Application security is essential as these programs have increasingly become targets for hackers. It consists of practices adopted to make them more secure, which occurs during their development and then after their implementation.

What Are the Challenges?
Ensuring application security requires tracking all the tools developed for these applications. It is also important to be aware of the future needs of a company, which may require software aimed at a more complex infrastructure.

Network Security

What Is It?
Network security is a term that refers to hardware and software solutions, as well as procedures aimed at protecting the network and data against cyberattacks. In practice, this concept includes network analysis, application security, access control, and antivirus software, among other factors.

What Are the Challenges?
The main challenge of network security is to maintain protection in increasingly complex structures, with a large volume of cyber threats and several functionalities used in corporations, which also represent new problems.

Cloud Security

What Is It?
As companies suffer the impact of digital transformation, they become more dependent on cloud solutions and need to adopt measures that ensure digital security in this context.

This is because outsourced providers may even be responsible for infrastructure management, but the accountability for any exposed data remains with the organization as well.

What Are the Challenges?
The challenges of companies adopting cloud solutions are related to the ability to meet security criteria in a dynamic environment, which can generate a lack of visibility in accessing and using data.

Internet of Things (IoT) Security

What Is It?
Internet of things security is associated with protecting devices connected directly to the cloud in gadgets, such as surveillance cameras. Its function is to protect designed devices, without taking into account aspects of cybersecurity and data protection.

What Are the Challenges?
The greatest challenge associated with the internet of things security refers to human activity. In practice, with the increased connectivity of these devices, it is necessary to instruct users on the change of default passwords and the need for updates, for example.

On the other hand, many users do not see these devices as targets of attacks and end up ignoring best security practices during their development and use.

People, Processes, and Technologies: Crucial Elements for the Success of Every Cybersecurity Project

An efficient cybersecurity project does not only involve the five types of digital security covered in the previous topic. It is also important to take other essential elements into account. They are: people, processes, and technology.

Here’s what you need to know about these aspects:

People

When it comes to cybersecurity projects, investing in cutting-edge technology is not enough. It is essential to train users to respect security protocols and ensur
e the protection of company data.

In practice, your employees increase security risks in a variety of ways.
Among them, we can highlight:

Clicking on URLs and Opening Suspicious Emails

It is necessary to make your employees aware of the risks involved in this practice and encourage the exclusion of emails from fake addresses to protect sensitive data.

Keeping the Same Password for a Long Period

To ensure the security of your company, employees’ passwords must be changed regularly. In addition, strong combinations should be used, and it is not recommended to reuse the same password in different services.

Due to the difficulty in memorizing so many passwords, we also recommend the use of a password vault, which will only require the memorization of a single code.

Personal Browsing

Many people use the devices of their companies for personal purposes, such as accessing social media, shopping, or paying bills. The big problem is that this behavior facilitates the work of malicious agents who want to collect information. Therefore, ask your employees to use their own devices, not corporate ones, for personal browsing.

Lack of Backups

Many people still fail to perform backups when finishing their tasks. Nevertheless, it is of paramount importance to back up the system files. So, employees should understand they need the help of the IT team with these functions.

Unattended Devices

Leaving devices on desks unattended and without blocking them is a fairly common practice, which can also cause damage to the security of a company. For this reason, it is essential to make employees aware of the importance of preserving data contained in these devices and maintaining their control.

Processes

Information security professionals use numerous processes to protect sensitive data. In practice, they need to identify and combat cyber threats, protecting information and responding to incidents.
Besides being implemented, these processes must be documented to save time and financial resources, and preserve customer confidence in cases of cyberattacks.

To counter cybersecurity-related risks, we recommend using the Cybersecurity Framework, developed by the National Institute of Standards and Technology (NIST) of the U.S. Department of Commerce, after former U.S. President Barack Obama signed an executive order in 2014.

Technology

After the deployment of security processes, it is indispensable to assess the tools available to avoid cyber threats.

For this, you must consider two types of technology: those that will help you prevent and combat attacks, such as antivirus, DNS filtering, and malware protection; and those that need protection, including computers, routers, and the cloud.

Previously, we could rely on security perimeters. Now, migration to cloud environments, remote work, and policies like Bring Your Own Device (BYOD) have made it easier for hackers to work.

Guidelines for Prioritizing Cybersecurity Projects within a Company

A cybersecurity project is essential to not overwhelm IT staff with unnecessary work and to ensure the company’s ability to deal with a cyberattack.

However, to create and run your cybersecurity project, you must take some action. They are as follows:

Understanding Your Company’s Goals

Each organization has its strategic goals, which should guide the creation of the cybersecurity project. Therefore, it is important to evaluate the company’s vision and its business and cybersecurity strategies.

This information will provide a basis for the development of the project and will be a guide to gradually know if it is, in fact, efficient.

To understand the strategic goals of the company, read documents related to the subject and talk to top management to know their priorities.

Discovering the Reason Behind the Project

Cybersecurity projects can be motivated by several reasons, although all of them need to prevent and combat cyber incidents in common.

In practice, the project can be an awareness and training campaign on cybersecurity, the implementation or updating of a security system, compliance with new laws and regulations, etc.

Understanding what the project’s motivation is will certainly contribute to establishing priorities, directly impacting the company’s operations.

Determining the Value of the Project

Here, when we talk about value, we are referring to the importance of a cybersecurity project for an organization. That is, it is convenient to analyze how it will impact stakeholders and what its real importance is to the business. A project that adds great value must necessarily be prioritized.

Analyzing the Urgency

It is important to assess the urgency of the cybersecurity project to determine whether it should be prioritized or can wait. But remember that priorities can and should be modified as changes occur.

Detailing the Aspects that Affect the Project’s Success

A successful cybersecurity project depends on a number of factors, including budgets, deadlines, and return on investment (ROI), among other things.

On the other hand, it is often impossible to execute a project due to unfavorable circumstances. Therefore, it is advisable to know what can affect the project’s success in advance.

Ranking the Cybersecurity Project According to the Priority

With the information on goals, objectives, and possibilities of success in hand, it is time to establish an order of priorities through an overall classification, which can be score-based.

Defining How Many Projects Can Be Executed at a Time

Probably, the organization will not be able to assume all priority projects at once. Thus, the solution is to work on them in a phased manner, creating a queue of plans to execute.

Another recommendation is to run the fastest ones first and then the ones that require more time and effort.

Sharing Findings with Top Management

Before starting the cybersecurity project, it is essential to meet with leaders and share the information gathered. This is because the findings can serve as insights to change the order of priorities of the projects, requiring top management to be on board.

Working Flexibly

Working with cybersecurity projects requires flexibility, after all, priorities can be modified according to context. By the way, this occurred in most companies after the beginning of Covid-19, which accelerated the mass adoption of remote work and brought new demands to security teams.

Key Cyber Threats Faced by Companies

The following are the main cyber threats that should be considered by a cybersecurity project:

  • Ransomware;
  • Phishing;
  • Attacks on Mobile Devices;
  • Attacks Using QR Codes;
  • Denial-of-Service (DDoS) Attacks; and
  • LotL and AVT Attacks.

See the detailed explanation of each of them below:

Ransomware

This type of cybercrime works like this: the attacker blocks a network or system and asks for millionaire amounts in exchange for the release of information, which may not be returned, but sold to other criminals. Due to the lack of efficient cybersecurity mechanisms in companies, this tactic is very common.

Phishing

Another common crime in the virtual environment is phishing, which consists of sending counterfeit emails, and pretending to be a legitimate organization. With this, malicious agents convince their victims to share personal information or take action to their benefit.

There are also some types of very sophisticated phishing attacks, such as very realistic audio recordings produced through artificial intelligence.

Attacks on Mobile Devices

With many people working remotely, the use of personal devices for corporate purposes and the use of corporate devices for personal purposes tend to occur more frequently.
This increases security vulnerabilities, especially in the face of malware
attacks on devices.

Attacks Using QR Codes

Currently, cybercriminals use QR Codes to deploy malware applications, infecting their victims’ phones and stealing their bank details.
For this reason, it is advisable to check the code provided by the company before accessing it.

Denial-of-Service (DDoS) Attacks

This type of attack occurs when the hacker overloads a machine with traffic, disrupting its normal operation and making a service unavailable to users. In practice, the attack is performed through a single computer.

LotL and AVT Attacks

Less known, Living off the Land (LotL) attacks do not need to create malicious files to access a company’s systems because they use gateways that already exist.
Advanced Volatile Threat (AVT) attacks allow access to an organization’s data as quickly as possible.

About senhasegura

We, from senhasegura, are part of MT4 Tecnologia, a group of companies specializing in digital security, founded in 2001 and operating in more than 50 countries.

Our main objective is to ensure digital sovereignty and security for our clients, granting control over privileged actions and data and avoiding theft and leaks of information.

For this, we follow the lifecycle of privileged access management through machine automation, before, during, and after accesses.

These are also our commitments:

  • Avoid interruptions in the activities of companies, which may impair their performance;
  • Automatically audit the use of privileges;
  • Automatically audit privileged changes to identify privilege abuses;
  • Provide advanced PAM solutions;
  • Reduce cyber risks;
  • Bring organizations into compliance with audit criteria and standards such as HIPAA, PCI DSS,
  • ISO 27001, and Sarbanes-Oxley.

Conclusion

In this article, you saw that:

  • Cybersecurity is a set of technologies, procedures, and methods used to prevent cyberattacks;
  • Digital transformation has brought new vulnerabilities to IT structures;
  • Companies should invest in cybersecurity to prevent threats, such as malware, viruses, and phishing;
  • Data protection laws hold organizations accountable for the exposure of sensitive information of their customers, employees, and business partners;
  • Cybersecurity projects are aimed at promoting digital security within any company;
  • There are five types of cybersecurity: critical infrastructure security, application security, network security, cloud security, and Internet of Things (IoT) security;
  • People, processes, and technology stand out among the crucial elements for the success of a cybersecurity project;
  • To define the priorities of cybersecurity projects within a company, one needs to understand the organization’s objectives, find out the reason for each project, determine its value, assess its urgency, detail aspects that interfere with its success, rank projects in order of priority, define how many projects it is possible to execute at a time, share the findings with top management, and work flexibly;
  • The main threats faced by companies are ransomware, phishing, mobile device attacks, attacks using QR Codes, denial-of-service (DDoS) attacks, and LotL and AVT attacks.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.


About Segura®
Segura® strive to ensure the sovereignty of companies over actions and privileged information. To this end, we work against data theft through traceability of administrator actions on networks, servers, databases and a multitude of devices. In addition, we pursue compliance with auditing requirements and the most demanding standards, including PCI DSS, Sarbanes-Oxley, ISO 27001 and HIPAA.

無密碼的未來就在 NordPass

You lightly place your thumb at the bottom of your phone screen and, lo and behold, it’s unlocked instantly. So why can’t we do the same at the bank or when logging in to Twitter or YouTube? Well, soon we’ll be able to do it all. The passwordless future is inevitable and it’s almost here.

At NordPass, we’re thrilled to be creating a passwordless future. But what is passwordless authentication? How does it work? Let’s answer these questions.

Why should we consider going passwordless?

Year after year, we see either “123456” or “password” top our Most Common Passwords List. Millions of people reuse absurdly simple passwords across multiple platforms, even though they are very easy to crack by using a dictionary or brute force attacks. It makes passwords (and the people using them) one of the weakest links security-wise in any company or service.

Weak passwords are just part of the problem. The way we treat passwords is an issue as well. One of the worst password sins that all of us can attest to is reusing passwords. Having a single password to secure multiple accounts is a huge security risk, to put it mildly. In such instances, a single compromised account indicates that all of user’s accounts are essentially compromised as well.

The solution lies in biometric authentication and passkeys, which combined become one of the safest and smoothest passwordless authentication options available.

Passkeys: The key to passwordless authentication

In an age where technology usage continues to rise, the need for secure and efficient authentication methods becomes all the more pressing. Passwords, which have long reigned supreme as a solution for securing online accounts, have over time proven to be unreliable and susceptible to hacking. In turn, many organizations and companies have been looking for new, more efficient, and robust ways to authenticate users.

One organization at the forefront of the effort to go passwordless is the FIDO Alliance. The alliance works with various companies, including NordPass, to develop and promote open standards for passwordless authentication.

According to the FIDO Alliance, the technology set to replace passwords is passkeys. Passkeys are digital credentials that are generated by the user’s device. Usually used in combination with biometric data, such as a fingerprint or facial recognition, to offer an extra layer of security, passkeys provide access to websites and other online services.

What passkeys bring to the table

One of the major advantages of passkeys is that the private key, which is used to generate the passkey, never leaves the user’s device. This makes it almost impossible for attackers to gain access to the key through phishing or other forms of cyberattack. Furthermore, passkeys are almost impossible to hack, making them more secure overall.

quotes

Unlike traditional passwords, passkeys are invisible to the user and are never revealed or entered manually.

Going passwordless will also improve user experience. A fingerprint scanner, for example, is a fast and reliable authentication method. It would also mean that there would be no more password reset procedures — IT departments throughout the world will be very grateful. Also, when it comes to biometric authentication, you don’t need to remember anything. You won’t have any Post-its on the computer screen or notes in your planner. You can’t lose, steal, or forget your fingerprint.

Room for improvement for current passkey-based authentication

Right now, passwordless authentication is gaining major traction among such tech giants as Microsoft, Apple, and Google. All of these companies have been introducing passwordless authentication solutions, and in most instances the solutions include the use of passkeys.

However, current passkey-based solutions have a long way to go. At the moment, these solutions limit users to a single ecosystem, which makes it difficult to share them between, say, an Android user and an iOS user. In addition, the current solutions do not offer any kind of sync with password managers.

But this is where NordPass comes into play. We are currently working on integrating passkeys into your favorite password manager.

Introducing passwordless authentication to NordPass

At NordPass, we’re excited to be at the forefront of the passwordless revolution. And by early 2023, NordPass is set to introduce passwordless authentication both for individuals and businesses.

Passwordless access to NordPass

We are currently working on enabling a passwordless sign-in to NordPass. It will be a faster and simpler process than the one now, since it will require a single biometric confirmation. In simple language, this means that you will be able to access your Nord Account and NordPass with a single tap of a finger. You read it right. No more manually entering your Nord Account and Master Password each time you need to log in. Passwordless access to NordPass is set to significantly improve user experience and overall security.

NordPass passkey storage

All NordPass users will have the ability to save passkeys for any website or app in the encrypted vault and use them to access those online services later. With NordPass, you’ll be able to use, share, and sync passkeys between multiple devices and platforms, whereas many passwordless authentication solutions tend to lack such functionalities. This will make NordPass a single place for all of your digital valuables, including passwords, passkeys, credit cards, and other sensitive information.

Passwordless multi-factor authentication (MFA) for businesses

Password-based authentication is still the industry standard. However, due to the inherent vulnerabilities that come with password-based authentication, most businesses face a variety of cybersecurity risks. To significantly reduce the risk of suffering a phishing or an account takeover attack, businesses need to rethink their security approach with regard to access to endpoint devices such as laptops, desktops, workstations, and mobile devices as well as applications that leverage regular passwords or even single sign-on solutions.

With the introduction of passwordless MFA, we’re looking to help businesses improve their overall security stance by eliminating the need for passwords and introducing an authentication method based solely on biometrics.

Passkey integration for online service providers

The world is already moving rapidly towards a passwordless future. Unfortunately, not everyone can adapt smoothly and efficiently. Many small to medium-sized businesses (SMBs) lack the resources and know-how to implement passkey authentication for their users. However, at NordPass we’re ready to leverage our security expertise to make the transition from passwords to passkeys as smooth as possible. We believe that the frictionless user experience offered by passkeys across multiple platforms and devices, combined with superior security, will help your business increase conversion rates, user engagement, and user satisfaction.

You can expect big things as early as 2023. So stay tuned, and be prepared for the inevitable passwordless future – it’s just around the corner.


About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About Nord Security
The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About Version 2 Digital

Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.